Embrace the Bogeyman - Tactical Fear Mongering for Those Who Penetrate
Tactical fear mongering techniques for penetration testing, exploring the use of bogeymen and psychological tactics to improve security awareness and response in organizations.
Scripting Myself Out of a Job - Automating the Penetration Test with APT2
Learn to automate penetration testing using APT2, enhancing efficiency and effectiveness in identifying security vulnerabilities and potential exploits.
Attackers Hunt Sysadmins - It's Time to Fight Back
Learn defensive strategies for system administrators to protect against targeted attacks and enhance overall security posture.
Make STEHM Great Again
Explore strategies to enhance STEHM (Science, Technology, Engineering, Health, and Mathematics) education and workforce development, addressing challenges and proposing innovative solutions.
So You've Inherited a Security Department - Now What
Practical strategies for new security leaders to assess, prioritize, and improve their department's effectiveness while navigating organizational challenges.
Anti Forensics AF
Explore anti-forensics techniques with int0x80 of Dual Core, delving into methods to counter digital forensic investigations and protect digital privacy.
Scripting Myself Out of a Job - Automating the Penetration Test with APT2
Learn to automate penetration testing using APT2, enhancing efficiency and effectiveness in identifying security vulnerabilities and potential exploits.
Penetration Testing Trends
Explore cutting-edge penetration testing techniques and emerging trends with cybersecurity expert John Strand in this insightful conference talk.
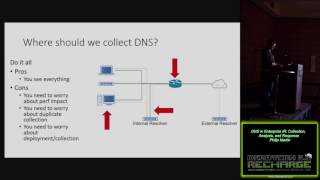
DNS in Enterprise IR Collection Analysis and Response
Explore DNS analysis techniques for enterprise incident response, covering collection tools, infrastructure, and common attack patterns. Learn to leverage RPZ for effective threat mitigation.
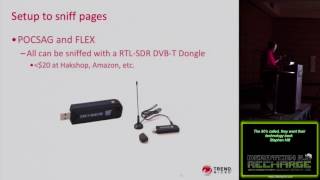
The 90s Called They Want Their Technology Back
Explore the history, protocols, and current uses of pagers, including their role in healthcare. Learn about sniffing and spoofing techniques, potential attacks, and solutions.
Managed to Mangled - Exploitation of Enterprise Network Management Systems
Explore vulnerabilities in enterprise network management systems and learn exploitation techniques for improved security awareness and defense strategies.
Garbage in Garbage Out - Generating Useful Log Data in Complex Environments
Explore effective log data generation in complex environments, focusing on meaningful data, thresholds, and log management systems for improved security and analysis.
Fuzzing Basics - How to Break Software
Learn essential fuzzing techniques to identify software vulnerabilities, enhance security testing skills, and improve overall application robustness.
Web Security for Dummies
Learn essential web security practices, including password management, browser safety, Tor usage, and system patching. Enhance your online protection skills with expert guidance.
Nobody Gets Fired by Choosing IBM but Maybe They Should
Explore strategies for navigating corporate environments, assessing situations, and implementing effective business plans to protect yourself and advance your career.
Attacking EvilCorp - Anatomy of a Corporate Hack
Explore corporate hacking techniques, from enumeration to targeted compromise, with insights on Kerberos exploitation and mitigation strategies for enhanced cybersecurity.
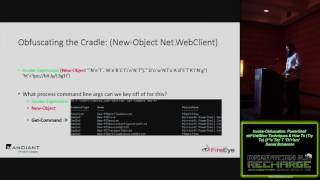
Invoke Obfuscation - PowerShell Obfuscation Techniques and How to Try to Detect Them
Explore advanced PowerShell obfuscation techniques and detection methods to enhance cybersecurity skills and stay ahead of potential threats.
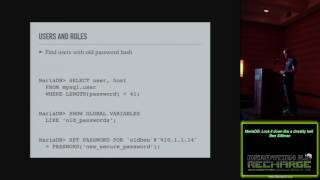
MariaDB - Lock It Down Like a Chastity Belt
Learn essential techniques for securing MariaDB databases, enhancing protection against unauthorized access and data breaches in this comprehensive security-focused session.
Yara Rule QA - Can't I Write Code to Do This for Me?
Learn techniques for efficient Yara rule management, including file organization, rule separation, and quality assurance practices to enhance malware detection capabilities.
Recharging Penetration Testing to Maximize Value
Strategies to enhance penetration testing effectiveness, including improved scoping, collaboration, and reporting techniques for maximizing value and impact in information security.
Java RATS - Not Even Your Macs Are Safe
Explore Java-based Remote Access Tools (RATs) and their potential threats to Mac systems, uncovering vulnerabilities and discussing cybersecurity implications.