Persist It - Using and Abusing Microsoft's Fix It Patches
Explore Microsoft's Fix It patches, their analysis, and potential for system persistence through reverse engineering and exploitation techniques.

The Machines That Betrayed Their Masters
Explore device tracking vulnerabilities and a distributed surveillance framework, including drone-based tracking and geolocation techniques for privacy awareness.
Z - MAKE TROY NOT WAR - Case Study of the Wiper APT in Korea, and Beyond
Análisis detallado del ataque "Wiper" en Corea del Sur en 2013, explorando el vector de infección inicial, examinando muestras de malware y estableciendo conexiones con otros casos de APT desde 2009.
Dude, WTF in My CAN!
Exploring CAN bus security vulnerabilities in modern vehicles, demonstrating remote access and control using a low-cost custom tool, and discussing car forensics for legal applications.
Point-of-Sale Malware
Explore point-of-sale malware threats, attack vectors, and defense strategies in this informative webcast. Gain insights to protect retail systems and customer data.
Owning the Routing Table - Part II
Powerful OSPF attack exploiting protocol ambiguity to control routing tables in autonomous systems. Enables network manipulation, DoS, and unauthorized access to information flows. Multi-vendor fix underway.
Spy-Jacking the Booters
Exposé on "booter" DDoS-for-hire services: their operations, vulnerabilities, and impact. Insights into defending against attacks and the criminal ecosystem behind these illicit services.
Hacking, Surveilling, and Deceiving Victims on Smart TV
Explore vulnerabilities in Smart TVs, including remote surveillance and deception techniques. Learn about potential security risks and attack vectors in this emerging technology platform.
Home Invasion v2.0 - Attacking Network-Controlled Hardware
Explore security risks of network-connected home devices, including potential for physical access and surveillance. Learn about vulnerabilities in smart locks and other IoT products.
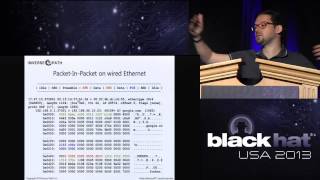
Fully Arbitrary 802.3 Packet Injection - Maximizing the Ethernet Attack Surface
Explore novel Ethernet attack techniques using affordable hardware and custom firmware. Learn about frame manipulations, SFD parsing anomalies, and Ethernet Packet-In-Packet injection for enhanced network security testing.
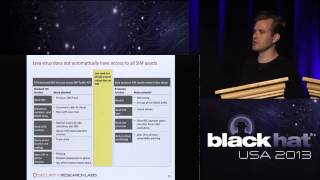
Rooting SIM Cards
Explore SIM card vulnerabilities and their impact on mobile security. Learn about implementation flaws, potential exploits, and the implications for trusted computing in smartphones and embedded devices.
Truncating TLS Connections to Violate Beliefs in Web Applications
Exploring TLS truncation attacks to exploit web application flaws, demonstrating vulnerabilities in authentication systems and their impact on popular platforms like Helios, Microsoft Live, and Google.
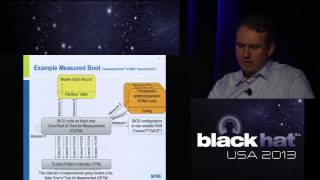
BIOS Security
Explore BIOS security vulnerabilities, SRTM manipulation, and trust subversion techniques. Learn about NIST standards and academic solutions for ensuring BIOS integrity.
Just-In-Time Code Reuse - The More Things Change, the More They Stay the Same
Explore advanced exploit techniques undermining fine-grained ASLR through just-in-time code reuse, demonstrating real-world applications and implications for cybersecurity defenses.
Combating the Insider Threat at the FBI - Real World Lessons Learned
Insider threat detection at FBI: multidisciplinary approach combining psychology, technology, and analytics. Lessons from real-world program implementation, focusing on deterrence, behavioral analysis, and predictive techniques.
Compromising Industrial Facilities From 40 Miles Away
Explore vulnerabilities in industrial wireless automation systems, revealing how key distribution weaknesses can be exploited to compromise critical infrastructure from long distances.
Out of Control - Demonstrating SCADA Device Exploitation
Explore SCADA device exploitation in oil and gas pipelines, examining control systems, vulnerabilities, and potential consequences of security breaches in critical infrastructure.
The Outer Limits - Hacking the Samsung Smart TV
Explore vulnerabilities in Samsung Smart TVs, including remote hijacking, userland rootkits, and surveillance capabilities. Learn about attack surfaces, security flaws, and potential fixes for smart platforms.
KickaaS Security with Automation and Cloud
Explore cutting-edge security automation techniques for cloud environments, focusing on resource management, host protection, and identity control.
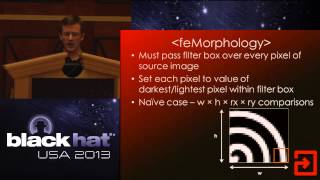
Pixel Perfect Timing Attacks with HTML5
Exploring JavaScript timing attacks to extract sensitive browser data, demonstrating cross-browser vulnerabilities and discussing challenges in fixing these security issues.
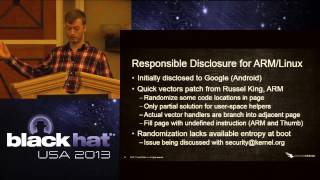
Hacking Like in the Movies - Visualizing Page Tables for Local Exploitation
Visualizing page tables to break ASLR and find vulnerabilities across operating systems. Includes an Android ASLR bypass and insights for Windows, Linux, and iOS.