Darwinism vs Forensics
Explore digital forensics in business, covering technologies analyzed, case studies, and anti-forensics efforts. Learn about metadata, EXIF data, and real-world applications in employment and legal matters.
The Transition Risk Assessment Risk Management
Explore risk assessment, regulatory compliance, and risk management strategies for effective information security, focusing on best practices and tools for organizations.
The Use of Covert Communications in Modern Cyber Attacks
Explore covert communication techniques in cyber attacks, including behavior patterns, encryption, and common methods. Learn to identify and mitigate risks in modern digital threats.
Technical Data Loss Prevention - How to Get the Most for Your Buck
Explore data loss prevention strategies for cloud applications, including risk factors, security broker benefits, and deployment options for protecting enterprise data in SaaS environments.
Insiders are the New Malware
Explore insider threats, data breaches, and effective strategies for protecting sensitive information through access control, data ownership, and risk assessment.
Technical A02 - The Current State of Memory Forensics
Explore memory forensics techniques, acquisition methods, and analysis goals. Learn about Windows 10 memory compression and Virtual Secure Mode impacts on forensic investigations.
Software Bill of Materials and Supply Chain with the Yocto Project
Explore software supply chain security using the Yocto Project, focusing on generating and utilizing Software Bill of Materials (SBOM) for enhanced transparency and risk management.
Designing Secure APIs
Improve API security design using tools and guidelines. Learn about JSON complexities, schemas, JWTs, rate-limiting, and enforcing rules with OpenAPI and static analysis tools.
Cybersecurity Zero to Hero with CyberChef
Learn to perform complex cybersecurity tasks using CyberChef, a user-friendly web app that simplifies malware analysis and streamlines workflows for both beginners and experienced analysts.
Binee - Complete Emulation of Advanced Malware
Explore advanced malware emulation with Binee, a Windows Process emulator. Learn to create detailed memory models, mimic OS kernels, and gather dynamic analysis data for reverse engineering and vulnerability research.
The Past, Present, and Future of Cross-Site - Cross-Origin Request Forgery
Explore the evolution of Cross-Site Request Forgery attacks, their impact on applications, and effective defense strategies for both traditional and API-based systems.
Securing the OAuth and OpenID Connect Front-Channel
Explore Pushed Authorize Requests (PAR) in OAuth, enhancing security by adding client authentication and removing request parameters from URLs, improving user experience and enabling new scenarios.
Houston, We Have a Problem - Analyzing the Security of Low Earth Orbit Satellites
Explore the first public security analysis of Low Earth Orbit satellites, uncovering vulnerabilities and potential exploits in these crucial space-based systems.
Guardians of the AI Era - Navigating the Cybersecurity Landscape of Tomorrow
Explore the future of cybersecurity in the AI era, examining challenges and opportunities for professionals. Learn to adapt and innovate in a rapidly evolving technological landscape.
A Manufacturer's Post-Shipment Approach to Fend-Off IoT Malware in Home Appliances
Explore a manufacturer's strategy to protect home appliances from IoT malware post-shipment, addressing rapid attack cycles and complex malware capabilities based on 5 years of IoT threat intelligence.
What Does an LLM-Powered Threat Intelligence Program Look Like?
Explore the impact of large language models on cyber threat intelligence programs, focusing on expanded capabilities and potential return on investment for organizations.
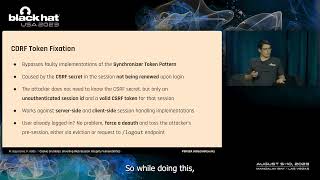
Cookie Crumbles - Unveiling Web Session Integrity Vulnerabilities
Explore web session integrity vulnerabilities, focusing on cookie security mechanisms and their real-world implications. Learn about bypassing protections and potential attacks on web applications.
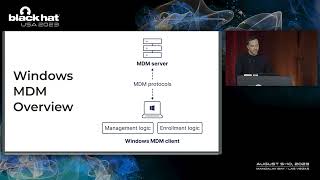
Windows Agentless C2 - Abusing the MDM Client Stack
Uncover vulnerabilities in Windows MDM client stack for agentless Command and Control. Explore MDM infrastructure, enrollment, and management protocols for potential abuse in device management.
Building Native Extensions - This Could Take A While
Explore techniques for building native gem versions, improving installation speed and reliability. Learn about toolchains, trust considerations, and deploying pre-compiled packages.
Network Security - What About the Data
Explore network security beyond firewalls, focusing on data protection strategies like role-based access, DLP, and data classification to safeguard valuable information assets.
ProbeSpy - Tracking Your Past, Predicting Your Future
Explore WiFi tracking techniques, behavioral profiling, and positioning systems. Learn about privacy implications and potential vulnerabilities in wireless networks.