Reverse Engineering and Exploiting Font Rasterizers - The OpenType Saga
Explore critical vulnerabilities in OpenType font handling across popular software, revealing potential for arbitrary code execution and bypassing exploit mitigations. Learn about reverse-engineering techniques and in-depth vulnerability analysis.
Passive IPS Reconnaissance and Enumeration - False Positive Abuse
Explore techniques for enumerating network defenses by exploiting false positives in Intrusion Prevention Systems, revealing valuable information about security measures to potential attackers.
Dark Fairytales from a Phisherman Vol II
Explore advanced phishing techniques, leveraging tools like Phishing Frenzy and BeEF for effective campaigns. Learn from real-world statistics and engaging hacking stories to enhance your cybersecurity skills.
Indicators of Compromise - From Malware Analysis to Eradication
Learn to identify, analyze, and eradicate unknown malware in corporate networks using freely available tools. Gain practical skills for effective threat detection and response.
Introduction to Reverse Engineering C++
Learn techniques for reverse engineering C++ programs, including analyzing compiled code, understanding memory layouts, and identifying key structures. Gain practical skills for software analysis and security research.
Analyzing Malicious Office Documents
Learn techniques to analyze malicious Microsoft Office documents using Python tools like oledump and YARA rules. Hands-on exercises guide you through step-by-step analysis without requiring Office software.
Stegosploit - Drive by Browser Exploits Using Only Images
Innovative technique encoding browser exploits in images, combining steganography and polyglots for undetectable delivery. Explores implementation, challenges, and implications for cybersecurity.
Smart Muttering - A Story and Toolset for Smart Meter Platform
Explore smart meter security vulnerabilities and a new open-source framework for embedded device analysis. Learn about critical infrastructure risks and tools for assessing obscure networks and protocols.
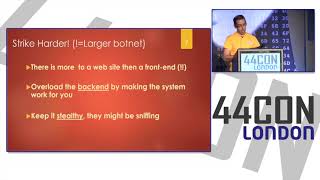
DDoS Mitigation Epic Fail Collection
Explore 10 critical DDoS mitigation failures, their technical details, and recommended solutions. Learn from industry leaders' mistakes to enhance your defense strategies against sophisticated attacks.
Meaningful Measurement - It’s About Time We Got This Right
Explores flaws in current cybercrime metrics, advocating for standardized, business-focused measurements to improve threat intelligence and risk analysis across all enterprise sizes.

Automated Extraction of Configuration and Payloads from Sophisticated Malware
Automated malware analysis system for extracting payloads, configurations, and indicators from sophisticated malware, reducing time and skill requirements for threat intelligence.
Attacks on SAP HANA Platform
Explore vulnerabilities in SAP HANA platform, including on-premise, cloud, and IoT deployments. Learn attack vectors, technical details, and prevention strategies for securing critical business data.
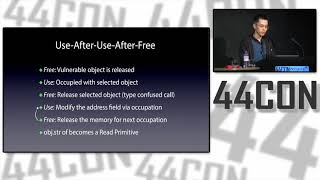
Leverage One-shot UAF to a Minigun
Exploración de técnicas avanzadas de explotación de vulnerabilidades Use-After-Free en Adobe Flash, incluyendo el método UAUAF para obtener acceso completo a la memoria y ejecución de código arbitrario.
Ways to Brick Your Hardware
Explore common hardware hacking pitfalls, recovery methods, and prevention strategies. Learn from experts' experiences to avoid damaging your projects and gain confidence in hardware experimentation.
Trusts You Might Have Missed
Demystifying domain trusts: Enumeration, visualization, and exploitation techniques for red teams. Learn to leverage trust relationships for domain takeover without exploits.
Light at the End of the Tunnel - Hope for Team Defence
Exploring emerging strategies and positive developments in cybersecurity defense, offering hope and practical solutions for improving security posture in an offense-dominated landscape.
Software Defined Networking - SDN Security
Explore SDN security implications, attack surfaces, and vulnerabilities with live exploit demos. Learn about efforts to enhance SDN controller security and future developments.
Exploiting 64 Bit IE on Windows 8.1 - The Pwn2Own Case Study
Detailed exploration of vulnerabilities and exploit techniques used to compromise 64-bit Internet Explorer on Windows 8.1, including ASLR & CFG bypass and sandbox escape, as demonstrated at Pwn2Own 2015.
Responsible Disclosure - Who Cares
Explore real-world experiences of security researchers attempting responsible disclosure, highlighting challenges, vendor responses, and lessons learned in vulnerability reporting.
Barbarians at the Gateway - An Examination of the Attacker’s Tool Box
Explore DDoS attack tools, methods, and motivations. Gain insights into attacker patterns and progression for better protection against cyber threats.
Toppling Domino - Testing Security in a Lotus Notes Environment
Explore Lotus Notes/Domino security vulnerabilities and learn effective penetration testing techniques for web servers, native servers, and client-side exploits.