Architecting a Security Program for the Future
Interactive workshop on risk-based security management, using role-playing to assess, prioritize, and mitigate risks in a fictional company. Provides practical tools and strategies for modern cybersecurity challenges.
Don't Touch Me That Way
Explore iOS fingerprint API security: correct usage, vulnerabilities, and potential attacks. Hands-on demo with code, tools, and test applications for mobile app developers and security professionals.
It's 10pm, Do You Know Where Your Access Keys Are?
Strengthen AWS infrastructure against attacks: Learn to secure environments, monitor for threats, and recover from incidents using AWS tools like Config, CloudWatch, and IAM.
LangSec for the Masses
Explore AWS security best practices, including hardening, monitoring, and recovery techniques. Learn to protect your infrastructure against common attacks and respond to security breaches effectively.
Leveling Up Your Bug Bounty Program
Explore bug bounty programs: benefits, pitfalls, and implementation strategies. Learn from Indeed.com's experience in leveraging diverse skills to enhance security and uncover critical vulnerabilities.
Be Ready for BeyondCorp - Enterprise Identity, Perimeters and Your Application
Explore BeyondCorp's enterprise security model, focusing on user and device authentication, access control, and implementation in open-source web applications using tools like SAML and Django.
Could a Few Lines of Code Mess It All Up
Explores risks of open source dependencies, revealing potential vulnerabilities in popular packages and discussing impacts on app security. Offers insights on mitigating risks in hybrid development.
Slippery When Wet - A Dirty Little Pigment Story
Explore the paradox of digital signatures vs. wet ink, examining trust issues, security concerns, and the future of identity verification in everyday transactions.
IOT and AppSec
Explore the intersection of Internet of Things (IoT) and application security, examining potential vulnerabilities and strategies for safeguarding connected devices and systems.
Infosec in the New World Order - Rugged DevOps and More
Explore the intersection of information security and DevOps with Gene Kim, focusing on rugged DevOps principles and their impact on modern cybersecurity practices.
Social Engineering
Learn about social engineering from David Hughes in less than an hour with LASCON's online material. Less than hour.
Hacking and Defending iPhone Application
Explore iPhone app vulnerabilities and defense strategies through hands-on demonstrations and practical techniques for securing iOS applications.
Network Attack Collaboration
Explore network attack collaboration techniques with Raphael Mudge. Learn strategies for coordinating and executing effective penetration testing in complex environments.
Automated vs. Manual Security - You Can't Scan for The Stupid
Explore the limitations of automated security tools and the importance of manual testing in identifying vulnerabilities that scanners miss, particularly those caused by human error.
Effortless, Agentless Breach Detection in the Enterprise - Token All the Things!
Discover innovative techniques for detecting network breaches using honeytokens. Learn about Canarytokens and new methods to set tripwires without agents or hardware, improving your network security.
Frictionless Security
Explore automated, non-intrusive security integration into company infrastructure. Learn from successes, failures, and future improvements in implementing frictionless security programs.
Hunting Asynchronous Vulnerabilities
Explore techniques for uncovering hidden vulnerabilities in backend systems using exploit-induced callbacks. Learn to detect and exploit asynchronous issues across various technologies and platforms.
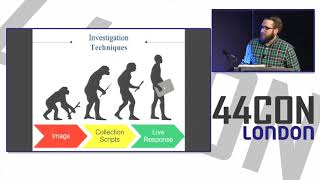
Old Dog, New Tricks - Forensics With PowerShell
Explore PowerForensics: a PowerShell-based toolset for live digital forensics and incident response, enabling efficient investigation of advanced cyber threats without system imaging.
Attacking VxWorks - From Stone Age to Interstellar
Explore vulnerabilities in VxWorks, a real-time operating system, from historical exploits to cutting-edge attack techniques. Gain insights into securing critical infrastructure and embedded systems.
Forging the USB Armory
Explore the development of the USB armory, an open-source hardware device for security applications. Learn about its architecture, security features, and potential uses as a trusted USB device.
Hackers in the Wire and Drones Oh My!
Explore powerful, inexpensive penetration testing using ARM-based devices, from wired/wireless dropboxes to flying drones. Control actions remotely, with devices like BeagleBone Black and Raspberry Pi 2.