Hack Out of the Box - Discovering 10+ Vulnerabilities in VirtualBox
Discover 10+ VirtualBox vulnerabilities through custom fuzzing techniques. Learn about attack surfaces, exploit primitives, and see a live box escape demonstration.
A Hipster History of CORS
Explore the evolution of CORS, its historical context, and modern cross-origin standards. Gain insights into web security and learn how to design secure web applications effectively.
Don't Get Owned by Your Dependencies
Explore innovative techniques for mitigating memory safety vulnerabilities in third-party C libraries, focusing on Firefox's lightweight in-memory sandboxing approach and the RLBox framework for efficient, secure application development.
SIEM There, Done That - Rising Up in the SecOps Revolution
Explore the future of cybersecurity through automation and intelligence, moving beyond traditional SIEM solutions to address modern SecOps challenges and usher in a new era of protection.
The New Ground Truth for Security
Explore how infrastructure can establish a new ground truth for cybersecurity professionals, addressing misinformation and advanced threats in today's complex digital landscape.
Threat Response Needs New Thinking - Don't Ignore This Key Resource
Discover innovative approaches to threat response, focusing on leveraging your network as a crucial asset for real-time attack detection and enhanced resilience against cybersecurity challenges.
The Looming Identity Crisis
Explore the challenges of securing identity in the AI era and discover innovative solutions to prevent an impending crisis in cybersecurity.
Giovanni Cruz - Atacando VoIP: un paraíso - Ekoparty 2010
Exploración de vulnerabilidades y técnicas de ataque en sistemas VoIP, revelando riesgos de seguridad y estrategias de protección en comunicaciones de voz sobre IP.
Network Based Detection of PE Structural Anomalies
Explore network-based detection techniques for identifying structural anomalies in Portable Executable (PE) files, enhancing cybersecurity defenses against malware threats.
Turning an Incident Report into a Design Issue with TLA+
Explore how modeling-driven techniques and TLA+ can enhance postmortem analysis, uncover root causes, and improve system design in distributed database architectures.
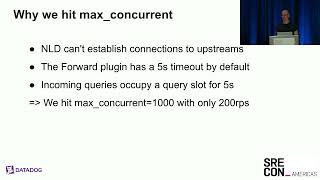
Logs Told Us It Was DNS, It Looked like DNS, It Had to Be DNS, It Wasn't DNS
Unraveling a complex Kubernetes incident: from DNS suspicions to kernel-level insights, culminating in a surprising three-line code fix. Learn debugging techniques and unexpected system behaviors.
An Organizational Response to Incidents - Designing for Smooth Coordination
Strategies for effective incident response coordination, focusing on follower roles and organizational preconditions. Insights to improve communication and collaboration during software outages.
Incident Commanders to Incident Analysts - How We Got Here
Explore the transition from incident management to incident analysis, highlighting the distinct skills required and the value of post-incident learning for driving meaningful organizational change.
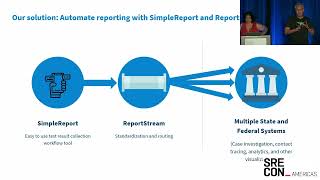
SRE's Critical Role in the COVID-19 Pandemic Response in Government
Explore how SREs in government navigated regulatory constraints to rapidly deploy critical software services during the COVID-19 pandemic, showcasing their adaptability and incident response skills.
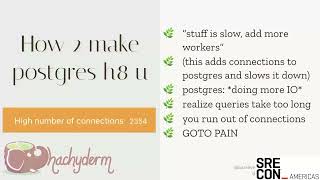
Hacking the Pachyderm - Scaling Servers and People
Scaling a social platform from 700 to 30,000 users in one month: technical challenges, decision-making, and team dynamics during rapid growth and migration without data loss or burnout.
Far from the Shallows - The Value of Deeper Incident Analysis
Explore the value of in-depth incident analysis in SRE, moving beyond surface-level metrics to uncover hidden insights and improve system reliability through qualitative investigation.
Human Observability of Incident Response
Practical advice on improving incident response outcomes by understanding the human element. Explores coordination, learning, and socio-technical systems in incident management.
Warding against the Dark Arts - Crafting a Defense Strategy against Botnet DDoS Attacks
Learn strategies to defend against large-scale DDoS attacks, focusing on performance gains, service hardening, and understanding real-user traffic for improved availability and comprehensive protection.
Adversarial Data Mining - Big Data Meets Cyber Security
Explore adversarial data mining techniques in cybersecurity, focusing on big data challenges and solutions for detecting and mitigating threats in complex digital environments.
Practical Censorship Evasion Leveraging Content Delivery Networks
Explore innovative techniques for bypassing internet censorship using Content Delivery Networks, presented by researchers from UMass Amherst at a major cybersecurity conference.
All Your DNS Records Point to Us - Understanding the Security Threats of Dangling DNS Records
Explore security threats of dangling DNS records, understanding vulnerabilities and potential exploits in domain name systems.