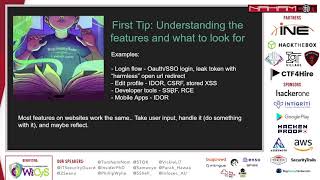
Putting Your Mind to It - Bug Bounties for 12 Months
Insights into successful bug bounty hunting strategies and experiences over a 12-month period, focusing on mindset, persistence, and effective techniques for finding vulnerabilities.
Hacking IIS
Explore advanced IIS hacking techniques, including HTTPAPI 2.0 assets, VHost hopping, local file disclosure, and complex XXE vectors. Learn to leverage tools like DNSpy for effective web application security testing.
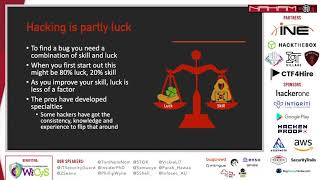
Learn to Hack - Choose a Target - Get a Bounty
Practical guide to overcoming initial challenges in bug bounty hunting, covering automation, reconnaissance, common vulnerabilities, and essential hacking skills for beginners.
Just Give Me a Trial, Please
Overcoming obstacles in hacking enterprise software for bug bounty programs: experiences and advice on tackling third-party vendor products and obtaining trial access.
Using Chromedp to Hunt for Prototype Pollution
Learn to use Chromedp in Go for detecting prototype pollution at scale, enhancing your ability to identify and address this client-side security vulnerability efficiently.

Microsoft Ignite 2021 - Empowering Hybrid Work and Innovation
Explore the future of hybrid work, cloud innovation, and cybersecurity with Satya Nadella. Learn to empower teams, build next-gen apps, and protect your organization in a changing digital landscape.
Microsoft Ignite Highlights for Latin America - Spanish Session
Resumen de los principales anuncios y aspectos destacados de Microsoft Ignite, presentado por expertos y ejecutivos de Microsoft América Latina en español.
The Invasion of Bad Drivers
Explore vulnerabilities in peripheral drivers, including a 0day discovery, exploitation techniques, and mitigation strategies. Learn about common security risks and how to protect your system.
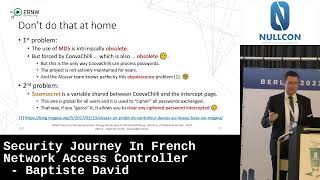
Security Journey in French Network Access Controller
Exploration des vulnérabilités des contrôleurs d'accès réseau, en particulier Alcasar. Analyse des failles de sécurité et des moyens de contournement, avec focus sur l'authentification et la protection des mots de passe.
Why Not Having Control Over Your Data is a Ticking Time Bomb
Explore the risks of data control loss and the potential of decentralized credentialing in the digital age. Learn how to protect your personal information and navigate the future of data management.
Burnout Culture is a Cyber Risk
Discover how burnout culture increases cyber risk and why human-centered approaches are crucial for organizational resilience and cybersecurity improvement.
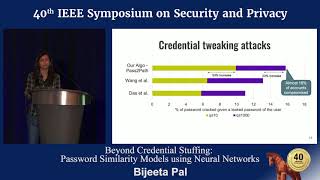
Beyond Credential Stuffing - Password Similarity Models Using Neural Networks
Explore advanced password security using neural networks to model similarities, revealing vulnerabilities in current systems and proposing innovative defenses against targeted attacks.
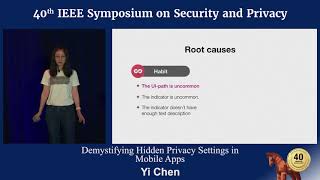
Demystifying Hidden Privacy Settings in Mobile Apps
Uncover hidden privacy settings in mobile apps, learn about their impact on user data sharing, and explore strategies for improving privacy control usability.
Characterizing Pixel Tracking through the Lens of Disposable Email Services
Explores disposable email services and email tracking, revealing security risks and prevalent third-party tracking methods. Analyzes a large-scale dataset to uncover tracking ecosystem dynamics.
PrivKV - Key Value Data Collection with Local Differential Privacy
Explores local differential privacy for key-value data collection, proposing PrivKV, PrivKVM, and PrivKVM+ solutions to improve estimation accuracy while preserving user privacy in distributed data collection.
EmPoWeb - Empowering Web Applications with Browser Extensions
Explores security risks of browser extension APIs, revealing how web apps can exploit them to bypass SOP, access sensitive user data, and perform privileged actions on users' devices.
Fidelius - Protecting User Secrets from Compromised Browsers
Innovative architecture using trusted hardware enclaves to protect sensitive user data during web browsing, even in fully compromised environments. Offers secure form data, JavaScript, XMLHttpRequests, and storage solutions.
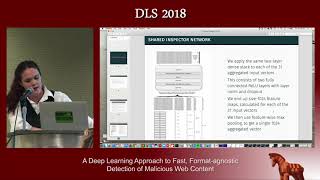
A Deep Learning Approach to Fast, Format-Agnostic Detection of Malicious Web Content
Innovative deep learning method for detecting malicious web content, operating on token streams from static HTML files. Achieves high accuracy and speed without complex parsing or emulation.
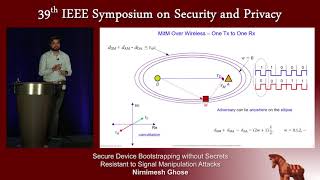
Secure Device Bootstrapping without Secrets Resistant to Signal Manipulation Attacks
Explores VERSE, a physical-layer group message integrity verification primitive for secure wireless device bootstrapping without prior associations, addressing MitM attacks and key management challenges.
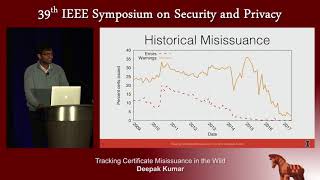
Tracking Certificate Misissuance in the Wild
Explore certificate misissuance trends, introducing ZLint tool to analyze CA errors. Discover improvements, persistent issues, and correlations with mismanagement in the Web PKI ecosystem.
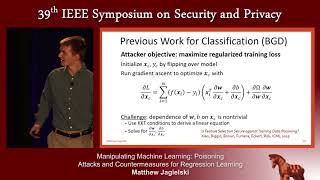
Manipulating Machine Learning - Poisoning Attacks and Countermeasures for Regression Learning
Explore poisoning attacks on linear regression models, their impact on automated decisions, and effective countermeasures. Learn about optimization frameworks and statistical attacks in machine learning security.