Hunting Supply Chain Threats Using Anomaly Detection
Explore a case study on detecting supply chain threats through anomaly detection in Cloud API logs, offering insights into advanced cybersecurity techniques.
I Hope This Sticks - Analyzing ClipboardEvent Listeners for XSS
Explore ClipboardEvent listeners as potential XSS vectors in web applications. Learn techniques for identifying and exploiting vulnerabilities to enhance your offensive security skills.
Story of an RCE on Apple Through Hot Jar Swapping
Discover how Frans Rosen achieved remote code execution on Apple through hot jar swapping. Learn about the research, exploit, and analysis behind this impressive security finding.
Reversing Web Assembly
Explore techniques for reversing Web Assembly (wasm) in this offensive security talk. Learn key strategies and tools for analyzing and understanding wasm code.
Blackbox Monitoring for Timely Bug Detection
Discover effective blackbox monitoring techniques for timely bug detection in web applications. Learn task-based hybrid approaches, freshness indicators, and risk markers for improved security.
A Heaven for Hackers - Breaking Web Security Virtual Appliance
Explore web security vulnerabilities and hacking techniques through hands-on demonstrations, focusing on methodology, enumeration, and exploitation of common weaknesses in web applications.
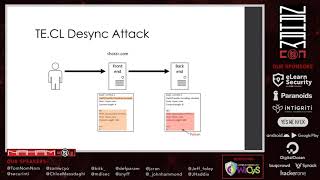
Practical Attacks Using HTTP Request Smuggling
Explore practical HTTP request smuggling attacks, including CL.TE/TE.CL desync techniques, testing methods, and real-world examples. Learn to exploit vulnerabilities for session stealing and response queue poisoning.
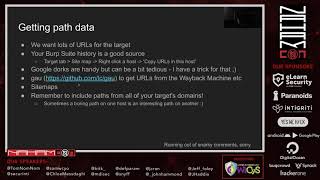
Who, What, Where, When, Wordlist
Explore techniques for creating and utilizing effective wordlists in cybersecurity, including target-specific lists, data processing, and practical applications for bug hunting.
The Pwning Machine - An Easy to Setup Pwning Station
Explore the Pwning Machine, an easy-to-setup hacking environment. Learn about its features, including a basic server, markdown editor, and pipeline runner for efficient cybersecurity tasks.
How to Use Amass Efficiently
Comprehensive guide on maximizing Amass tool for efficient information gathering and reconnaissance in cybersecurity, presented by expert Jeff Foley at NahamCon2020.
Scaling Up - Automated Attack Surface Discovery with Intrigue Core
Explore automated attack surface discovery using Intrigue Core for efficient cybersecurity scaling. Learn techniques to identify vulnerabilities and enhance your security posture.
You've Got Pwned - Exploiting E-Mail Systems
Explore email system vulnerabilities and exploitation techniques in this informative talk by @securinti, covering key security risks and potential attack vectors.
The Bug Hunter's Methodology v4.0 - Recon Edition
Comprehensive guide to reconnaissance techniques for bug bounty hunters, covering advanced methods to identify vulnerabilities and expand attack surfaces in web applications.
Finding XSS on Apple.com and Building a Proof of Concept to Leak Your PII
Discover how to find XSS vulnerabilities on high-profile websites and create effective proof-of-concept exploits to demonstrate potential data leakage risks.
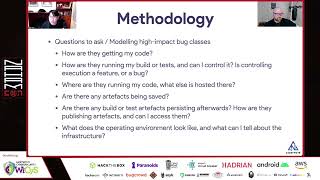
Continuous Intrusion - Hacking CI Systems
Explore techniques for exploiting vulnerabilities in Continuous Integration systems, focusing on security risks and potential attack vectors in the software development pipeline.
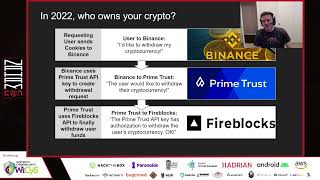
Breaking Into Cloud Wallets - Hacking Crypto Web Apps
Explore cloud wallet vulnerabilities and crypto web app hacking techniques in this talk by @samwcyo, covering blind XSS, SQL injection, and account takeovers in the cryptocurrency ecosystem.
Effectively Finding Vulnerabilities by Debugging the Source Code
Discover effective techniques for identifying vulnerabilities through source code debugging. Learn to enhance your bug hunting skills and improve your ability to find security flaws in software.
Recon Fundamentals by Example
Explore recon fundamentals through practical examples in this offensive security talk. Learn essential techniques for effective reconnaissance in bug bounty and penetration testing.

Finding 0days in Enterprise Web Applications
Explore techniques for finding 0-day vulnerabilities in enterprise web applications, focusing on HCL Digital Experience, Solarwinds Web Help Desk, and Sitecore's Experience Platform.
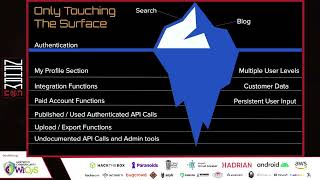
The Bug Hunter's Methodology - Application Analysis v1
Comprehensive guide to application analysis for bug hunters, covering advanced techniques, tools, and methodologies to identify vulnerabilities and maximize bounty rewards.
Career and Community Building with Bug Bounties
Panel discussion on leveraging bug bounties for career growth, knowledge expansion, and community building in infosec. Experts share insights on how bug bounties have impacted their professional journeys.