East vs West - How The Coasts Approach Information Security Differently
Explore the contrasting approaches to information security between Wall Street and Silicon Valley, uncovering valuable insights for professionals across various security roles.
Bootstrapping Security
Practical strategies for implementing effective cybersecurity on limited budgets, covering tools, techniques, and cost-saving approaches for organizations with financial constraints.
The Voight-Kampff Test for Discovering Web Application Vulnerabilities
Explore techniques to differentiate between human-discovered and machine-detected web app vulnerabilities, with insights on manual setup, chain exploits, and real-world case studies.
Security, Politics, Neutrality, and Protecting Users
Explore the intersection of security, politics, and tech neutrality, examining how these factors impact user protection and the evolving role of technology companies in society.
Break Crypto like a Pro
Explore common cryptographic vulnerabilities and learn practical exploitation techniques in this engaging talk on breaking crypto systems effectively.
Non-Political Security Learnings from the Mueller Report
Explore forensic evidence from the Mueller Report to understand network compromises, access methods, and defensive strategies for organizations.
RIS-ky Business - Exploiting Medical Information Systems
Explore medical device security, protocols, and system architecture. Learn how attackers can exploit vulnerabilities to access patient information in healthcare settings.
Serverless Osquery Backend and Big Data Exploration
Explore serverless osquery backend deployment, scalability challenges, and large-scale data processing for enhanced intrusion detection and endpoint management.
Real Time Vulnerability Alerting by Using Principles from the United States Tsunami Warning Center
Learn to combat vulnerability fatigue using data analytics principles from the US Tsunami Warning Center for real-time, high-impact security alerts.
Purple is the New Black - Modern Approaches to Application Security
Explore modern application security approaches combining defense, offense, automation, and continuous learning for various app types, including zero trust, supply chain, and microservices.
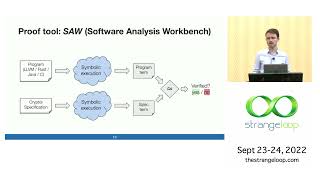
Formally Verifying Everybody's Cryptography
Explore formal verification in cryptography: its application, challenges, and impact on securing real-world systems through mathematical reasoning and advanced techniques.
Prevent Phishing & Impersonation
Explore innovative approaches to prevent phishing and impersonation attacks in digital systems. Learn about trust-based identity models and a prototype address book that enhances security without compromising usability.
Redback - Advanced Static Binary Injection
Explore advanced static binary injection techniques to insert external code into executables, modifying run-time behavior. Learn from experts about this powerful yet underutilized method.
Store-to-Leak Forwarding - There and Back Again
Explore store-to-leak forwarding attacks, their evolution since Meltdown, and implications for data security in modern processors. Learn about new vulnerabilities and mitigation strategies.
Back to the Future - Cross-Protocol Attacks in the Era of 5G
Explore vulnerabilities in mobile network protocols across generations and learn about cross-protocol attacks in 5G networks, presented by security expert Sergey Puzankov.
Page Cache Attacks - Microarchitectural Attacks on Flawless Hardware
Explore microarchitectural attacks on flawless hardware, focusing on page cache vulnerabilities. Learn about state-of-the-art techniques, countermeasures, and implications for system security.
From an URGENT - 11 Vulnerability to a Full Take-Down of a Factory, Using a Single Packet
Demonstration of exploiting URGENT/11 vulnerabilities in industrial controllers to take over an entire factory with a single packet, highlighting cybersecurity risks in automated systems.
Making an Impact from India to the Rest of the World by Building and Nurturing Women Infosec Community
Explore the journey of InfoSecGirls, a community empowering women in cybersecurity, from its origins in India to its global impact, fostering diversity and inclusion in the tech industry.
Demystify Today's Binary Disassembling and How Modern ABI Makes it Easier
Explore modern binary disassembling techniques and tools, understanding their strategies, challenges, and how modern ABI enhances the process. Learn about evaluation results and new approaches in this field.
Win the 0-Day Racing Game Against Botnet in Public Cloud
Explore techniques for capturing 0-day attack payloads automatically in public cloud environments, with real-world examples and insights on model performance and monitoring strategies.
The Inside Story - There Are Apps in Apps and Here Is How to Break Them
Explore instant app architecture and attack models, uncovering vulnerabilities in this popular app format. Learn about security implications and potential exploits in click-to-play designs.