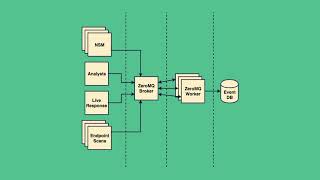
Beyond AV - Detection-Oriented File Analysis
Explore advanced file analysis techniques for enhanced threat detection, focusing on Strelka's features and applications in enterprise security.
All Your Containers Are Belong to Us
Explore container orchestration security risks, focusing on exposed management nodes and APIs. Learn implications, recommendations, and see demonstrations of potential exploits in popular platforms.
Friend or Replicant - How Attackers Automate and Disguise Themselves
Explore the tactics behind fake online accounts, from creation to manipulation, and learn how attackers exploit various vectors to influence the digital landscape at scale.
Two-Faces of WASM Security
Explore WebAssembly's dual nature: its potential for malicious use in sophisticated attacks and the vulnerabilities it introduces, presenting challenges for both users and web developers.
Cats in My Certificate Transparency Logs
Explore Certificate Transparency logs: their purpose, functionality, and potential misuse. Learn about SCTs, public keys, and novel applications, including finding cat pictures online.
Hacking with a Heads Up Display
Explore OWASP ZAP's Heads Up Display, a browser-integrated security testing tool designed to make security testing more accessible and user-friendly for developers, QA, and hackers.
Attacking Deep Learning-Based NLP Systems
Explore vulnerabilities in deep learning NLP systems, focusing on word embeddings. Learn to manipulate training data and inject into real-world applications, with emphasis on security implications.
Arcades and Audits - What Gaming Can Do for Your Security Posture
Explore gamification techniques for enhancing security audits and disaster preparedness, combining arcade game benefits with operational resilience strategies for engaging and effective training.
High Performance VM Introspection
Innovative approach to enhance VM introspection performance using in-guest agent and virtualization exception mechanism, addressing security challenges in hypervisor-based solutions.
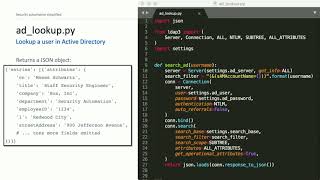
Security Automation Simplified
Practical guide to implementing security automation using existing tools and basic coding, demonstrating how to streamline SecOps processes and save time without relying on expensive products.
Offensive Javascript Techniques for Red Teamers
Explore advanced JavaScript techniques for red team operations, including browser exploitation, network reconnaissance, and crafting payloads to target internal vulnerabilities quickly and effectively.
Goldilocks and the Three ATM Attacks
Explore three ATM attack case studies, from poor security to zero-day exploits, revealing vulnerabilities and prevention strategies in modern ATM systems.
Back to the SOCless Future
Explore Twilio's journey towards automated security operations, featuring insights on scalable 24/7 monitoring and a serverless automation framework for effective threat response.
How to Lose a Container in 10 Minutes
Explore container security challenges, common deployment mistakes, and real-time vulnerabilities in cloud environments with practical examples and live demonstrations.

Ferris Bueller's Guide to Abuse Domain Permutations
Explore techniques for detecting and defending against domain permutation attacks, including homoglyphs and typo-squats, to enhance cybersecurity and prevent fraud.
Vendor Security - Where Our Data Goes We Follow
Explore vendor security challenges and solutions with experts from diverse companies. Learn about assessment methods, influencing vendors, scaling programs, and predicting security maturity in partner organizations.
How to Kill an AWS Access Key
Learn to eliminate static AWS Access Keys using Security Token Service, SAML, and Identity Providers for enhanced cloud security and short-lived credentials.
Visualizing Security
Explore data analysis and visualization techniques for security through real-world examples, covering various chart types and data transformation methods to enhance security insights.
Phishy Little Liars - Pretexts That Kill
Discover advanced techniques for creating specialized, custom pretexts in penetration testing, using target-specific data to enhance effectiveness and avoid detection.
Securing Coinbase's Edge Payments Infrastructure
Explore secure payment networks, KYC/AML practices, and fraud prevention in cryptocurrency exchanges. Learn about Coinbase's strategies for protecting transactions and ensuring regulatory compliance.
When GDPR and CCPA Strike - Silver Lining for Security Teams in Data Protection Clouds
Explore how data protection laws like GDPR and CCPA can benefit security teams, informing risk modeling, securing buy-in, and reducing liability exposure for organizations.