Breaking Samsung's ARM TrustZone
Explore Samsung's TrustZone vulnerabilities and learn techniques to exploit trusted components, execute high-privilege code, and bypass security measures in ARM-based systems.

Conducting a Successful False Flag Cyber Operation - Blame it on China
Explore techniques for conducting false flag cyber operations, including persona creation, toolchain analysis, and exploitation methods. Learn to understand and counter attribution attempts in cybersecurity.

Exploiting Qualcomm WLAN and Modem Over The Air
Explore Qualcomm WLAN and Modem vulnerabilities, focusing on firmware exploitation, isolation breaches, and over-the-air control techniques. Gain insights into real-time debugging and mitigation strategies.
Death to the IOC - What's Next in Threat Intelligence
Explore ML-driven automation for cyber threat intelligence, including custom entity extraction and attack pattern identification, moving beyond traditional IOC approaches.

WebAuthn 101 - Demystifying WebAuthn
Demystifying WebAuthn: Learn about its use cases, implementation, and future developments in web authentication, essential for any service implementing user login.
Fantastic Red-Team Attacks and How to Find Them
Explore prevalent gaps in organizational defenses through Atomic Red Team testing. Learn to identify and analyze complex attack patterns using Event Query Language and data analysis techniques.
Unraveling the Recipe for Resilient Enterprise Security Operations
Explore strategies for resilient enterprise security operations, focusing on informed decision-making during critical incidents like ransomware attacks. Learn about risk indicators and active defense techniques.
The Metaverse of Vulnerability
Explore the cybersecurity challenges and vulnerabilities in the metaverse, from technical issues to operational risks, and learn proactive strategies to address these concerns.
Mitigating Russian State-Sponsored Cyber Threats to US Critical Infrastructure
Explore Russian state-sponsored cyber threats to US critical infrastructure, learn mitigation strategies, and understand FBI resources for enhancing cybersecurity preparedness.
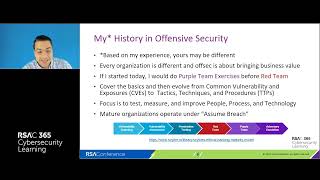
Intro to Purple Team - Cyber Threat Intelligence, Attack, Detect, Respond
Learn to build an effective Purple Team program, covering threat intelligence, attack emulation, and detection engineering using MITRE ATT&CK as a common language for improved cybersecurity.
Making Security Simpler
Experts discuss simplifying security through built-in features, automation, and improved architectures, aiming to reduce resource needs and enhance protection for various organizations.
Sherlock Holmes - Finding Threats We Didn’t Know We Were Looking For
Explore threat detection using human intuition, visualization, and abductive reasoning. Learn to uncover hidden security risks and develop actionable intelligence through innovative analytical approaches.
Friday the 13th - JSON Attacks
Explore JSON vulnerabilities, focusing on data libraries and serializers. Learn about attack vectors, classifications, and mitigation strategies for securing applications against JSON-based threats.
WiFuzz - Detecting and Exploiting Logical Flaws in the Wi-Fi Cryptographic Handshake
Explore techniques for detecting and exploiting logical vulnerabilities in Wi-Fi cryptographic handshake implementations, focusing on model-based testing and real-world examples.
Evading Microsoft ATA for Active Directory Domination
Explore techniques to bypass Microsoft ATA's threat detection in Active Directory, covering reconnaissance, credential attacks, lateral movement, and persistence methods.
Exploit Kit Cornucopia
Explore creative techniques for detecting Exploit Kit infrastructure, including compromised websites, gates, and dedicated hosts, while understanding their underlying architecture.
Fad or Future - Getting Past the Bug Bounty Hype
Panel discussion on bug bounty programs: insights, challenges, and best practices from experienced program managers. Covers ROI, hunter interactions, and lessons learned for effective implementation and management.
Redesigning PKI to Solve Revocation, Expiration, and Rotation Problems
Explore PKI redesign for IoT security, addressing key revocation, expiration, and rotation challenges. Learn from real-world experiences and discover innovative solutions for robust device management.
Incident Response
Explore incident response and threat intelligence with Palo Alto Networks' SVP Wendi Whitmore, discussing cybersecurity consulting, ransomware trends, and prevention strategies.
The State of State Machines
Explore mobile security threats, the evolving landscape, and Zero Trust principles in this insightful discussion on protecting mobile devices and data.
Real Eyes, Realize, Real Lies - Beating Deception Technologies
Explore weaknesses in deception technologies, learn tactics to overcome advanced techniques, and discover a new open-source tool for red teams to avoid traps during engagements.