Be Mean to Your Code - Rugged Development & You
Pragmatic approaches and tools for ruggedizing your development lifecycle, from code commit to running system. Learn solutions for secure, resilient applications in fast-paced environments.
Breach Assessments - Are You Owned? You Can Find Out!
Discover techniques to detect ongoing network breaches, analyze anomalous behavior, and eradicate threats from Red Team experts turned Blue Team specialists.
Rugged Software Engineering
Practical strategies for rapid and secure software development, addressing challenges in modern engineering organizations and emphasizing rugged software practices.
We Are the Cavalry - Why It Has to Be Us and Why Now
Exploring cybersecurity challenges in the Internet of Things era, emphasizing the need for proactive measures and collective responsibility to address emerging risks and protect human safety.
Big Data, Little Security - Practical Steps for Securing Big Data
Practical steps for securing big data installations, addressing challenges and vulnerabilities in velocity, variety, and volume. Explores security measures, authentication, and threat modeling.
From Gates to Guardrails - Alternate Approaches to Product Security
Exploring Netflix's innovative approach to product security, emphasizing automation, DevOps culture, and continuous assessment for agile development in cloud environments.
Million Browser Botnet
Explore how online advertising networks can be exploited to create massive browser botnets, enabling DDoS attacks, spam campaigns, and password cracking without leaving traces. Learn about the scalability and potential risks of this attack scenario.
Railsgoat - Rails Attack and Defense
Explore RailsGoat, an OWASP project for Rails security training. Learn common vulnerabilities, remediation techniques, and attack scenarios aligned with the OWASP Top 10 using a purposely vulnerable Rails application.
Riding the Magical Code Injection Rainbow
Explore advanced exploitation techniques for SQL injection, XPath injection, cross-site scripting, and shell command injection using the Magical Code Injection Rainbow framework for configurable vulnerable applications.
Malware Automation
Explore automated malware production techniques, tools, and methodologies used by attackers to generate thousands of threats daily, including a live demonstration of the process.
Everything Useful I Learned About Software Security, I Learned at Microsoft
Discover key software security insights from Michael Howard's 18-year Microsoft journey, covering depreciation, friction reduction, network security, and practical strategies for robust development.
Fast Adversaries - Fast Countermeasures
Fast-paced hacking techniques and countermeasures: Learn about adversaries' evolving tools, tactics, and how to protect assets effectively. Explore rapid detection, patching, and risk management strategies.
Security Automation in the Agile SDLC - Real World Cases
Explore real-world examples of implementing successful security automation in fast-paced Agile development environments, focusing on practical strategies and processes.
Managing Certificates and TLS Endpoints
Explore TLS/SSL management, vulnerabilities, and tools for maintaining secure systems. Learn about emerging threats, automation techniques, and best practices for certificate and endpoint management.
Getting Security Up to Speed with CI - CD
Automating security in CI/CD: Learn about Threadfix-Centric Application Security Architecture, challenges in AppSec testing, and leveraging QA regression for enhanced coverage.
Designing Flexibility in Software to Increase Security
Explore designing flexible software architecture to enhance security, adapt to changes, and prevent vulnerabilities. Learn from real-world examples and gain practical tips for writing better, more adaptable code.
Httpillage - Calling All Nodes
Explore distributed HTTP-based attacks using Httpillage, a tool for multi-node penetration testing. Learn to enhance impact demonstration and overcome limitations of single-host security assessments.
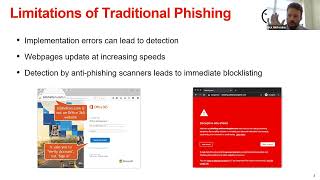
Catching Transparent Phish - Understanding and Detecting MITM Phishing Kits
Explore MITM phishing toolkits, their threat models, and detection methods. Learn about network-level analysis, classifiers, and countermeasures to enhance cybersecurity defenses.
A Wander Through the World of Container Security
Explore container security, from Docker to Kubernetes, covering breakout vulnerabilities, networking challenges, and RBAC. Gain insights into potential threats and future attack vectors in containerized environments.
OWASP Flagship Projects - OWASP Dependency-Check
Learn to identify and mitigate vulnerabilities in software dependencies using OWASP Dependency-Check, enhancing application security through effective composition analysis.
OWASP Flagship Projects - OWASP DefectDojo
Learn about OWASP DefectDojo, an open-source application security management tool. Explore its features, automation capabilities, deployment options, and community-driven development.