Security Vulnerabilities in DVB-C Networks - Rahul Sasi - Ekoparty Security Conference - 2014
Explore security vulnerabilities in DVB-C networks, including middleware server attacks, protocol bugs, and MPEG stream fuzzing. Learn to hijack TV streams and manipulate cable broadcasting systems.
A Wake-Up Call - Information Security for Non-Profits, Foundations, and Charities
Exploring cybersecurity challenges for non-profits, this talk offers strategies to protect organizations, donors, and beneficiaries in the digital age, emphasizing unique sector needs and practical solutions.
Attack Vectors in Biometric Recognition Systems - Mobile Authentication Use Case, Blockchain, and More
Explore vulnerabilities in biometric recognition systems, including mobile authentication, spoofing techniques, and emerging technologies like blockchain, with insights on future developments and security challenges.
Startup Security - Making Everyone Happy
Automating security for startups using open-source tools to integrate dependency, code, and infrastructure protection without impeding progress or increasing developer workload.
Security for DevOps
Learn to identify and prevent application abuse by understanding adversary tactics and implementing effective security architecture in DevOps environments.
Making Invisible Things Visible - Tracking Down Known Vulnerabilities
Insights on software supply chain practices, revealing vulnerabilities in open source components and strategies for improving application security in high-performance development organizations.
Cryptography Pitfalls
Explore common cryptography pitfalls, modern techniques, and tools to enhance system security. Learn about random number generation, hash functions, ciphers, and authentication protocols.
Cryptography 101 - A History and the Basics of Cryptography
Explore the evolution and fundamentals of cryptography, from ancient ciphers to modern encryption methods, understanding their strengths and vulnerabilities.
Practical Physical Security Advice for the Modern Enterprise
Practical advice on improving physical security, covering common weaknesses, bypass techniques, vulnerability mapping, and cost-effective solutions for modern enterprises.
Uninvited Guests on the World's Wild Web - Understanding Malicious Web Bots
Explore malicious web bots, their impact on applications, and effective countermeasures using OWASP's Automated Threat Handbook. Learn to protect against unwanted automation and improve web security.
Go Purple! Adopt Purple Team Strategy to Augment Application Security Programs
Explore purple team strategies to enhance app security programs, bridging defensive and offensive approaches for effective collaboration and improved security outcomes.
A Physical Security Plan for Implementing ISO 27002
Explore physical security implementation for ISO 27002, covering human resources, asset management, and access control. Learn from real-world examples and gain insights on testing, remediation, and continuous improvement.
Interact Differently - Get More from Your Tools Through Exposed APIs
Explore how to leverage exposed APIs and plugin interfaces in software tools to enhance functionality, streamline workflows, and create custom solutions for improved efficiency and effectiveness.
Demystifying a Malware Attack
Explore the anatomy of malware attacks, from deployment to key players involved. Gain insights into attack strategies, technologies used, and lessons for better cybersecurity preparedness.
Why the LinkedIn Hack Could Be Your Biggest AppSec Threat
Explore account takeover threats, their long-term impact, and effective defense strategies. Learn about hacking techniques, credential stuffing, and tools to protect against evolving cyber risks.
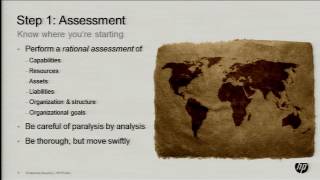
You're Going to Need a Bigger Shovel
Explore software security assurance, application security, and organizational strategies for effective resource planning and process building in cybersecurity.
Hiding From Big Brother Using Distributed Steganography
Learn techniques for hiding data from surveillance using distributed steganography, exploring methods like hidden files, alternate data streams, and encryption combined with steganographic approaches.
Reversing Web Applications
Explore web application reverse engineering techniques, from information gathering to active testing, to understand behavior, analyze code, and improve security assessments.
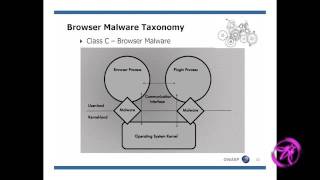
The Good Hacker - Dismantling Web Malware
Explore web malware anatomy, impact, and detection techniques. Learn about browser vulnerabilities, drive-by downloads, and real-world case studies of exploit kits and botnets.
SSL and the Future of Authenticity
Explore SSL's role in online security, challenges with certificate authorities, and innovative approaches to authentication in the digital age.
Threat Modeling Cloud Apps - What You Don't Know Will Hurt You
Explore threat modeling for cloud applications, focusing on AWS services, security controls, and potential risks. Learn to identify assets, adapt to cloud architectures, and address new security challenges.