20 Years In - Security’s Grand Challenges, Then and Now
Explore the evolution of cybersecurity challenges over two decades, from intelligence and scale to implicit trust, password reliance, and cloud migration risks. Gain insights into mitigating advanced threats and future security landscapes.
The 5 Most Dangerous New Attack Techniques and How to Counter Them
Experts discuss cutting-edge cyber attack techniques, their mechanisms, and effective countermeasures. Gain insights into emerging threats and proactive defense strategies from leading security professionals.
What Really Happens When Hackers Attack Medical Devices
Explore medical device hacking, FDA regulations, and cybersecurity in healthcare. Includes live demo of network attack and interactive code session on data integrity protection.
Supply Chain Security in the Software Era
Explore software supply chain risks and gain insights on mitigating them through real-world examples and concrete recommendations for policy makers and executives.
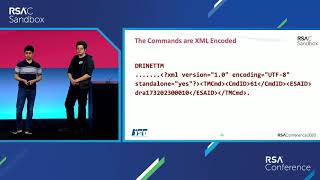
IoT Bug Hunting - From Shells to Responsible Disclosure
Explore techniques to circumvent security controls in IoT devices, from uncovering vulnerabilities to responsible disclosure. Gain insights into remote attacks and manufacturer security shortcomings.
Privacy by Design Lessons from Beyoncé
Explore privacy engineering best practices and future trends through the lens of Beyoncé's approach, reflecting on GDPR's impact and emerging privacy regulations.
Hey Google, Activate Spyware! When Google Assistant Uses a Vulnerability as a Feature
Uncover Android vulnerabilities allowing remote control of photos, videos, and location data without user knowledge. Learn how researchers chained weaknesses to create a rogue spy application.
Hacking the Unhackable - Pwning the Bitfi Crypto Wallet
Explore the security flaws in the Bitfi crypto wallet, learn from its mistakes, and understand best practices for secure device development and responsible disclosure.
Probe to Pwn - Rookie Track
Explore mobile and wireless attack methods, from target identification to device compromise, and learn mitigation strategies to protect against various threats and vulnerabilities.
Crawling Metadata with Recon-ng
Explore metadata extraction using Recon-ng plugin metadamn.py, learning about its capabilities, challenges, and future developments in web reconnaissance.
InfoSec is a Board Responsibility
Elevate InfoSec to a governance issue by speaking 'board talk', addressing objections, and tailoring proposals to focus on measurable benefits, risk mitigation, and corporate objectives.
A Look at Modern Warfare
Explore the economic impact of cyber warfare compared to traditional military conflicts, analyzing cost-effectiveness and strategic implications in modern combat scenarios.
The Joy of Passwords
Explore password security, learn about vulnerabilities, and discover effective strategies for creating and managing strong passwords to enhance your online protection.
Rise of the Vermilion - Cross-Platform Cobalt Strike Beacon Targeting Linux and Windows
Explore the first cross-platform Cobalt Strike re-implementation, Vermilion Strike, targeting both Linux and Windows in real-world attacks. Learn about this significant malware discovery.
JavaScript Obfuscation - It’s All About the P-a-c-k-e-r-s
Explore JavaScript obfuscation techniques and learn a method for detecting packers to identify obfuscated files, crucial for understanding modern security threats.
Hacker TikTok - Community, Creativity, and Controversy
Panel discussion exploring security-focused TikTok creators' experiences in bringing hacking awareness, humor, and community to a new audience, highlighting successes and challenges in this emerging frontier.
CISO Panel Discussion
Insightful discussion on building and scaling top security teams, exploring strategies for talent attraction, retention, and overcoming challenges in the cybersecurity industry.
Hook, Line and Sinker - Pillaging API Webhooks
Explore "Webhook Boomerang flaws" and learn how to exploit SSRF vulnerabilities in API webhooks, potentially compromising cloud credentials despite security measures.
Exposed Secrets - How Public Git Repositories and Docker Images Expose Millions of Secrets Like API Keys and Security Certificates Every Year
Uncover the alarming spread of exposed API keys and secrets in public repositories. Learn about research findings, causes, and implications for cybersecurity.
The Power of Guardrails - How to Slash Your Risk of XSS in Half
Discover how secure code defaults can significantly reduce XSS vulnerabilities and elevate overall security. Learn strategies to implement effective guardrails and minimize recurring security risks.
Ooga Booga - Avoiding Reinvention of the Wheel - Useful Security Tools and Lessons to Know
Discover Marie Kondo-inspired techniques for managing security challenges efficiently. Learn about useful tools and lessons to avoid reinventing the wheel in under-resourced security teams.