The Ransomware Threat - Tracking the Digital Footprints
Explore ransomware's evolution, prevention strategies, and digital footprint tracking techniques to enhance cybersecurity and protect businesses from evolving threats.
Mobile App Corporate Espionage
Explore real-world corporate espionage techniques using hidden behaviors in mobile apps, focusing on data risk threats and out-of-band communications for leaking sensitive information.
Emerging Best Practices in Software Supply Chain Security - What We Can Learn from Google, the White House, OWASP, and Gartner
Explore emerging best practices in software supply chain security, analyzing guidelines from major organizations to compile key strategies for mitigating risks in deployment pipelines.
RadRAT - An All-in-One Toolkit for Complex Espionage Ops
Uncover RadRAT: a sophisticated, undetected malware with remote access capabilities, lateral movement, and evasion mechanisms for targeted attacks and information exfiltration in large networks.
Deconstructing APT28's XAgent for OSX
Detailed analysis of APT28's XAgent malware for macOS, exploring its advanced spying capabilities including keylogging, screen capture, and data exfiltration from iOS backups.

WebAuthn - How to FIDO
Explore FIDO2 WebAuthn for phishing-resistant, passwordless authentication. Learn implementation strategies for stronger user protection on websites and applications.
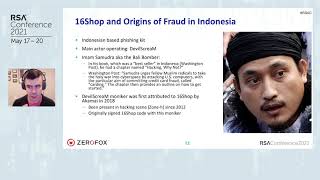
My Phishing Kit Burnbook
Explore phishing kit ecosystems, organized crime groups, and PhishPond tool for detection and analysis in this cybersecurity deep dive.
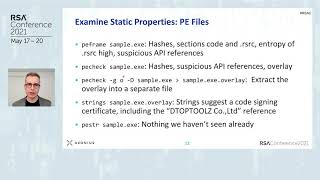
Analyzing Windows Malware on Linux - Getting Started Tips and Examples
Practical session on using free Linux tools for Windows malware analysis, featuring the REMnux toolkit. Learn essential techniques for incident response and SOC analysis.

CVSS Scores Are Dead - Let’s Explore 4 Alternatives
Explore limitations of CVSS scores and benefits of risk-based vulnerability scoring, examining alternatives like EPSS, SSVC, and VPR for more comprehensive threat assessment.
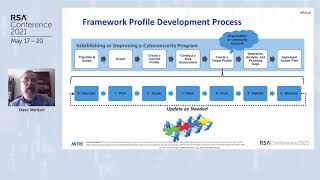
Three’s Company - Unpacking and Settling in with Three NIST Frameworks
Explore how NIST's Risk Management, Cybersecurity, and Privacy Frameworks complement each other to enhance enterprise risk management and improve organizational security posture.
DBOM and SBOM - New Options for Better Supply Chain Cybersecurity
Explore new approaches to supply chain cybersecurity using Digital and Software Bill of Materials. Learn how these tools can enhance risk management and component traceability in complex global supply chains.
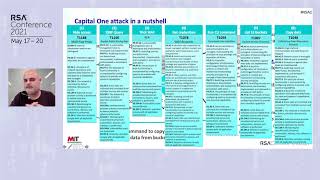
A Case Study of the Capital One Data Breach
Explore the 2019 Capital One data breach, examining attack methods, compliance issues, and corporate culture's impact on cybersecurity posture.
What's New with the CIS Controls v8
Explore key updates in CIS Controls v8, reflecting major changes in modern computing and infrastructure environments for enhanced cybersecurity practices.
SolarWinds - What Really Happened?
Insightful analysis of the SolarWinds cyberattack, revealing unique perspectives on the incident's details, methods, and perpetrators, with valuable lessons for enhancing industry-wide cybersecurity measures.
How to Tell the Right Cyber-Story to Executives and Board Members
Learn to effectively communicate cybersecurity strategies to executives using real-world examples, key metrics, and persuasive storytelling techniques for justifying initiatives and gaining C-level support.
Hacking the Cybersecurity Job Market - A Primer for Students & Grads
Expert panel provides guidance on starting a cybersecurity career, discussing industry trends, job opportunities, and offering advice for students and recent graduates entering the field.
Security Awareness Training for the Remote Workforce
Strategies for maintaining security awareness culture in remote work environments, including tips for expanding training programs and ensuring continued vigilance among distributed teams.
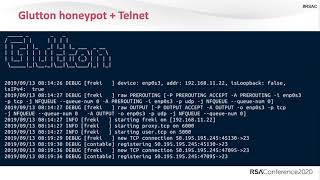
My Botnet Always Beats Yours - A Honeypot to Massive Bot Fight Scenes
Explore the fascinating world of IoT botnets through threat hunting stories, uncovering dramatic fight scenes between botnet herders and their evolving tactics in the dark web.
Mystery and Magic Intersect with Human Behavior Analysis
Explore human behavior, security vulnerabilities, and deception with Dr. Lorrie Cranor in this intriguing discussion on the intersection of psychology and cybersecurity.
Hacking Society
Explore how a computer security mindset applies to societal systems. Learn to identify vulnerabilities and defend core structures like elections, economy, and lawmaking.
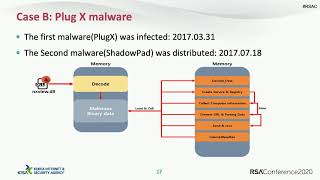
Chronicle of the Supply Chain Attack and Two Attack Strategies
Explore supply chain attack strategies, including software development environment and update server penetration, through analysis of incidents targeting Korean and global companies.