
From Chaos to Clarity: Deciphering Cache Inconsistencies in a Distributed Environment
Explore Netflix's distributed caching system, its replication engine processing 30M requests/second, and a critical debugging journey that nearly delayed a global launch. Learn applicable techniques for any organization.
What Is Incident Severity, but a Lie Agreed Upon? - Rethinking Incident Classification
Explore the complexities of incident severity in SRE, challenging common assumptions and discussing strategies to develop effective severity frameworks tailored to your organization's needs.
Securing Java Containers by Breaking In
Explore container security through live hacking, learn vulnerabilities in Docker images, and adopt best practices for securing containerized Java applications in production.
AI Showdown - The Good, The Glitchy, and The Risky
Evaluating top AI frameworks for CI/CD integration, focusing on accuracy, security, coding practices, and compliance with emerging standards and legislation.
Encryption 3 - PKC 2024 Session and Closing Remarks
Explore advanced encryption techniques and latest research findings in cryptography, followed by concluding insights from the PKC 2024 conference.
Attacks and Hardness in Public Key Cryptography - PKC 2024 Session
Explore cutting-edge research on cryptographic attacks and hardness at PKC 2024, featuring expert presentations on the latest advancements in public-key cryptography.
Cryptanalynomics - Invited Talk at PKC 2024
Opening session and invited talk on "Cryptanalynomics" by Nadia Heninger at PKC 2024, featuring welcome addresses and discussions on cryptographic analysis and economics.
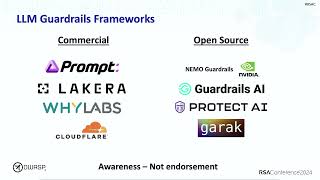
Securing AI Apps with the OWASP Top Ten for Large Language Models
Explore strategies to mitigate risks in generative AI using OWASP Top 10 for LLMs. Learn best practices for building secure and responsible AI applications in your environment.
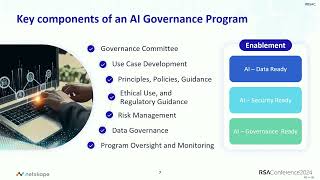
Navigating the AI Frontier - The Role of the CISO in GenAI Governance
Discover how CISOs can lead AI governance, balancing risk management and innovation. Learn to integrate AI safeguards, ensure data integrity, and foster responsible practices with a comprehensive framework and roadmap.
Controlling a Data Footprint - How to Build a Data Disposition Framework
Learn to build a data disposition framework to determine optimal data storage duration and methods for protecting, altering, or destroying information to meet organizational requirements.
IP Protection and Privacy in LLMs - Leveraging Fully Homomorphic Encryption
Explore how Fully Homomorphic Encryption addresses IP protection and privacy concerns in Large Language Models, with a live demonstration of this innovative hybrid approach.
Permissions: Balancing Centralized and Decentralized Approaches
Explore balancing fast local policy decisions with uniform security guardrails in modern businesses. Learn strategies for creating permission structures that are quick, adaptable, and globally dependable.

Key Management 101 - DEKs, KEKs, and Credentials Living Together
Explore key management essentials, including types of keys, usage, and tools. Learn practical advice for PCI compliance and securing sensitive data in cloud environments.
Keeping Up with the Algorithms - A Journey in Artificial Intelligence
Explore AI's rapid evolution and future challenges with experts from industry, academia, and government. Gain insights on building a safe, reliable framework for AI's future.
Homeland Security in the Age of Artificial Intelligence
Exploring AI's impact on national security and community protection, discussing responsible development and adoption to maximize benefits while mitigating potential risks and adversarial use.
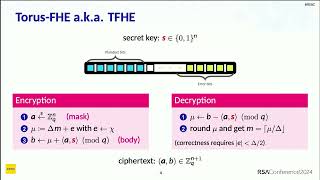
Homomorphic Encryption - TFHE Public-Key Encryption and Differential Privacy
Explore TFHE public-key encryption and differential privacy in approximate homomorphic encryption with experts from Zama and Royal Holloway, University of London.
Empowering Women Using AI - Addressing Gender-Based Violence Online
Explore how AI can combat gender-based violence online, raise awareness, and protect individuals. Learn about innovative approaches to mitigate online harassment and empower women in the digital space.
Unlocking Digital Ownership: How to Store Accounts Using Blockchain Technology
Explore blockchain's role in digital ownership, empowering developers to control their accounts and data. Learn how this technology revolutionizes digital identity and security.
Public Key and Messaging - Eurocrypt 2024
Explore cutting-edge research on public key cryptography and secure messaging at Eurocrypt 2024. Gain insights into advanced cryptographic techniques and their applications in modern communication systems.
Private Information Retrieval - Eurocrypt 2024
Explore cutting-edge research on Private Information Retrieval at Eurocrypt 2024, featuring presentations on advanced cryptographic techniques for secure data access and privacy protection.
Practical Attacks
Explore cutting-edge research on practical cryptographic attacks presented at Eurocrypt 2024, featuring insights from leading experts in the field of information security.