Detecting Crypto-Jacking in Kubernetes Workloads
Detect crypto-jacking in Kubernetes workloads using Falco. Learn to create rules, test environments, and implement security measures for cloud-native applications.
How to Build a Kubernetes Admission Controller from Scratch - Tutorial
Learn to build a Kubernetes admission controller from scratch, exploring fundamentals, installation, and Python implementation. Gain hands-on experience in enhancing cluster security and policy enforcement.
Container Factory for Aerospace and Defense Enterprises
Explore how Collins Aerospace develops a container factory to meet governance and compliance rules for safety-critical software, addressing challenges and integrating innovative solutions for cybersecurity and compliance.
Spicing up Container Image Security with SLSA and GUAC
Explore SLSA and GUAC tools to enhance container image security, verify build provenance, and understand artifact composition for safer deployments in production environments.
Security++ - Hide Your Secrets via Distributed Hardware Security Module
Explore distributed Hardware Security Modules for enhanced cloud security and performance. Learn how this solution balances remote and local HSMs, enabling secure cryptographic operations across cloud, on-premise, and edge environments.
Securing the Superpowers: Who Loaded That eBPF Program?
Explore eBPF technology's power and security implications. Learn about auditing, monitoring, and enforcing eBPF program loading on Linux systems using Tetragon for enhanced system protection and accountability.
Protecting Kubernetes Clusters When Administrators Quit - Revoking Access and Best Practices
Explore strategies for revoking access to Kubernetes clusters when administrators or users leave, addressing real-world security challenges and best practices for minimal disruption.
Securing Kubernetes
Explore Kubernetes security strategies and best practices to protect your containerized applications and infrastructure in this informative session.
Top 5 Authorization Trends in 2022 - A Year in Review
Explore the top 5 authorization trends of 2022 in cloud-native computing, offering insights into evolving security practices and technologies.
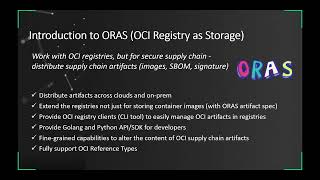
Secure Container Supply Chain with Notation, ORAS, and Ratify
Explore tools for securing container supply chains: Notation for signing artifacts, ORAS for distributing OCI artifacts, and Ratify for verifying container images.
Securing Kubernetes Clusters: A Collaborative Approach to Self-Assessment
Explore the collaborative security assessment of Kubernetes Cluster API, covering threat modeling, global teamwork challenges, and lessons for future sub-project evaluations across the Kubernetes ecosystem.
Kubescape Roadmap - Future Developments in Kubernetes Security
Explore the future of Kubernetes security with Kubescape's development plans and upcoming features in this informative CNCF presentation.
Creating Security Policies and Controls for Kubernetes Using ChatGPT
Explore how to leverage ChatGPT for creating robust security policies and controls in Kubernetes environments, enhancing your cloud-native security practices.
Exploring Process Capabilities with eBPF - Monitoring and Security in Cloud Native Applications
Explore eBPF's capabilities for scaling, monitoring, and securing cloud-native apps. Learn to run ad hoc experiments using BumbleBee and expose kernel events as Prometheus metrics for enhanced security research.
Secret Management in Kubernetes: Using Secret Store CSI Driver
Explore secure secret management in Kubernetes using Secret Store CSI Driver. Learn its architecture, multi-credential provider support, and see code examples for robust security implementation.
Kubernetes Environments Visualization - Strategies and Solutions at GitLab
Explore GitLab's approach to visualizing Kubernetes environments, managing access, and leveraging the GitLab platform for effective environment management and resource visualization.
Kubernetes Code of Conduct - Working for the Community
Panel discussion on Kubernetes' Code of Conduct, exploring its application, incident response process, and community impact. Learn how it fosters a safe, respectful environment and contributes to the Kubernetes community.
RBAC to the Future: Untangling Authorization in Kubernetes
Explore Kubernetes RBAC essentials, from its inner workings to enterprise-level strategies. Learn to design, automate, and monitor least-privilege configurations for enhanced security and efficiency.
The Hacker's Guide to Kubernetes - Exploiting Vulnerabilities and Best Practices
Interactive demos showcasing live Kubernetes hacking, exploring OWASP Top 10 vulnerabilities and exploits. Learn to identify and mitigate security risks in k8s clusters, containers, and components.
Canals and Bridges: Using Amsterdam's Transit System to Secure Kubernetes Networks
Explore Kubernetes network security through Amsterdam's canal system analogy. Learn threat modeling, monitoring tools, and NetworkPolicies to implement robust security strategies for complex K8s environments.
Cert-Manager for SPIFFE: Solving Multi-Cloud Workload Identity - Lecture
Explore how cert-manager leverages SPIFFE to solve multi-cloud workload identity challenges, enabling secure pod access across different cloud environments.