Container Patching: Making It Less Gross Than the Seattle Gum Wall
Explore strategies for efficient container patching, including prevention, detection, fixing, and monitoring. Learn about opensource tools and best practices to streamline the process and meet security requirements.
Hands-on Hacking Kubernetes and Ways to Prevent It
Hands-on workshop exploring Kubernetes vulnerabilities and prevention strategies. Demonstrates remote code execution exploit and teaches mitigation techniques for enhanced container security.
Unpacking Open Source Security in Public Repositories and Registries
Explore security risks in popular open-source projects and public registries. Learn about common misconfigurations, vulnerabilities, and best practices to safeguard your systems when using public resources.
Securing Self-Hosted GitHub Actions with Kubernetes and Actions-Runner-Controller
Explore secure deployment of self-hosted GitHub Actions runners using Kubernetes and actions-runner-controller. Learn about cluster settings, controller configurations, and runner pod security for regulated environments.
Cryptographic Agility: Preparing Modern Apps for Quantum Safety and Beyond
Explore cryptographic agility for modern apps, focusing on quantum safety. Learn strategies for seamless transitions between cryptography standards and preparing for future cryptographic migrations.
Get Your Security Priorities Straight - Identifying Workloads Under Real Threat with Context
Discover a security prioritization system for Kubernetes workloads based on the MITRE framework, helping differentiate real threats from potential ones in various contexts.
From the Cluster to the Cloud: Lateral Movements in Kubernetes
Explore techniques for lateral movement from Kubernetes containers to cloud resources, covering RBAC misconfigurations, authentication methods, and real-world incidents. Learn prevention and detection strategies.
Beyond Cluster-Admin - Getting Started with Kubernetes Users and Permissions
Learn to implement users and permissions in Kubernetes clusters, covering user provisioning methods, RBAC for fine-grained access control, and strategies for both managed and self-hosted environments.
SIGs Aren't Silos - A Case Study Into Solving Inter-Domain Problems in Kubernetes Development
Explore a cross-SIG bug in Kubernetes, its impact, and lessons learned. Gain insights into inter-domain problem-solving and improving collaboration between Special Interest Groups in open-source development.
KubeEdge: From Fixed Location to Movable Edge - Latest Updates and Future
Explore KubeEdge's latest advancements in edge computing, including new industry adoptions, scalability improvements, and community updates. Learn about its expanding capabilities and future roadmap.
Kubernetes to Cloud Attack Vectors: Demos of Cross-Environment Vulnerabilities
Explore attack vectors between managed Kubernetes clusters and cloud environments. Learn best practices for securing EKS, AKS, and GKE against lateral movement and compromise.
Lessons Learned From Etcd Data Inconsistency Issues
Explore critical etcd data inconsistency issues, their discovery, resolution, and key lessons for the cloud native community. Gain insights into maintaining robust distributed systems.
Cloud Native Kubernetes for Public Safety Systems - A Case Study
Exploring Kubernetes implementation for public safety systems, focusing on automation, scalability, and cost management in a diverse technological environment.
Data on Kubernetes: Deploying and Running PostgreSQL - Patterns for Databases in Kubernetes Clusters
Explore deploying PostgreSQL on Kubernetes using Cloud Native PostgreSQL operator and CSI-plugin. Learn about zero/low RTO, replication effects, and object store backups for robust database management.
How SIG Release Cooks Trustworthy Artifacts From Raw Source Code - Kubernetes Build Process
Explore how Kubernetes SIG Release transforms source code into trusted artifacts, focusing on SLSA compliance, community-controlled infrastructure, and expanded artifact signing.
How the Basics of Kubernetes Authentication Scale for Organizations
Explore Kubernetes RBAC for flexible team access. Learn basics, identity details, common issues, limitations, auditing, and real-world patterns. Includes live demos for DevOps culture support.
Zero Trust Workload Identity in Kubernetes
Explore Zero Trust principles in Kubernetes using SIFFE and Spire for workload identity-based authorization, eliminating the need for secrets and enhancing security across service meshes.
Improving Secure Pod-to-Pod Communication Within Kubernetes Using Trust Bundles
Explore advanced techniques for enhancing secure pod-to-pod communication in Kubernetes using trust bundles, leveraging cert-manager, SPIFFE, and KEP-3257 for automated TLS certificate creation and mTLS patterns.
Verifiable GitHub Actions with eBPF
Explore eBPF-based solution for securing GitHub Actions pipelines against supply chain attacks. Learn about runtime security, build profiling, and verification techniques to protect your software development process.
Finding the Needles in a Haystack - Identifying Suspicious Behaviors with eBPF
Explore how AWS uses eBPF to identify security risks in Kubernetes, including malicious activities and communication with known threats. Learn advantages, challenges, and practical applications.
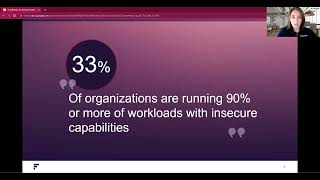
Kubernetes Benchmark Report 2023 - What's Working and What's Not
Explore key findings from the 2023 Kubernetes Benchmark Report, covering reliability, security, and efficiency in cloud-native environments.