Rust on L4Re - Safe Language Meets Safe Microkernel
Explore the integration of Rust's memory-safety features with L4Re's microkernel for enhanced system reliability and security. Learn about porting challenges and future applications in IPC.
Embedding WebAssembly for Scripting in Rust Applications
Explore WebAssembly integration in Rust applications for efficient dynamic scripting, covering benefits, implementation, and practical demonstrations.
Why You Should Take a Look at Rust
Découvrez les avantages de Rust : sécurité, performance et abstraction sans coût. Apprenez pourquoi ce langage moderne aspire à devenir incontournable dans les dix prochaines années.
Introducing Rust-AV: A Pure-Rust Approach to Multimedia Development
Explore rust-av: a pure-Rust approach to multimedia development, offering memory safety and performance. Learn how Rust's features can create a more reliable and user-friendly multimedia framework.
Handsome Macros in Rust - Intern Presentation
Explore advanced Rust topics: macros, code coverage, sandboxing, and applied statistics. Gain insights from Mozilla experts on enhancing Firefox's performance and security.
Subtyping in Rust - Magic and Misconceptions
Explore Rust's subtyping, variance, and advanced data structure concepts with Felix Klock. Gain insights into Rust's unique approach to type systems and memory safety.
Standardization and Security - Improving Cloud Security Posture Through Standardization
Explore how Northwestern Mutual enhanced cloud security through standardization, addressing the paradox of choice in development tools and patterns to improve efficiency and reduce vulnerabilities.
Package Transparency for WebAssembly Registries
Explore WebAssembly package distribution with warg, a new registry protocol offering enhanced supply chain security through Package Transparency, verifiable data structures, and easy detection of operator compromise.
Cloud Native Security Landscape - Myths, Dragons, and Real Talk
Explore cloud-native security across the software lifecycle, from open-source creation to runtime threat detection. Learn about key projects, developer-security team collaboration, and separating real risks from myths.
Zero Trust in the Cloud with WebAssembly and WasmCloud
Explore WebAssembly and WasmCloud for enhanced cloud security. Learn about sandbox isolation, cryptographic signatures, and verifiable capability models to deploy secure, untrusted code with confidence.
CNI or Service Mesh? Comparing Security Policies Across Cloud Native Networking Solutions
Explore recent changes in cloud native networking solutions, comparing CNI and service mesh implementations for security policies, and understanding trade-offs between different approaches.
Taming Attestation for Cloud Native Edge Security with Parsec
Explore how Parsec simplifies hardware-backed security and attestation for edge devices, enabling secure communication with cloud services across diverse ecosystems.
Mapping Motives: Analysis of 2,000 Enterprise Cloud Detections - Strengthening Multi-Cloud SOC
Analysis of 2,000 cloud detections reveals enterprise control patterns, gaps, and attacker motives. Learn to strengthen multi-cloud security operations with actionable insights and MITRE ATT&CK framework application.
Lessons from 7 Headline-Grabbing Cloud Security Breaches
Analyze 7 real cloud security breaches, exploring attack methods, defense strategies, and specific takeaways to enhance cloud infrastructure protection and avoid similar vulnerabilities.
Cloud Native Security Whitepapers Overview
Overview of TAG Security's whitepapers and reference architectures for cloud native security, covering topics like supply chain security, zero knowledge, and security controls mapping.
Real-World Trust Management with Linkerd and Cert-Manager
Explore real-world trust management using Linkerd and cert-manager, enhancing security and reliability in cloud-native environments.
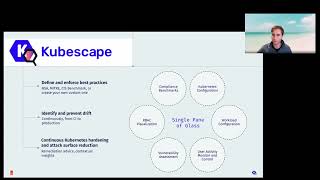
Securing the Cloud with Canonical Kubernetes and Kubescape
Learn to secure cloud environments using Canonical Kubernetes and Kubescape, exploring key strategies and tools for robust protection in modern containerized infrastructures.
Geeking Out with WebAssembly and Kubernetes Using ContainerD Shims
Explore WebAssembly integration with Kubernetes using ContainerD shims, covering features, risks, and practical demonstrations for cloud-native development.
Hacking Cloud Native Applications Through Open Source
Explore techniques for hacking Cloud Native applications using open-source tools, focusing on security vulnerabilities and mitigation strategies in containerized environments.
Don't Mind the Gap - Securely Accessing Cloud Resources with SPIFFE/SPIRE
Explore secure cloud resource access using SPIFFE/SPIRE for identity federation. Learn to access AWS and other services without managing API keys, simplifying cross-cloud interactions.
Real-Time Pipeline Monitoring for the Energy Sector
Explore real-time pipeline monitoring for energy, covering data ingestion, architecture, WebAssembly, security, and analytics. Learn innovative solutions for edge-to-cloud monitoring and virtualized testing.