Azure Vulnerability Testbed (AzGOAT) - Understanding and Hardening Azure Security
Explore Azure security vulnerabilities and defenses with AzGOAT, a lab environment for understanding attack surfaces, designing secure solutions, and minimizing threats in Azure environments.
Exploiting Web Messaging Implementations
Uncover vulnerabilities in cross-document messaging, learn common developer mistakes, and explore open-source tools for identifying post messaging security issues in web applications.
Insiders Guide to Mobile AppSec with Latest OWASP MASVS
Explore mobile app security with OWASP MASVS, covering data storage, network calls, authentication, coding, and reverse engineering. Gain insights from real-world experience and latest tools for effective mobile pentesting.
Testability Patterns for Web Applications - A New OWASP Project
Explore testability patterns for web applications in this OWASP project presentation, focusing on enhancing security testing effectiveness and efficiency.
Mobile Application Security Testing - Journey to Version 2.0
Explore the evolution of mobile app security standards and best practices in this insightful talk on the journey to OWASP Mobile Security Testing Guide v2.0.
How to Meet the New Mobile Application Security Imperative
Explore strategies for enhancing mobile app security, addressing vulnerabilities, and meeting modern security imperatives in this informative OWASP presentation.
Squeezing the Last Drop Out of OWASP Juice Shop
Explore advanced hacking techniques and security challenges in this hands-on session with OWASP Juice Shop, led by its creator Bjoern Kimminich.
Server-Side Prototype Pollution: Detection and Exploitation Techniques - OWASP AppSec Dublin
Explore server-side prototype pollution vulnerabilities, detection techniques, and prevention strategies in web applications with security expert Gareth Heyes.
Narrow - SCA Reachability Analysis Without The Effort
Explore efficient SCA reachability analysis techniques to enhance software security without excessive effort, presented by Josiah Bruner at Global AppSec Dublin.
JavaScript Realms - The Blank Spot in Web Application Runtime Security
Explore JavaScript Realms and their impact on web application runtime security, uncovering potential vulnerabilities and mitigation strategies.
Removing Secrets to Make Mobile Apps More MASVS-Secure
Explore mobile app security, focusing on removing secrets and enhancing MASVS compliance. Learn defense strategies against various attacks and discover a resilient authentication architecture.
Defending Against New Phishing Attacks that Abuse OAuth Authorization Flows
Explore advanced techniques to protect against sophisticated phishing attacks exploiting OAuth authorization flows, enhancing your cybersecurity defenses.
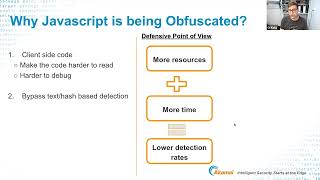
JavaScript Obfuscation: It's All About the Packers
Explore JavaScript obfuscation techniques, focusing on packers and their impact on code security and readability in this informative OWASP presentation.
Securing an API Ecosystem with OAuth 2.0
Explore OAuth 2.0 implementation for robust API security in this comprehensive talk by Philippe De Ryck, covering best practices and ecosystem protection strategies.
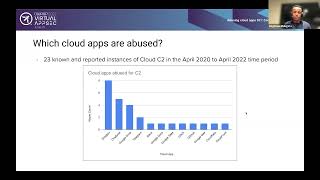
Abusing Cloud Apps 101 - Command and Control
Explore techniques for exploiting cloud applications as command and control infrastructure, focusing on security vulnerabilities and defensive strategies.
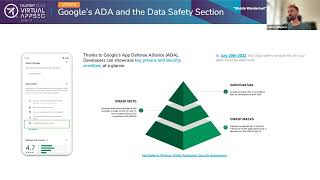
Mobile Wanderlust - Our Journey to Version 2.0
Explore the evolution of mobile security testing with insights on OWASP's latest advancements and best practices for protecting mobile applications.
OWASP Juice Shop Project
Explore web application security with OWASP's intentionally vulnerable Juice Shop, learning about common vulnerabilities and how to exploit and defend against them.
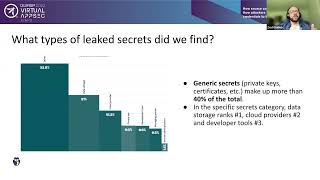
How Source Code is Revealing Our Secrets
Explore how source code can inadvertently expose sensitive information and learn strategies to protect against unintended data leaks in software development.
Quantifiable Quality - The New Standard of Secure Code
Explore innovative approaches to measure and enhance code security, focusing on quantifiable quality metrics for robust software development.
An Introduction to Rust
Comprehensive introduction to Rust programming language, covering basic syntax, ownership, borrowing, and advanced features like generics and traits. Suitable for experienced programmers.
The Rust Programming Language - A Much-Needed Solution
Explore Rust's impact on systems programming, its industry adoption, and key benefits. Learn why investing in Rust can benefit you and your organization.