The Secret Life of Secrets - Designing Secure API Keys
Explore API key design strategies, security measures, and best practices for creating robust and secure API authentication systems.
Hook, Line, and Tinker: A Dive into Phishing Campaign Sites
Explore phishing cases, learn active reconnaissance techniques, and discover how to disrupt attackers and identify security gaps with an AppSec engineer's insights and triage process.
Snow Nor Rain Nor Dependency Confusion - How to Deliver the Right Package
Practical insights on identifying, exploiting, and fixing dependency confusion vulnerabilities in real-world package environments, based on firsthand experience.
Advanced Persistent Teenagers - Understanding the Lapsus$ Playbook
Explore how teenage hackers breached major tech companies, analyze their techniques, and learn effective defense strategies against similar attacks.
Insane in the Supply Chain - Threat Modeling for Attacks on AI Systems
Explore AI supply chain risks and threat modeling strategies to protect against attacks that could impact company reputation and executive liability.
Guardians of Cybersecurity - Deploying IoT Devices via Drones and Dropboxes
Explore the cybersecurity implications of drones carrying hacking devices, discussing potential threats and the need for increased awareness in this emerging field of IoT and aerial technology.
Drones, RemoteID and the Thrilling Future of UAS Flight
Explore RemoteID technology reshaping drone flight, focusing on safety, security, and regulatory compliance. Discover current applications and challenges in the thrilling future of UAV aviation.
Performing Rapid Triage Analysis using ANY.RUN
Explore rapid triage analysis using ANY.RUN for efficient malware assessment. Learn to gather crucial indicators of compromise and prioritize potential threats effectively.
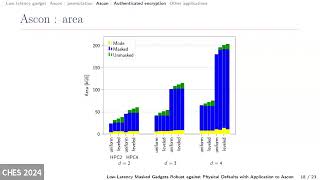
Gadgets II - Advanced Cryptographic Hardware Techniques
Explore advanced cryptographic hardware techniques and implementations in this CHES 2024 session, chaired by Rei Ueno.
Teach Your SBOM New Tricks with Bomshell
Explore bomshell, a scripting language for SBOM based on CEL. Learn to query, combine, and reshape SBOM documents across formats, enhancing compatibility and streamlining ingestion processes.
Is the Internet on Fire? Strategies for Mitigating Open Source Software Vulnerabilities
Explore strategies for mitigating open source software vulnerabilities, including supply chain attacks, SBOMs, and next-generation security controls for robust defense and compromise resilience.
Network ACLs Made Easy: Establishing Zero Trust Network Policies
Learn to automate Zero Trust network policies using AWS VPC Flow Logs and Terraform. Discover techniques for analyzing traffic data, optimizing security groups, and implementing efficient access controls without third-party solutions.
Threat Modeling for AI Apps with Attacks as Code
Explore automated threat modeling for AI apps using Secops-Chaos framework. Learn to encode TTPs as security experiments and map MITRE ATLAS TTPs to AI apps in Kubernetes environments.
Scan, Patch, VEX - Using Open Source Tools to Manage Vulnerabilities in Containers
Learn to manage vulnerabilities in cloud-native environments using open-source tools like Trivy and Copacetic, and standards like VEX. Improve security across development, testing, and production.
Where Does Your Software Really Come From - Artifact Attestations and Open Source Verification
Explore GitHub's Artifact Attestations: a new capability for verifying open source software origins, enhancing transparency and security in the OSS ecosystem.
How to Generate VEX Automatically for Your Project
Learn to automate VEX generation for Kubernetes workloads, reducing false positives in security scans and streamlining vulnerability management using Kubescape and a new GitHub Action.
Learn to Navigate the Perils and Pitfalls of Multi-Tenant Identity Infrastructure
Explore challenges and solutions in multi-tenant identity management for B2B, B2C, and M2M environments, focusing on security, user experience, and balancing isolation with resource sharing.
Guardians of the Dataverse - Securing the AI Supply and Data Chain
Explore strategies to secure AI/ML and Big Data pipelines, leveraging insights from NIST SP 800-204D and CNCF projects to protect critical AI workflows and sensitive data.
SPIFFE Ecosystem: MTLS and Identity with Linkerd and Teleport
Explore SPIFFE ecosystem growth, focusing on Linkerd and Teleport's implementation for workload identity verification across Kubernetes clusters and external environments.
All I Know About Cybersecurity I Learned from Fungus
Explore fascinating parallels between fungal biology and cybersecurity principles, gaining unique insights into cloud-native application security and best practices through nature-inspired analogies.
Leveraging Cryptographic Lineage for Context and Connected Trust
Explore cryptographic lineage for enhanced security, addressing challenges in AI adoption through attested claims and chain of custody, building on zero trust principles for improved traceability and trust in distributed systems.