Scanning at Scale with OWASP ZAP - Technical Challenges and Improvements
Explore techniques for scaling OWASP ZAP scans, including technical challenges, modifications, and improvements. Learn from Probely's experience as active ZAP contributors.
Lessons Learned Building a Software Supply Chain Security Team
Insights on building a software supply chain security function, exploring the role of SBOMs and addressing challenges in implementing effective security measures.
Using API Specifications to Attack APIs
Explore API security vulnerabilities, breaches, and scanning tools. Learn to leverage API specifications for both protection and potential exploitation in this comprehensive overview.
Building Trust-Based Networks with Dime Data Format
Explore Dime, a modern data format for building trust networks and enabling secure communication. Learn its advantages over X.509 certificates and its potential for future applications.
Defense-in-Depth Engineering Techniques for Secure Software Design
Explore techniques for building resilient software, identifying overlooked vulnerabilities, and designing for incident preparedness. Learn to architect secure systems and improve incident response capabilities.
Knowing What Risks Matter and Don't in Your Open Source
Explore key findings on open-source software risks, including usage trends, vulnerability rates, and best practices. Learn to prioritize and address critical issues in application security.
Hacking an Online Casino - Bug Bounty Stories Episode 1
Discover how a bug bounty hunter successfully hacked a major online casino. Learn about the techniques used and gain insights into the world of ethical hacking and cybersecurity.
A Blackbox Reduction for Adaptive Adversaries Using Differential Privacy
Explore a novel black-box transformation using differential privacy to convert dynamic algorithms from oblivious to adaptive adversary resistance, enhancing algorithm design for dynamic graphs.
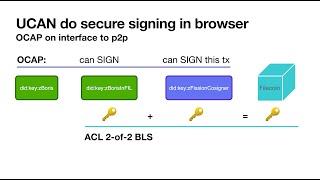
Secure Key Management in the Browser with UCAN - Fission Platform Overview
Explore secure key management in browsers using UCAN, WebCrypto API, and DIDs. Learn about Fission's platform and plans for Filecoin integration without browser extensions.
Towards Intelligent Application Security
Exploring the evolution of application security and proposing an automated approach integrating security into development and operations, aided by learning techniques and threat intelligence.
Another Look at the Five Most Dangerous Attack Techniques
Experts discuss current and emerging dangerous attack techniques, providing insights on prioritizing and preparing for upcoming threats in cybersecurity.
TETRA Radio Security: Uncovering Secret Cryptography in Law Enforcement Communications
Unveiling TETRA cryptography: Journey through radio jailbreaking, reverse-engineering, and exploiting vulnerabilities to analyze the proprietary algorithms used in critical communication systems worldwide.
Horror Stories from the Automotive Industry - Security Challenges and Solutions
Unveiling critical security flaws in automotive industry through penetration testing experiences. Explores industry behavior, proposes improvements for safer, more reliable future in vehicle development and cybersecurity.
Unified SOC - Centralized Security Data with OT Visibility for Intelligence-Driven Investigations
Experts discuss unifying Security Operations Centers by integrating OT cybersecurity, threat intelligence, and advanced technologies for comprehensive visibility and efficient investigations in industrial environments.
Loom Security Journey - Getting Over the Finish Line
Explore the security journey of a startup, from building essential functions to navigating a smooth acquisition. Gain insights into critical security measures during rapid growth and M&A processes.
LLMs at the Core: From Attention to Action in Scaling Security Teams
Practical insights on leveraging LLMs to automate security processes, enhance SDLC, and improve threat detection. Explore open-source tools for scaling security teams effectively.
Securing Generative AI - Is It All an Illusion?
Explore GenAI/LLM security, vulnerabilities, and assessment strategies. Learn a flexible framework for securing and deploying commercial AI systems, with insights from real-world experiences.
Imperfect Security - Doing Less to Achieve Better Security
Explore strategies for effective security programs through simplification, collaboration, and positive approaches, challenging the notion of "perfect security" for stronger outcomes.
The Road to Developers' Hearts - Bridging the Gap Between Security and Software Engineering
Insights on bridging the gap between security professionals and software engineers, based on experience building security software at scale.
Attacking and Defending Supply Chains - How We Got Admin in Your Cloud
Explore software supply chain vulnerabilities leading to secrets exfiltration and privilege escalation, with best practices for securing reference architectures and production environments.
Please Don't Discard - Security Data: Leveraging Structured Security Review Data
Discover how to leverage security review and threat modeling data for future challenges. Learn from Snowflake's approach to structuring and persisting valuable security information.