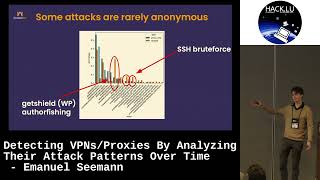
Detecting VPNs and Proxies by Analyzing Attack Patterns Over Time
Explore techniques for identifying VPNs and proxies through analysis of their attack patterns, enhancing network security and threat detection capabilities.

Disclosure, Hack and Back - Vulnerability Reporting and Cybersecurity Insights
Explore real-world vulnerability reports and hacking incidents, revealing common mistakes in both corporate security responses and cybercriminal operations. Gain insights into improving cybersecurity practices.
Cyberattacks on MGM and Caesars - Recent Casino Breaches
Analysis of recent cyberattacks on major casino companies, exploring threat actors, breach methods, and implications for cybersecurity in the hospitality industry.
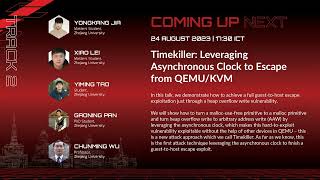
Timekiller: Escape From QEMU/KVM - Exploiting Asynchronous Clock Vulnerabilities
Demonstrating a novel guest-to-host escape exploit in QEMU/KVM using asynchronous clock vulnerabilities. Introduces "Timekiller" technique to turn heap overflow into arbitrary address write, achieving full VM escape.
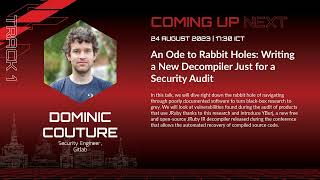
Writing a New Decompiler for JRuby Security Audits
Explore JRuby vulnerabilities and learn about YBurj, a new open-source decompiler for JRuby IR, enabling recovery of compiled source code for enhanced security audits.
Injecting Brains Into Blind SQL Injection - Optimizing Data Exfiltration
Innovative approach to optimize Blind SQL Injection using Machine Learning and statistics. Introduces Hakuin, a tool that significantly improves exfiltration speed for database schemas and content compared to standard methods.
How NTLM Relay Ruins Your Exchange Servers
Uncovers a critical NTLM relay attack surface in Exchange Server, affecting mailbox security and potentially leading to RCE. Explores vulnerabilities, exploits, patches, and protection strategies for Exchange environments.
Escaping From VMware Workstation Through the Disk Controller
Exploración detallada de una vulnerabilidad en los controladores de disco de VMware Workstation que permite escapar de una máquina virtual, con demostraciones de exploits para Linux y Windows.
Analyzing and Reverse Engineering Antivirus Signatures
Explore antivirus signature analysis and reverse engineering, gaining insights into detection evasion techniques and evaluating Microsoft Defender's effectiveness for improved cybersecurity strategies.
Lazarus Group's Undercover Operations in South Korea 2022-2023
Detailed analysis of Lazarus Group's recent cyber campaigns in South Korea, covering infiltration methods, lateral movement techniques, and data exfiltration strategies used by this sophisticated threat actor.
Extracting Information from Automotive Internet Units
Techniques for extracting and analyzing firmware from automotive internet modules, focusing on Qualcomm MDM-based units. Covers extraction methods, image analysis, and file system exploration.
Designing Your Own Electronic Attack Device
Learn to design and create custom electronic attack devices, from circuit boards to complete Linux systems, for personalized and efficient security testing and penetration tasks.
Bluetooth Sniffing: Privacy Implications and Unexpected Findings
Exploring Bluetooth sniffing implications: privacy, security, and societal impacts. Insights on device tracking, medical data, law enforcement, and potential vulnerabilities in various Bluetooth-enabled systems.
Exploiting the Lexmark PostScript Stack
Explore Lexmark PostScript stack exploitation, covering internals, language basics, mitigations, and achieving remote code execution through out-of-bounds read and type confusion vulnerabilities.
Embracing Failure to Be a Better Hacker and Human
Explore how embracing failure can enhance hacking skills and personal growth. Learn from real-world examples and gain insights into overcoming challenges in the hacking world.
A Tale of Lazarus and His Family - Hack.lu 2023
Explore the pervasive influence of Lazarus and related threat actors in cybersecurity, uncovering their tactics, techniques, and global impact on digital landscapes.
Exploring Data Collection, Analysis and Security - Hack.lu 2023
Explore data collection, analysis, and security techniques with experts Ventuzelo and Laucournet in this insightful conference talk from Hack.lu 2023.
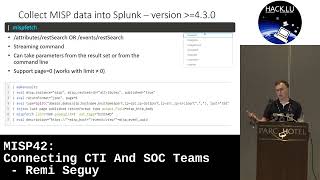
Connecting CTI and SOC Teams - MISP42
Explore strategies for bridging the gap between Cyber Threat Intelligence and Security Operations Center teams, enhancing collaboration and threat response capabilities.
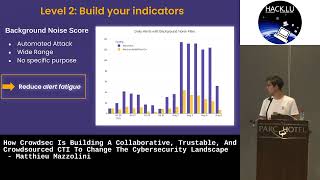
Building a Collaborative, Trustable, and Crowdsourced Cyber Threat Intelligence - Hack.lu 2023
Explore collaborative approaches to building trustworthy, crowdsourced Cyber Threat Intelligence (CTI) in this insightful presentation from Hack.lu 2023.
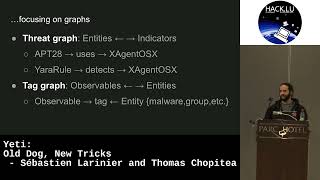
Yeti - Old Dog, New Tricks in Cybersecurity
Explore Yeti's latest advancements in threat intelligence, including new features and capabilities for enhanced cybersecurity analysis and investigation.
Turbocharging IOC Validation - Become a More Efficient CTI Analyst
Enhance your Cyber Threat Intelligence skills with advanced IOC validation techniques, improving efficiency and accuracy in threat analysis and response.