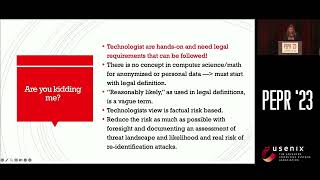
De-identified, Anonymized, or Aggregated Data - A Global Regulatory Comparison
Explores global data protection regulations, focusing on anonymized data challenges. Highlights need for common definitions, risk assessment guidelines, and regulatory clarity in privacy technologies.
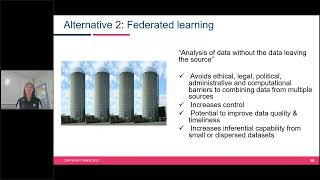
Making Private Data Open and Enhancing Decision-Making Through Digital Atlases
Explore innovative approaches to data sharing, privacy preservation, and decision-making enhancement through digital atlases, focusing on the Australian Cancer Atlas and Bayesian statistical models.
Cyber Resilience Act: Concerns for Open Source Software Development
Explores EU's Cyber Resilience Act's impact on open source software, highlighting concerns about lack of consultation with experts and potential burdens on developers. Discusses Linux Foundation's efforts to address these issues.
Inside the Mind of a Hacker 2023 - Bugcrowd Webinar
Explore hacker insights, AI's impact on cybersecurity, and industry trends with experts. Gain valuable perspectives on ethical hacking, motivations, and the evolving landscape of security research.
Ongoing EvilEye Campaigns Targeting CCP Adversaries
Explore ongoing EvilEye campaigns targeting CCP adversaries, analyzing tactics, targets, and implications for cybersecurity professionals and policymakers.
How Digital Technologies Are Redefining Warfare and Why It Matters
Explore the impact of digital technologies on modern warfare and its implications for global security in this insightful presentation by Mauro Vignati.
Ditch Passwords - Passkeys as the Future of Logins
Explore passkeys as a secure, user-friendly alternative to passwords. Learn how they work, their benefits, implementation considerations, and their role in the future of authentication.

ACME - Benefits of an Internet Security Protocol in Your Network
Explore the advantages of implementing ACME protocol for enhanced network security, focusing on its practical applications and impact on internet safety.
Building an Evil Phone Charging Station
Explore the creation of malicious phone charging stations, understanding potential security risks and vulnerabilities in public charging infrastructure.
Embedded Threats: A Deep Dive Into the eSIM World
Explore the security vulnerabilities and potential threats in embedded SIM technology, uncovering risks and implications for mobile communications and IoT devices.
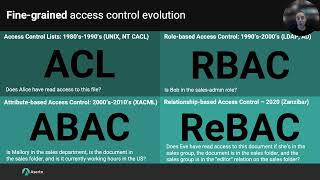
Cloud-Native Authorization Standards
Explore cloud-native authorization standards and their implementation in modern distributed systems for enhanced security and access control.
Beyond Fines and Remediation - A Look at Financial Impacts of Cybersecurity
Explore the hidden financial impacts of cybersecurity incidents, learn to quantify losses, and develop proactive risk management strategies for comprehensive cyber protection.
Remotely Exploiting the ClamAV Antivirus Engine - CVE-2023-20032 Case Study
Explore a case study on exploiting CVE-2023-20032 in ClamAV, demonstrating remote code execution and ASLR bypass techniques applicable to similar antivirus software vulnerabilities.
Ensuring IoC Quality at CERT-FR - Hack.lu 2023
Explore CERT-FR's strategies for maintaining high-quality Indicators of Compromise (IoCs) in cybersecurity incident response and threat intelligence.
Malware AV Evasion Tricks - Cryptography in Malware
Explore advanced malware evasion techniques using cryptography, enhancing your cybersecurity knowledge and defensive strategies against sophisticated threats.
MISP Updates - Hack.lu 2023
Explore the latest updates and enhancements to MISP, the open-source threat intelligence platform, presented by Andras Iklody at Hack.lu 2023.
Why Does the CTI Industry Struggle With Communicating Uncertainties?
Explore challenges in communicating uncertainties within the Cyber Threat Intelligence industry, examining industry practices and potential improvements for more effective risk assessment.
Kunai - A New Threat Hunting Tool for Linux
Discover Kunai, an innovative threat hunting tool for Linux systems. Learn its features, capabilities, and how it enhances cybersecurity through advanced detection techniques.
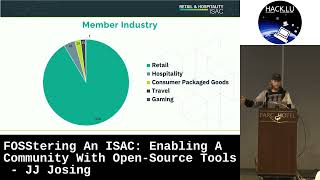
FOSStering an ISAC - Enabling a Community with Open-Source Tools
Explore open-source tools for building an Information Sharing and Analysis Center (ISAC), fostering community collaboration and enhancing cybersecurity threat intelligence sharing.
CTI Is Dead, Long Live CTI - Evolving Threat Intelligence Practices
Explore the evolution and future of Cyber Threat Intelligence (CTI) in this thought-provoking talk, examining its challenges, innovations, and potential impact on cybersecurity strategies.
SBOMs - Are They a Threat or a Menace?
Explore the implications of Software Bill of Materials (SBOMs) in cybersecurity, examining their potential benefits and challenges for software supply chain management.