Calm Down: HTTPS Is Not a VPN
Explore HTTPS limitations, privacy concerns, and security implications in web communications. Learn about packet capture, fingerprinting, and potential vulnerabilities in encrypted connections.
Running a Bug Bounty Program - What You Need to Know
Discover essential insights for running successful bug bounty programs, including strategies, resources, and best practices for effective vulnerability management and rewards.
Scanning with Swagger - Using the Open API Specification to Find Vulnerabilities
Explore leveraging Open API specification for enhanced security scanning, uncovering vulnerabilities and improving application protection strategies.
OWASP CISO Survey Report: Tactical Insights for Managers
Gain tactical insights for managers from OWASP's CISO Survey Report, covering threat sources, risks, trends, investments, challenges, and strategies for effective application security management.
The Timing Attacks They Are A-Changin' - Web-based and Browser-based Timing Attack Techniques
Explore evolving timing attacks in web security, from classic cross-site techniques to browser-based methods, and learn effective mitigation strategies.
Internet Banking Safeguards Vulnerabilities - AppSecEU 2016
Explore internet banking vulnerabilities, attack patterns, and safeguards. Learn about transaction authorization best practices, user authentication, and regulatory requirements for secure online banking.

Video Game Security - Hacking Techniques and Protection Mechanisms
Explore video game hacking techniques, from business risks to memory manipulation, covering client-side and network-based attacks, with insights applicable to various software industries.
Working with the Security Community - A Decade of Evolution
Veteran security expert reflects on a decade of application security evolution, community interactions, and future trends in vulnerability management and response.
Open Source Authentication: Security Without High Cost
Explore strong authentication methods, including one-time passwords and biometrics, to enhance online security. Learn about open-source solutions that reduce costs and improve accessibility for organizations of all sizes.
Fixing the Unfixable: Solving Pervasive Vulnerabilities with RASP
Explore runtime application self-protection (RASP) as a solution for unfixable vulnerabilities like Java deserialization. Learn about RASP approaches and a free, open-source agent to neutralize attacks.
Making Security Agile in CI/CD Environments
Integrating security into agile development and CI/CD pipelines. Learn strategies to automate security processes, leverage QA tests, and utilize tools for improved productivity in application security.
Women in Security - Challenges, Success Factors, and Industry Perspectives
Panel discussion on challenges and success factors for women in security technology, exploring diversity, retention, and industry challenges with insights from four accomplished female leaders.
Skillful, Scalable Full-Stack Security in a State of Constant Flux
Approaches to maintaining secure full-stack posture at scale in changing environments. Discusses automation vs. human testing, analytics in continuous security, and scaling with human validation and intelligence.
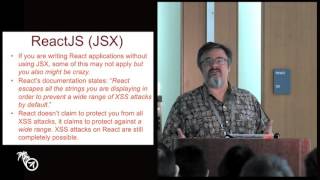
Advances in Secure Coding Frameworks
Explore positive advancements in application security frameworks, highlighting built-in security features that simplify secure coding for developers and improve overall software safety.
Benchmarking Application Security Across Industries
Insights from 200,000+ application assessments reveal industry-specific software security trends, vulnerabilities, and best practices. Benchmark your AppSec program against peers for improved security outcomes.

15 Years of Web Security - The Rebellious Teenage Years
Explore web security's evolution, challenges, and future trends with insights on threat modeling, vulnerability data, and emerging solutions like cyber insurance and security guarantees.
Security Automation in the Agile SDLC - Real World Cases
Explore real-world examples of implementing successful security automation in fast-paced development environments, focusing on agile methodologies, DevOps, and continuous integration for secure software delivery.
Unlocking Threat Modeling - Participatory Session on Security Architecture Assessment
Participatory session demystifying threat modeling for security assessment. Learn risk evaluation, architectural decomposition, and appropriate views to enhance system security from the start.
Adaptive Testing Methodology: Crowdsourced Testing for Customized Target Stack
Discover an efficient, customizable pentesting methodology that adapts to specific technology stacks and time constraints, improving consistency and effectiveness in vulnerability detection.
OCSP Stapling in the Wild - Lecture
Explore OCSP stapling in the wild with experts Devdatta Akhawe and Emily Stark. Learn about TLS security, browser implementations, and real-world challenges in HTTPS ecosystems.
Serverless Security for DevOps and Defenders
Explore serverless architecture's impact on DevOps and security with James Wickett. Learn how this emerging technology enhances defense strategies and streamlines development processes.