The Mobile Malware Maze - 15 Years of Evolution
Explore the 15-year evolution of mobile malware, from Symbian OS to Android, examining shifting trends and current threats in this comprehensive keynote on mobile security.
Enterprise Security - Web Summit 2014
Experts discuss enterprise security challenges and solutions in the digital age, offering insights on cybersecurity trends and best practices for businesses.
Predictive Security - Solving Enterprise Risk Management as a Data Problem
Explore predictive security and enterprise risk management through data-driven solutions with insights from Lookout's co-founder Kevin Mahaffey.
Privacy - The New Fame? Exploring Online Data Security and Personal Privacy
Explore the future of online privacy with experts discussing its importance, potential dangers, legislation, and innovative solutions for protecting personal data in the digital age.
How to Secure Your Software Supply Chain on Windows Server
Explore challenges and solutions for securing software supply chains on Windows Server, focusing on Mirantis Container Runtime's role in providing enterprise-grade security for container workflows and Kubernetes nodes.
Acoustic Intrusions - Exploring Sound-Based Security Vulnerabilities
Explore acoustic intrusion techniques and their implications for cybersecurity. Learn about sound-based vulnerabilities and potential defense strategies.
Hook, Line and Syncer - The Liar for Hire's Ultimate Tacklebox
Explore advanced social engineering techniques and strategies for deception in cybersecurity, featuring expert insights on manipulating human behavior for penetration testing.
Compliance: An Assault on Reason
Explore the critical analysis of compliance frameworks and their impact on cybersecurity practices, challenging conventional wisdom and proposing innovative approaches to risk management.
Adaptive Penetration Testing - Techniques and Strategies
Explore adaptive penetration testing techniques with Kevin Mitnick and Dave Kennedy, covering profiling, bypassing security measures, and innovative attack methods using specialized hardware.
Hackers for Charity Update - Leveraging Hacking Skills for Humanitarian Causes
Discover how hackers use their skills for charitable causes, exploring the latest initiatives and impact of Hackers for Charity in this insightful update.
Cipherspaces and Darknets - An Overview of Attack Strategies
Explore attack strategies on Tor and darknets, covering threat models, encryption layers, DNS leaks, metadata risks, and mitigation techniques for enhanced anonymity.
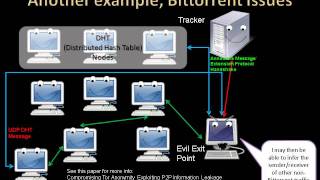
Cipherspaces and Darknets - An Overview of Attack Strategies
Explore attack strategies for cipherspaces and darknets, uncovering vulnerabilities and defense mechanisms in encrypted networks and anonymous communication systems.
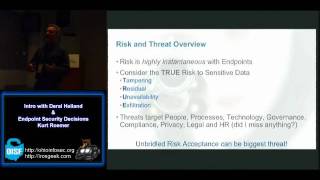
Endpoint Security Decisions in the Age of Consumerization and Mobile Devices
Explore key decisions for managing endpoint risk in the era of consumerization and mobile devices, balancing security with innovation and user experience.
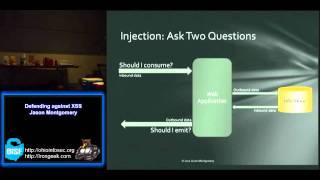
Defending Against Cross-Site Scripting (XSS) Vulnerabilities
Learn to defend against cross-site scripting (XSS) attacks. Covers vulnerability types, injection points, mitigation strategies, and practical demonstrations for developers and security professionals.
Hacking a Mature Security Program
Explore advanced penetration testing techniques for mature security environments, focusing on sophisticated methods to elevate security postures and adapt to evolving threats.
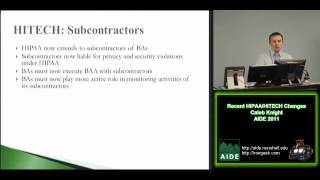
Recent HIPAA/HITECH Changes - Overview and Impact on Health Information Privacy
Overview of HITECH Act and its impact on HIPAA, examining recent changes to broaden protection of personal health information privacy and security in healthcare technology.
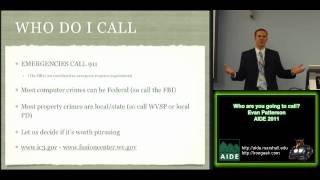
Who to Contact When You Witness a Tech Crime - FBI Guidelines
Learn when, how, and who to contact when witnessing tech crimes, presented by FBI expert Evan Patterson. Gain insights into reporting procedures and appropriate actions for cybercrime situations.
OP-TEE: Using TrustZone to Protect Our Own Secrets
Explore TrustZone technology for securing sensitive data in ARM CPUs, its potential applications, and the open-source OP-TEE implementation for Linux, with insights on current limitations and future possibilities.
Making DevSecOps Happen with Containers - Security Concerns and Solutions
Explore DevSecOps implementation with containers, addressing security concerns through automation and collaboration. Learn to bridge the gap between DevOps and security teams for better application protection.
Read-only Rootfs: Theory and Practice for Embedded Systems
Explore techniques for implementing read-only rootfs in embedded systems, enhancing robustness and facilitating system updates. Learn to manage state storage and overcome challenges in real-world scenarios.
Surviving in the Wilderness: Integrity Protection and System Update for IoT Devices
Explore IoT device security, OTA updates, and integrity protection. Compare approaches like IMA, swupd, dm-verity, and OSTree. Learn implementation using Yocto/OpenEmbedded layers for robust IoT systems.