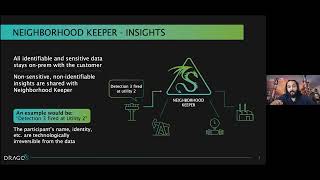
Leveraging ICS Community with Collective Defense and Request for Assistance
Explore collective defense strategies for ICS security through Neighborhood Keeper, facilitating community communication and assistance for enhanced threat visibility and incident response.
OT Cybersecurity for IT Professionals - Understanding ICS Environments
Explore key differences between IT and OT cybersecurity, focusing on unique challenges in industrial control systems and strategies for aligning people, processes, and technology.
Cyber Threats to Oil and Natural Gas Operations - Webinar
Explore cyber threats to oil and gas operations, their impact on industrial technologies and safety, and learn actionable strategies to strengthen ICS/OT cybersecurity across all stages of the industry.
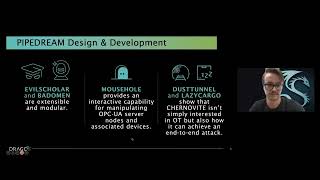
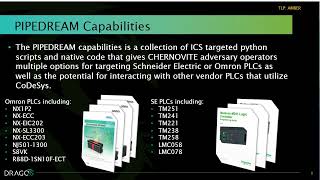
PIPEDREAM Malware and the CHERNOVITE Activity Group - Industrial Control Systems Cybersecurity
Detailed analysis of PIPEDREAM, an ICS-specific malware capable of disrupting industrial environments. Experts discuss components, capabilities, impacted devices, and mitigation strategies.
Cyber Resiliency in the Power Industry - Strategies and Perspectives
Explore power industry cyber resiliency strategies, challenges, and implementation across IT/OT systems. Learn to incorporate resilience into security programs for better threat preparedness and response.
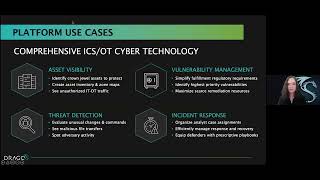
Improving OT Threat Visibility on CHERNOVITE's PIPEDREAM Malware - Dragos Platform Webinar
Explore PIPEDREAM malware's impact on ICS/OT environments, learn detection strategies, and discover mitigation steps using the Dragos Platform for enhanced OT threat visibility.
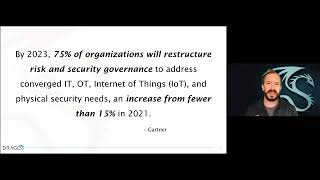
Starting Your Journey: A Roadmap for ICS/OT Cybersecurity
Explore ICS/OT cybersecurity essentials, from risk identification to program building. Learn strategies to protect critical infrastructure and align your organization's cybersecurity efforts for enhanced safety and reliability.
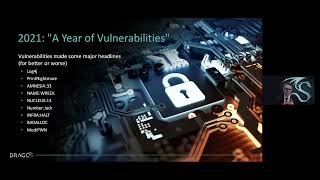
2021 ICS/OT Cybersecurity Vulnerability Briefing - Year in Review
Comprehensive analysis of 2021 ICS/OT vulnerabilities, offering insights on trends, high-profile cases, and actionable guidance for prioritizing and addressing cybersecurity risks in industrial environments.
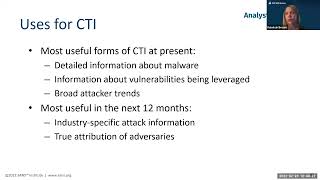
SANS 2022 Cyber Threat Intelligence Survey - Key Findings and Adaptations
Explore shifts in cyber threat intelligence due to workplace changes, its role in ransomware response, and preparation for unpredictable events with severe consequences.
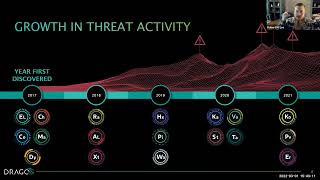
2021 ICS/OT Cybersecurity Year in Review - Executive Briefing
Comprehensive analysis of ICS/OT cybersecurity trends, threats, and vulnerabilities in 2021, offering insights on new activity groups, incident responses, and data-driven recommendations for safeguarding industrial operations.
5 Lessons for Integrating OT Threat Intelligence - 2022
Discover key insights on integrating operational technology threat intelligence, enhancing cybersecurity strategies for industrial control systems and critical infrastructure protection.
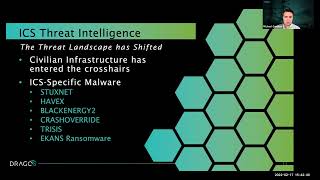
How to Operationalize ICS Threat Intelligence for Defenders
Discover strategies to leverage ICS threat intelligence for enhanced cybersecurity in industrial environments. Learn practical use cases and implementation techniques for effective defense against evolving threats.
The 4 Qualities of Good Cyber Threat Intelligence
Explore the four key qualities of effective cyber threat intelligence for industrial environments, focusing on actionable insights and industry-specific threats.
Navigating the 2022 NDAA and Its Impact on ICS/OT Cybersecurity
Explore key requirements for Operational Technology in the 2022 NDAA, including building a complete picture of ICS/OT environments and establishing safe data transfer between IT and OT systems.
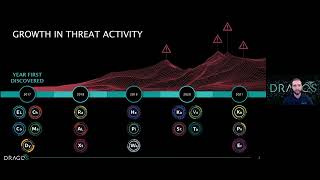
2021 ICS/OT Cybersecurity Threat Landscape Review
Explore the 2021 ICS/OT cybersecurity landscape, including new threat groups, ransomware trends, and notable incidents. Gain insights to better safeguard industrial control systems and operational technologies.
Mastering the Maze - Reinforcement Learning for Automated Penetration Testing
Explore how reinforcement learning can revolutionize penetration testing by automating lateral network movement and identifying attack vectors, enhancing efficiency in cybersecurity assessments.

CommandGPT: Using ChatGPT for C2 and Post-Exploitation - Lecture 13
Explore CommandGPT's potential in offensive security, leveraging AI for dynamic code generation in command and control frameworks and simulating ransomware techniques.
The Pros and Cons of Encrypted Client Hello
Explore the advantages and challenges of Encrypted Client Hello (ECH) in TLS, including its impact on privacy, security, and network infrastructure.

Red Team Tales: 7 Years of Physical Penetration Testing
Explore real-world physical penetration testing experiences across diverse facilities, from banks to cheese factories. Gain insights into security vulnerabilities and unconventional tactics used in red team operations.
Attack Surface and Security Implications of eSIM Technology
Explore the security vulnerabilities and potential risks associated with eSIM technology in mobile phones and desktop devices, raising awareness about offensive operations and post-compromise scenarios.
Reverse Engineering an EV Charger - Zaptec Pro Analysis
Dive into the reverse engineering process of a popular EV charger, exploring firmware analysis, custom bootloader creation, and potential security improvements in this insightful presentation.