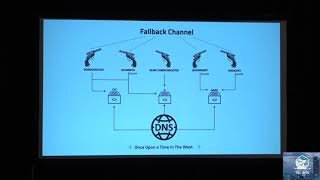
Once Upon a Time in the West - A Story on DNS Attacks
Explore DNS attack techniques used by notorious hacking groups, examining their tools and patterns to improve detection and defense strategies against evolving cyber threats.
Magecart - A Growing Threat to E-Commerce Sites
Explore Magecart's e-commerce threats, attack techniques, and defense strategies. Learn about vulnerabilities, compromises, and protective measures for online shops and payment systems.
Bringing Rapid Prototyping to the Threat Model Process
Discover rapid threat modeling for Agile/DevOps environments, enhancing software security design tenfold through efficient risk analysis and automated workflows.
How Online Dating Made Me Better at Threat Modeling
Explore threat modeling through online dating, balancing privacy and human connection. Learn best practices for safer digital interactions and gain insights into core security principles.
Uninvited Guests - Understanding Malicious Web Bots with OWASP Handbook
Explore malicious web bots and automated threats using OWASP's Handbook. Learn about scalping, scraping, and sniping, with real-world examples and countermeasures for better online security.
Dissecting Mobile Application Privacy and Analytics
Explore mobile app data collection, privacy concerns, and analytics practices. Learn to assess and safeguard personal and client information in popular applications.
What Do You Mean Threat Model Every Story
Explore integrating threat modeling into continuous development, focusing on methodology, developer education, and reflecting evolving systems in fast-paced environments.
The Importance of the Cloud and the Developers Communities in Fighting Cyber Crime
Explore cloud and AI's role in cybersecurity, innovative trends, and Microsoft's strategies to combat evolving cyber threats in this insightful talk by a leading industry expert.
DevSecOps with OWASP DevSlop
Learn DevSecOps through hands-on examples with OWASP DevSlop. Explore secure component management, secret handling, testing techniques, and open-source tools to enhance your pipeline security.
Common API Security Pitfalls
Explore common API security pitfalls, their root causes, and best practices for protection. Learn to assess and improve API security, focusing on authentication, encryption, and input validation.
Temporal - It's Not Your Developers' Fault
Explore how software development evolution impacts security, from traditional methods to Cloud Native workloads, and why increasing breaches aren't solely developers' responsibility.
Temporal - The Future of DevSecOps Transformation
Explore the future of DevSecOps transformation, covering Agile methodologies, new roles, maturity models, and innovative approaches to pipeline engineering and quality feedback.
Temporal - Code-Origin Policy - Towards a Formal User Privacy Protection for the Web
Explore a novel approach to web privacy protection through code-origin monitoring, offering customizable user safeguards and formal assurance mechanisms for JavaScript execution.
Temporal - Achieving the Web Isolation Nirvana - How Far Along Are We?
Explore web isolation's evolution, current approaches, and future challenges. Learn about a client-side sandboxing solution and discuss the future of web application security.
Temporal - Security As Code - The New Model Of Achieving Security At Scale
Explore the concept of Security-as-Code, a scalable approach to implementing security controls through codification, automation, and software engineering practices.
Temporal - Redefining Threat Modeling - Security Team Goes on Vacation
Explore innovative self-serve threat modeling techniques that empower development teams to identify and mitigate security risks independently, enhancing overall application security and efficiency.
Temporal - AppSec Timeline - Wins, Failures, Promises, and Predictions
Explore AppSec's 20-year journey: achievements, setbacks, and future prospects. Analyze trends, evaluate DevSecOps impact, and gain insights into the evolving landscape of application security.
AppSec - From Outsiders to Allies
Chris Wysopal explores AppSec's evolution from hacker-driven to a critical ally in software development, emphasizing the need for collaboration, shared accountability, and integrated security practices in modern development processes.
Extending WAFs at the Application Layer
Explore application-level security control with Sanwaf, an alternative to traditional WAFs. Learn its structure, datatypes, and implementation for enhanced web application protection.
Social Media Botnet Detection with Linkage Analysis and Machine Learning
Explore techniques for detecting social media spam botnets using linkage analysis and machine learning, covering unsupervised and semi-supervised approaches and their applications.
Why Developers Struggle with AppSec
Explore challenges developers face in application security, trust issues, and solutions for integrating security into the development process, with insights on tools and production biases.