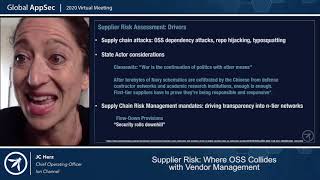
Supplier Risk - Where OSS Collides With Vendor Management
Explore the intersection of open source software and vendor management, focusing on supplier risk, regulatory mandates, and strategies for mitigating potential threats in the software supply chain.
Yes, You Too Can Break Crypto - Exploiting Common Crypto Mistakes
Explore common cryptographic vulnerabilities and learn practical techniques to exploit them, enhancing your understanding of secure implementation and potential attack vectors.
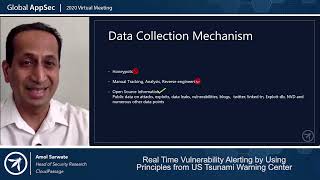
Real Time Vulnerability Alerting by Using Principles from the United States Tsunami Warning Center
Learn how to implement real-time vulnerability alerting using principles from the US Tsunami Warning Center, covering triage methods, data analysis, and prioritization techniques.
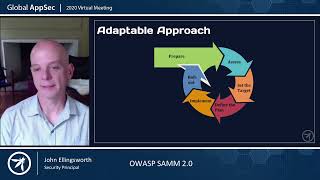
OWASP SAMM 2 - Your Dynamic Software Security Journey
Explore OWASP SAMM 2, a dynamic framework for software security. Learn principles, assessment tools, and critical success factors to enhance your organization's security maturity.
OWASP IoTGoat Project Overview and Roadmap
Explore IoTGoat, an OWASP project for IoT security testing. Learn about hardware compatibility, vulnerabilities, and hands-on techniques like firmware extraction and password cracking.
Magecart 2020 - The New Face of XSS
Explore Magecart's evolution, injection techniques, and threat complexity. Learn from real-world case studies and discover strategies to prevent these sophisticated web skimming attacks.
MLSec Going Deeper
Explore advanced machine learning security concepts, including adversarial samples, attack strategies, and defensive techniques for various ML models.
Enabling Message Level Protection at Uber
Explore Uber's approach to message-level protection, including encryption strategies, crypto interfaces, and developer evangelism for secure data handling at scale.
Application Logging in the Era of GDPR
Explore GDPR-compliant application logging practices, data privacy laws, and effective strategies for protecting sensitive information in production logs.
Insider Threat Detection & Automation by Behaviour Analytics
Learn to detect and automate insider threat prevention using behavior analytics, exploring UEBA, anomalies, and data-driven techniques for enhanced cybersecurity.
A Dancefloor that is Literally Just Banana Peels - AppSec Awareness Program Pitfalls
Explore common pitfalls in AppSec awareness programs and learn effective strategies for implementation, audience engagement, and sustainable security education.
Before It's Out the Door - Securing Outbound Open Source
Explore strategies for securing open-source projects before release, covering governance, code review, and infrastructure. Learn to address security concerns and manage community projects effectively.
HTTP3 Security
Explore HTTP3 security with Robin Marx: handshakes, QuickSense, passive proxies, deep packet inspection, and QUIC vs TCP. Gain insights into the latest web protocol advancements.
Insecure Deserialization, and How Not to Do It
Explore secure deserialization techniques and common vulnerabilities with practical demos, focusing on session cookies and big vulnerabilities in various platforms.
The Now and the Future of Malicious WebAssembly
Explore WebAssembly's evolution, performance, and security implications, including its use in cryptojacking and potential future developments in web-based attacks.
OWASP Based Threat Modelling - Creating A Feedback Model in an Agile Environment
Learn to create an effective threat modeling feedback system in Agile environments using OWASP principles. Explore frameworks, processes, and strategies for risk management and application security.
Fast Forwarding Mobile Security With The OWASP Mobile Security Testing Guide
Explore mobile security essentials, including OWASP's Mobile AppSec Verification Standard and Testing Guide. Learn about network communication, data storage, and privacy requirements for robust app protection.
Breaches Are Everywhere - What’s A Good Security Leader To Do?
Explore strategies for security leaders to combat increasing breaches, from IoT vulnerabilities to phishing attacks. Learn essential skills and best practices for effective cybersecurity management.
Securing The Future
Explore the future of cybersecurity with Mikko Hypponen, covering topics like data value, governmental attacks, cyber warfare, and emerging technologies like deepfakes and machine learning for defense.
Restricting the Scripts, You're to Blame, You Give CSP a Bad Name
Explore Content Security Policy's role in web security, covering script restrictions, TLS enforcement, and framing control. Learn best practices and developer insights for effective CSP implementation.
Practical OWASP CRS in High Security Settings
Learn to implement OWASP Core Rule Set for high-security web applications, covering WAFs, ModSecurity, logging, whitelisting, and advanced protection techniques.