Choosing the Right Static Code Analyzers Based on Hard Data
Learn to select effective static code analyzers using data-driven insights, exploring tool capabilities, integration, coverage, and result quality for improved software security.
How Do JavaScript Frameworks Impact The Security Of Applications
Explore JavaScript frameworks' impact on application security, analyzing mitigation levels, case studies, and CSRF protection across popular frameworks like Meteor.
Modern and Secure IAM for Modern Applications
Explore modern IAM strategies for enhanced application security, covering OpenID, JSON Web Tokens, SAML, and FIDO protocols, with practical insights and a demo.
Controlled Mayhem With Cloud Native Security Pipelines
Explore cloud-native security pipelines, comparing traditional and modern approaches, while addressing challenges in container orchestration, access control, and CI/CD processes.
Web Apps vs Blockchain DApps - Tools, Vulns And Standards
Explore the security aspects of decentralized applications (DApps) and smart contracts, covering tools, vulnerabilities, and standards across the development lifecycle.
The Woman Who Squashed Terrorists - When An Embassy Gets Hacked
Discover how a cybersecurity expert thwarted a terrorist hack on an embassy, exploring the incident's origins, diplomatic implications, and crucial lessons for global security.
Security Vulnerabilities Decomposition - Another Way to Look at Vulnerabilities
Explore security vulnerabilities decomposition, focusing on SQL injection, secure data handling, and design patterns for payment gateways and single sign-on. Learn practical security controls for secure development.
The Insecurity Caused by Trusting Your Client-Side Storage
Explore vulnerabilities in client-side storage, including cookies and web storage, and learn exploit patterns and attack vectors to enhance web application security.
The State of Credential Stuffing and the Future of Account Takeovers
Explore credential stuffing, account takeovers, and evolving cybersecurity threats. Learn about attack methods, defense strategies, and the future of online fraud prevention.
Applying Security Engineering Principles to Complex Composite Systems
Explore security engineering principles for complex systems, focusing on composite elements, interactions, and dependencies across the system lifecycle, illustrated with a Smart City transit example.
XSS is Dead - We Just Don't Get It
Exploración crítica de la persistencia del XSS, analizando su historia, fracasos en su mitigación y factores que contribuyen a su continuidad. Se cuestiona su relevancia actual y se proponen reflexiones sobre el futuro de la seguridad web.
Attacking Modern Web Technologies
Explore modern web vulnerabilities with top hacker Frans Rosén. Learn about exploiting postMessage, WebSockets, cloud misconfigurations, and more. Gain insights to enhance your web security knowledge.
From Rogue One to Rebel Alliance - Building Developers into Security Champions
Learn to transform developers into security champions, scaling your AppSec efforts. Discover recruitment strategies, training techniques, and success metrics for building a robust security program within development teams.
Detecting and Preventing Malicious Domain Registrations in the .eu TLD
Análisis exhaustivo de registros de dominios maliciosos en .eu, explorando campañas cibercriminales y presentando un sistema de predicción para detectar y prevenir registros maliciosos antes de que causen daño.
Injecting Security Controls in Software Applications
Explore techniques for integrating security controls into software development, focusing on real-world examples, actionable advice, and verification methods to build more secure applications.
Can We Automate Security?
Explore Microsoft's CI/CD pipeline security tools and lessons learned, focusing on automation strategies to enhance product and service security in the development process.
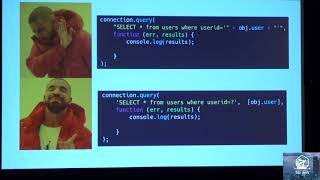
OWASP Top 10 for JavaScript Developers
Explore JavaScript vulnerabilities in OWASP Top 10, covering client and server-side issues with focus on modern frameworks and NodeJS. Learn prevention techniques for secure web development.
Protecting a High Profile Enterprise
Strategies for protecting high-profile enterprises, drawing from 20+ years of experience. Covers choosing the right security approach, application security's role, and effective management techniques.

Vehicle Security Trends - Implications for Automotive Suppliers
Explore automotive security trends, attack surfaces, and mitigation strategies for suppliers in the era of connected and autonomous vehicles. Learn about third-party risks and development process improvements.
Building & Hacking Modern iOS Apps
Explore iOS app security from both developer and hacker perspectives, covering secure development practices, vulnerability assessments, and insights into Apple's latest security features.
Testing and Hacking APIs
Learn techniques for testing and exploiting API vulnerabilities, including understanding implementation, detecting weak points, and conducting effective penetration tests on modern applications.