Unlocking Any Door in 21st Century - Immersion in Bio-Security
Explore biometric authentication vulnerabilities, AI/ML risks, and creative hacking techniques. Learn about data privacy threats and strategies to bypass liveness checks in modern security systems.
Single Instruction Multiple Data Leaks in Cutting-edge CPUs - AKA Downfall
Unveiling Downfall attacks: new transient execution vulnerabilities in Intel CPUs. Exploits Gather instruction to leak data across security boundaries, defeating previous defenses and necessitating critical hardware fixes.
Craig's Angular - Rust Spectacular
Explore Rust programming from an Angular developer's perspective, comparing it to TypeScript and discussing its potential impact on front-end development.
Downfall - Exploiting Speculative Data Gathering
Unveiling Downfall attacks: new transient execution vulnerabilities exploiting gather instructions on x86 CPUs, compromising security across various computing environments and defeating existing defenses.

Jtagulator - Assisted Discovery of On-Chip Debug Interfaces
Explore on-chip debug interfaces and JTAG architecture with JTAGulator, a hardware tool for identifying and accessing embedded systems' debug ports.
Hardware Tamper Resistance - Why and How
Explore hardware tamper resistance techniques, from physical systems to electronic solutions, and learn about new approaches like machine-verifiable seals and secure multiparty computation.
Building a Modern Security Engineering Organization
Learn strategies for building an effective security engineering team, focusing on modern approaches to protect against evolving threats in today's dynamic technology landscape.
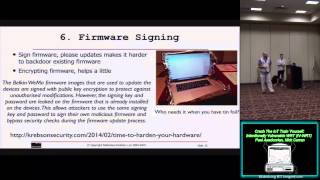
Crash the IoT Train Yourself - Intentionally Vulnerable WRT IV WRT
Explore IoT device vulnerabilities, including firmware backdoors, default credentials, and web interface flaws. Learn about common security risks and see live demonstrations of exploits.

Wolf in Shell's Clothing - Why You Should Be Skeptical of Your Trusted Tools
Explore the skepticism towards trusted security tools, data breaches, and vulnerabilities. Learn about manual hijacking, drive-by downloads, and strategies to enhance network protection.
Identifying and Exploiting Hardware Vulnerabilities - Demo of the HRES Process
Demonstration of the HRES process for identifying and exploiting hardware vulnerabilities, showcasing practical techniques and methodologies.
Its Too Funky In Here - IDS - IPS Choices Benefits Drawback and Configurations ForgottenSec
Explore IDS/IPS systems, their benefits, drawbacks, and configurations. Learn about security engineering, deployment strategies, and future steps in network security monitoring.
IoT Defenses - Software, Hardware, Wireless, and Cloud
Explore comprehensive IoT security strategies across software, hardware, wireless, and cloud domains, enhancing your ability to protect interconnected devices and systems.
Securing Trust - Defending Against Next Generation Attacks
Explore next-gen cybersecurity threats and defense strategies, focusing on digital certificates, SSH, and foundational security measures to protect against evolving attacks.
I've Got a Pocket Bone to Pick with You
Explore USB gadget functionality on embedded Linux systems, covering mass storage impersonation and HID device creation for security testing and penetration scenarios.
Flush, Gauss, and Reload - A Cache Attack on the BLISS Lattice-Based Signature Scheme
Explore a cache attack on the BLISS lattice-based signature scheme, examining vulnerabilities and potential security implications for post-quantum cryptography.
Run Time Accessible DRAM PUFs in Commodity Devices
Explore DRAM-based Physical Unclonable Functions (PUFs) in everyday devices, their implementation, and potential applications for enhanced security and device authentication.
Message Transmission with Reverse Firewalls - Secure Communication on Corrupted Machines
Explore secure communication on corrupted machines through reverse firewalls, addressing algorithm substitution attacks and perandomizable hybrid encryption for enhanced message transmission protocols.
Verified Drop in Replacements for TLS & HTTPS
Explore secure alternatives to TLS and HTTPS protocols with expert Cedric Fournet, focusing on verified drop-in replacements for enhanced cybersecurity.
The First Thorough Side Channel Hardware Trojan
Explore the groundbreaking research on side channel hardware trojans, examining their potential impacts and detection methods in cryptographic systems.
Key Extraction Using Thermal Laser Stimulation - A Case Study on Xilinx Ultrascale FPGAs
Explore thermal laser stimulation for key extraction on Xilinx Ultrascale FPGAs, examining vulnerabilities and potential security implications in hardware cryptography.
Stealthy Opaque Predicates in Hardware - Obfuscating Constant Expressions at Negligible Overhead
Explores hardware-based obfuscation techniques for constant expressions, presenting a novel approach with minimal overhead. Discusses applications in watermarking and security.