Building a Forensic Toolkit That Will Protect You From Evil Influences
Explore techniques for secure forensic analysis of compromised systems, focusing on creating a protected environment and essential utilities for Solaris and Windows NT investigations.
The Info Leak Era on Software Exploitation
Explore advanced techniques for exploiting software vulnerabilities through information leaks, focusing on defeating ASLR and converting various vulnerabilities into effective info leaks.
Hardware Backdooring is Practical
Explores hardware backdooring through Rakshasa malware, demonstrating permanent BIOS infection, NX bit disabling, and security lowering across various motherboards using open-source components like Coreboot.
Mission mPOSsible
Explore vulnerabilities in mobile payment systems, including code execution through various input vectors. Live demonstrations showcase attack methods, emphasizing security weaknesses in current mPOS solutions.
USB Attacks Need Physical Access Right? Not Any More
Explore remote USB attacks, their implications, and defense strategies in this eye-opening presentation on evolving cybersecurity threats.
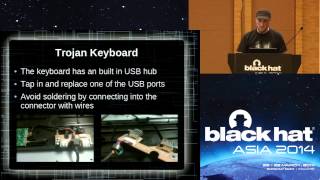
Building Trojan Hardware at Home
Learn to create and detect hardware-based trojans using everyday devices. Explore techniques for modifying hardware, embedding malicious code, and understanding countermeasures against these threats.
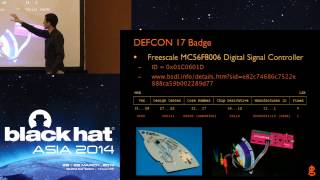
Discovering Debug Interfaces with the JTAGulator Part 2
Explore JTAG debugging interfaces, learn about data registers, state machines, and protection mechanisms. Hands-on demonstrations with various devices and UART scanning techniques.
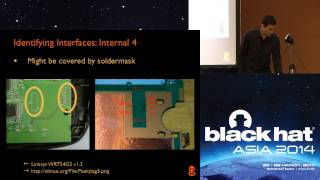
Discovering Debug Interfaces with the JTAGulator Part 1
Explore debug interfaces and hardware hacking techniques using the JTAGulator, a versatile tool for discovering and exploiting hidden system access points.
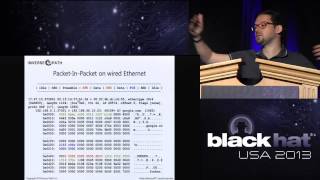
Fully Arbitrary 802.3 Packet Injection - Maximizing the Ethernet Attack Surface
Explore novel Ethernet attack techniques using affordable hardware and custom firmware. Learn about frame manipulations, SFD parsing anomalies, and Ethernet Packet-In-Packet injection for enhanced network security testing.
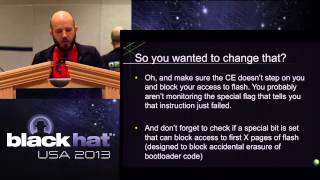
Teridian SoC Exploitation - Harvard Architecture Smart Grid Systems
Exploitation techniques for Teridian 8051-based SoCs in smart grid systems, covering architecture, security barriers, and methods to gain code execution and firmware access.
Power Analysis Attacks for Cheapskates
Discover affordable power analysis attack techniques for cryptographic systems using open-source hardware and software. Learn to set up a budget-friendly lab and perform live demonstrations against AES implementations.
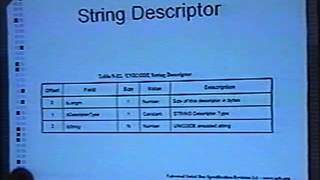
Plug and Root - The USB Key to the Kingdom
Explore USB device vulnerabilities and potential security risks in computer systems, focusing on automated attacks and defense strategies.
Injecting Malware into iOS Devices via Malicious Chargers
Demonstration of iOS device vulnerability through malicious chargers, bypassing security mechanisms to inject arbitrary software within one minute of connection, using a proof-of-concept called Mactans.
Hiding at Depth - Exploring, Subverting and Breaking NAND Flash Memory
Explore NAND Flash vulnerabilities, learn to hide and discover files on mobile devices, and understand implications for digital forensics and device security. Open-source tools for Android demonstrated.
Multiplexed Wired Attack Surfaces
Explore techniques for accessing mobile device interfaces through multiplexed wired connections, including gaining shell access and using open-source tools for interface exploration.
All You Always Wanted to Know About Antiviruses
Demystifying antivirus software: internals, detection methods, and trade-offs. Explores AV engines, whitelists, signatures, real-time monitoring, and network inspection across Windows, Linux, and Android platforms.
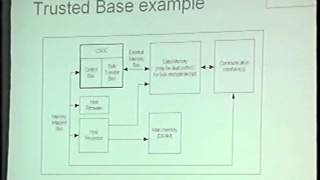
Secure Hardware Design
Explore secure hardware design principles and techniques with experts Kingpin and Brian Oblivion, focusing on protecting electronic systems from vulnerabilities and attacks.
Container Security
Explore container security fundamentals, shared kernel implications, and best practices with experts Liz Rice and Eoin Woods. Learn to assess and mitigate risks in containerized applications.

A Security RISC? The State of Microarchitectural Attacks on RISC-V
Systematic investigation of microarchitectural attack surface on 64-bit RISC-V CPUs, exploring vulnerabilities and security implications as RISC-V architecture gains popularity in commercial processors.
Lost Control - Breaking Hardware-Assisted Kernel Control-Flow Integrity with Page-Oriented Programming
Explore techniques to bypass hardware-assisted kernel control-flow integrity using page-oriented programming, revealing vulnerabilities in modern operating system security mechanisms.
Cracking With Automated USB Fuzz
Explore automated USB fuzzing techniques to detect vulnerabilities in computer systems, including simulating USB cameras and exploiting Windows Hello using infrared images.