Exploiting QSEE, The Raelize Way
Exploiting vulnerabilities in Qualcomm's Trusted Execution Environment through software and hardware attacks, achieving arbitrary code execution and compromising device security.
Jailbreaks Never Die - Exploiting iOS 13.7
Unveiling iOS 13.7 exploit chain: kernel vulnerabilities, mitigation bypasses, and techniques for reading/writing kernel memory. Insights into iOS security research and jailbreak development.
God Mode Unlocked - Hardware Backdoors in x86 CPUs
Unveiling a critical hardware backdoor in x86 CPUs allowing unprivileged users to bypass security checks and escalate to kernel-level access. Explores detection, prevention, and broader implications for processor security.
Software Security Era - Past, Present, and Future
Explore the evolution of memory corruption exploitation, from early techniques to modern mitigations. Includes live demos of vulnerabilities and discusses the ongoing challenges in software security.
Pwning ARM Debug Components
Exploring ARM debug components for security primitives and information flow tracking. Demonstrates a portable approach to enhance runtime security monitoring in ARM-based systems.
Firmware Hacking With Ghidra
Hands-on firmware hacking workshop using Ghidra for reverse engineering ARM Cortex-M architecture, followed by live demonstration of hardware glitching attacks on microcontrollers.
Securing Your Laptop Like You Mean It
Comprehensive guide to advanced laptop security, covering hardware virtualization, secure boot, and protection against sophisticated physical attacks. Practical tips for privacy-conscious users and security professionals.
HDMI - Pwning HDMI For Fun And Profit
Explore HDMI vulnerabilities through protocol analysis, fuzzing techniques, and real-world exploitation, showcasing potential security risks in AV devices and demonstrating practical attack vectors.
Intrusion-Detection on the HW Bus
Explore innovative hardware-based intrusion detection techniques for enhanced system security, focusing on monitoring and analyzing hardware bus activity.
Multidimensional HW Attack and Defense Toolset
Explore multidimensional hardware attack and defense strategies with a comprehensive toolset, enhancing cybersecurity knowledge for both offensive and defensive applications.
Hardware Side Channels in Virtualized Environments
Explore hardware side channel vulnerabilities in virtualized environments, focusing on cloud-based attacks. Learn about attack surfaces, demonstrations, and potential mitigations for these security risks.
PG - I Club and So Can You
Learn to start and run an "I Club" for sharing knowledge and skills in computer security, with practical tips on logistics, advertising, and community building.
PG - I Club and So Can You
Learn to start and run an "I Club" for cybersecurity enthusiasts, fostering community learning and skill development through shared experiences and competitions.
Exploiting a Limited UAF on Ubuntu 22.04 to Achieve LPE
Detailed exploration of exploiting a Linux kernel vulnerability in Ubuntu 22.04 to achieve local privilege escalation, focusing on advanced exploitation techniques and bypass methods.
Hack In The Studio - Fireside Chat
Fireside chat with security experts Cristofaro Mune and Adam Laurie, discussing their extensive experience in hardware hacking, embedded systems security, and reverse engineering techniques.
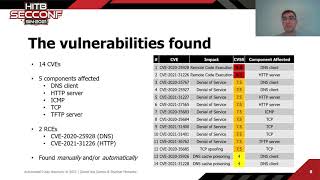
Squashing Low-hanging Fruit in Embedded Software
Discover advanced techniques for identifying and mitigating critical vulnerabilities in embedded systems, focusing on NicheStack TCP/IP stack vulnerabilities and automated vulnerability detection methods.
Exploiting UAF by Ret2bpf in Android Kernel
Exploiting a 10-year-old Use-After-Free vulnerability in Android's xt_qtaguid kernel module, demonstrating local privilege escalation on Mi9 device using ret2bpf technique to bypass protections.
Don't Get Owned by Your Dependencies
Explore innovative techniques for mitigating memory safety vulnerabilities in third-party C libraries, focusing on Firefox's lightweight in-memory sandboxing approach and the RLBox framework for efficient, secure application development.
Make Sure DSA Signing Exponentiations Really Are Constant-Time
Explore constant-time DSA signing exponentiations for enhanced cryptographic security. Insights from experts on mitigating timing attacks in digital signature algorithms.
High-Throughput Semi-Honest Secure Three-Party Computation with an Honest Majority
Explore high-throughput secure three-party computation with an honest majority in this presentation on advanced cryptographic protocols and their practical applications.
BeleniosRF - A Non-Interactive Receipt-Free Electronic Voting Scheme
Explore a non-interactive receipt-free electronic voting scheme, BeleniosRF, enhancing election integrity and voter privacy through advanced cryptographic techniques.