
Why Do Keynote Speakers Keep Suggesting That Improving Security Is Possible
Humorous critique of tech industry's approach to security, highlighting flaws in machine learning, AI, and IoT while advocating for ethical computing and thoughtful development.
Looking for Malicious Hardware Implants with Minimal Equipment
Explore hardware security threats, detection methods, and threat modeling with minimal equipment. Learn to identify unexpected features and understand the challenges of hardware implants and interdiction.
Securing Bare Metal Hardware at Scale
Explore advanced techniques for securing firmware in large-scale hardware deployments, addressing challenges and future trends in protecting against persistent backdoors and exploits.
Adventures in Hardware Hacking or Building Expensive Tools on a Budget
Explore hardware hacking techniques like CT scanning and chip decapping for non-destructive device analysis, circuit reconstruction, and vulnerability identification in embedded systems and access control.
The Effect of Entertainment Media on Mental Models of Computer Security
Explores how entertainment media shapes people's understanding of computer security, identifying misconceptions from fictional tropes and examining how viewers evaluate realism in portrayals.
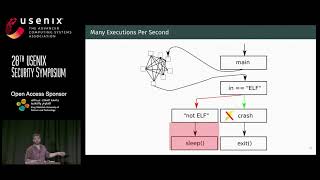
AntiFuzz - Impeding Fuzzing Audits of Binary Executables
Explore techniques to protect binary executables against automated bug-finding tools, focusing on impeding fuzzing, symbolic execution, and hybrid fuzzing approaches while maintaining performance.
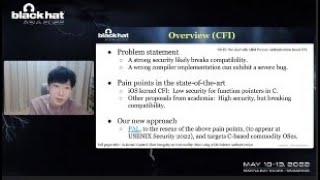
Taking Kernel Hardening to the Next Level
Explore advanced kernel hardening techniques, focusing on CFI and UAF defense. Learn about new approaches to enhance OS security against evolving exploitation methods.
One Glitch to Rule Them All - Fault Injection Attacks Against the AMD Secure Processor
Explore fault injection attacks on AMD's Secure Processor, revealing vulnerabilities in CPU security and discussing implications for system integrity and trust.
The Art of Exploiting UAF by Ret2bpf in Android Kernel
Explore Android kernel exploitation techniques, focusing on a Use-After-Free vulnerability in xt_qtaguid. Learn about KASLR bypass, rooting methods, and security measures against such attacks.
POSWorld - Should You Be Afraid of Hands-On Payment Devices
Explore the vulnerabilities of Point of Sale terminals, uncovering security flaws in hardware, software, and file systems that enable cloning and fraud in the dark market.
Secret Flaws of In-DRAM RowHammer Mitigations
Unveiling secret flaws in DRAM RowHammer mitigations, exploring Target Row Refresh implementation, and introducing TRRespass: a RowHammer fuzzer for creative hammering patterns to bypass protections.
DHCP Is Hard
Explore DHCP vulnerabilities and exploits in popular implementations, including dnsmasq, ISC DHCP, and systemd networkd, with insights on architecture and attack techniques.
More Libraries! More Vulnerabilities! More Things! Now with Real World Case Studies
Explore real-world case studies on library vulnerabilities, their impact, and mitigation strategies. Gain insights into security challenges and learn about industry responses and financial implications.
Drammer - The Making Of
Exploración técnica del ataque Drammer, que aprovecha la vulnerabilidad Rowhammer en dispositivos Android sin permisos de usuario ni fallas de software. Detalla el proceso de desarrollo y los desafíos enfrentados.
Fault Injection Attacks on Secure Boot
Exploring fault injection attacks on secure boot, this talk introduces techniques, impacts, and practical mitigation strategies for embedded systems security, with real-world examples and key takeaways.
Adaptive Android Kernel Live Patching
Adaptive Android kernel live patching framework for securing devices against vulnerabilities, enabling hotpatching without source code access and automatic adjustment to different models and versions.
Bypassing Hardware-Based Trusted Boot Through x86 Downgrade
Exploiting microcode loader vulnerability to downgrade CPU microcode, enabling attacks on Intel security technologies like Boot Guard and TXT by loading older, vulnerable versions of Authenticated Code Modules.
Auditable & Provable Privacy of Smart Speakers
Explore smart speaker privacy vulnerabilities, including skill squatting and eavesdropping, and learn about potential solutions like hardware mic disconnects and user awareness.
Page Fault Liberation Army
Explore x86 processor memory translation logic and MMU as a Turing-complete processor. Learn about innovative security approaches and computational possibilities in virtual memory systems.
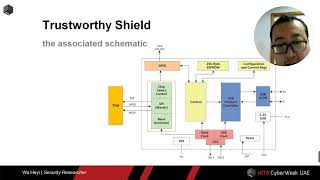
Trustworthy Shield – A Cheap TPM Module for Older Systems
Explore a cost-effective TPM module for older systems, enhancing security without hardware changes. Learn about trusted computing technology and its applications in IoT and embedded systems.
The Evolving Attack Surface
Explore the expanding vulnerabilities in industrial control systems, from traditional security to blockchain, with insights on hardware attacks, supply chain risks, and network hijacking.