AppArmor
Explore AppArmor's security features, development process, and integration with LxD, guided by Canonical security expert John Johansen.
Fatal Fury on ESP32 - Time to Release Hardware Exploits
Methodical exploration of defeating ESP32 security features using low-cost hardware techniques, including voltage glitching and analog side-channels, with implications for IoT device security.
Attacking Hardware Systems Using Resonance and the Laws of Physics
Explore resonant frequencies to subvert electronic systems, challenging assumptions about hardware security and demonstrating vulnerabilities in supposedly secure components.
WebAssembly - A New World of Native Exploits on the Browser
Explore WebAssembly's security risks, low-level semantics, and potential vulnerabilities in browser-based applications. Learn about linear memory, function tables, and mitigation strategies.
Securing Your In-Ear Fitness Coach - Challenges in Hardening Next Generation Wearables
Explore security challenges and solutions for next-gen wearables, focusing on a custom Security Development Lifecycle for hardware, software, and cloud components in IoT ecosystems.
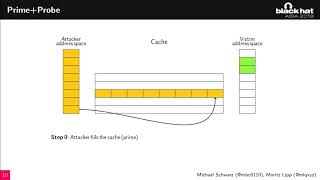
When Good Turns Evil - Using Intel SGX to Stealthily Steal Bitcoins
Explore how Intel SGX can be exploited to implement stealthy malware, extract secret RSA keys, and steal Bitcoins through cache attacks and other vulnerabilities in trusted execution environments.
ZombieLoad - Leaking Data on Intel CPUs
Explore ZombieLoad, a critical Intel CPU vulnerability. Learn about its mechanics, implications for data security, and potential exploits through demonstrations and insights.
Complexity Killed Security
Explore how increasing hardware complexity impacts software security, challenges in documentation access, and potential solutions for modern cybersecurity threats.
Hacking the Supply Chain - The Ripple20 Vulnerabilities Haunt Tens of Millions of Critical Devices
Exposición sobre vulnerabilidades críticas Ripple20 que afectan a millones de dispositivos IoT en diversos sectores, detallando su descubrimiento, impacto y explotación técnica.
Attacking iPhone XS Max
Explore iPhone XS Max vulnerabilities, including PAC implementation, XNU bug exploitation, and kernel read/write access. Learn about Unix Domain Socket, race conditions, and unprotected control flow transfer points.
Breaking Through Another Side - Bypassing Firmware Security Boundaries from Embedded Controller
Reverse engineering Embedded Controller firmware to bypass Intel BIOS Guard on Lenovo Thinkpads, exploring hardware security boundaries and firmware update processes.
Use-After-Use-After-Free - Exploit UAF by Generating Your Own
Explore a novel exploitation technique for UAF vulnerabilities in Adobe Flash, transforming them into multi-class type confusions for full memory access despite recent mitigations.
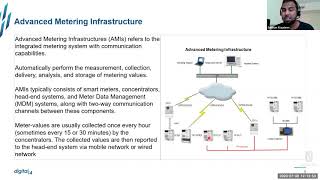
Insecurity of Smart Energy Meters - A Hardware Security Perspective
Explore hardware security vulnerabilities in smart energy meters, covering threat classifications, current trends, and testing methodologies for advanced metering infrastructure and grid security.
Silicon - Security's New Layer
Explore hardware security challenges, from supply chain vulnerabilities to chip-level attacks. Learn about emerging threats and best practices for securing technology stacks from silicon to software.
Testing Endpoint Protection - How Anyone Can Bypass Next Gen AV
Explore techniques to bypass next-generation antivirus software, learn about testing methodologies, and understand the effectiveness of endpoint protection solutions.
Security Orchestration and Incident Response
Explore cyber-resilience strategies in an uncertain world, integrating human expertise with machine learning for effective security orchestration and incident response.
Predator to Prey - Tracking Criminals with Trojans and Data Mining for Fun and Profit
Explore tracking techniques for stolen devices, from USB hacks to data mining, with ethical considerations and real-world case studies in digital forensics and cybersecurity.
Mill vs. Spectre - Performance and Security
Explore CPU architecture vulnerabilities, focusing on Meltdown and Spectre attacks. Learn about the Mill architecture's unique approach to performance and security without hardware speculation.
Level Up Your Concurrency Skills With Rust
Explore Rust's approach to safe concurrent programming, learning how it catches errors at compile time and enhances your skills across languages. Gain insights into race conditions and memory safety.
The Security of Classic Game Consoles
Explore classic game console security measures, their exploits, and lessons for modern software. Journey through gaming history to understand hardware, media, and software protection techniques.
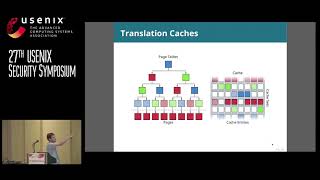
Malicious Management Unit - Why Stopping Cache Attacks in Software is Harder Than You Think
Explores indirect cache attacks bypassing software-based defenses by exploiting MMU operations, challenging existing security measures and revealing vulnerabilities in cache isolation techniques.