Cloud Native Security Whitepapers Overview
Overview of TAG Security's whitepapers and reference architectures for cloud native security, covering topics like supply chain security, zero knowledge, and security controls mapping.
Real-World Trust Management with Linkerd and Cert-Manager
Explore real-world trust management using Linkerd and cert-manager, enhancing security and reliability in cloud-native environments.
Addressing Evolving Threat Models in Cloud Security with Open-Source Software
Explore evolving cloud security threats and learn to address them using open-source solutions, focusing on practical strategies and real-world use cases for robust cloud-native security.
Cloud Native Application Authorization
Explore modern approaches to application authorization in cloud-native environments, focusing on security, scalability, and best practices for Kubernetes and CNCF projects.
Staring Into the Abyss With the Security Technical Advisory Group
Introduction to CNCF Security Technical Advisory Group, covering its charter, scope, and key initiatives like Security Reviews and Supply Chain Security Paper. Learn about cloud native security and how to get involved.
Insights from the Cloud Native Security Slam
Explore lessons from CNCF's Security Slam, focusing on best practices for securing the software supply chain and addressing remaining gaps in cloud native security.
Past, Present, and Future of Tetragon - First Production Use Cases and Future Trajectory
Explore Tetragon's journey from inception to v1.0, including production use cases, security challenges, and future goals. Learn how BPF-based security pitfalls were avoided and performance issues solved.
Flavors of Certificates in Service Mesh - The Whys and Hows
Explore various certificate deployment options in Service Mesh security, with demonstrations using Istio for scenarios like external management, SPIFFE integration, and 5G Telco Cloud security.
Securing Identity and Authorization in Microservices
Explore Transaction Tokens (TraTs) for securing microservices, enhancing user identity and context in call chains, and defending against various attacks in distributed architectures.
Open Policy Agent (OPA) Introduction and Deep Dive
Explore Open Policy Agent (OPA), a versatile policy engine for Kubernetes, service mesh, CI/CD, and infrastructure. Learn about its features, use cases, and recent updates in this informative session.
Cloud Native Application Threat Modeling and Adversary Emulation - Techniques and Tools
Explore threat modeling and adversary emulation techniques for cloud-native applications, including methodologies, tools, and strategies to identify and mitigate security risks in dynamic cloud environments.
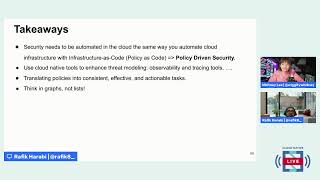
Cloud Native Application Threat Modeling and Adversary Emulation
Explore cloud native application security through threat modeling and adversary emulation techniques, enhancing your ability to identify and mitigate potential vulnerabilities.
Security Safari: A Journey Through the Wilderness of Securing Budding Opensource Projects
Explore essential security guidelines for open-source projects, distilled from CNCF and OpenSSF resources. Learn actionable steps to implement fundamental security measures from day one.
A Wind of Change for Threat Detection
Explore advanced cloud native security threat detection using eBPF and Falco, focusing on innovative approaches to create high-value kernel signals and leverage data analytics for behavior-based detection.
Building and Growing a Cloud Native Glossary for Japanese Developers
Explore the creation of a Japanese Cloud Native Glossary, its impact on developer communication, and insights into translating CNCF security documents for the Japanese community.
Reduce Security Alert Fatigue - Focus on What Matters
Learn strategies to prioritize and manage security alerts effectively, minimizing fatigue and focusing on critical issues in cloud-native environments.
The Quest for CNCF Ecosystem Security
Explore CNCF ecosystem security, focusing on open source project hygiene, TAG Security initiatives, and the Argo project's implementation. Learn strategies to enhance cloud native security and celebrate ecosystem progress.
A WASM Runtime for FaaS Protected by TEE
Explore confidential computing with WASM runtime for FaaS protected by TEE. Learn about Inclavare, cloud-native containers, and how WASM addresses cross-platform issues in secure cloud environments.
Creating Cloud Native Security
Explore cloud native security with experts from Apple, IBM, and VMware. Learn about CNCF's Security TAG initiatives, including supply chain security, project reviews, and community impact.
Cloud Native Application Security with Open Source
Explore cloud native app security risks, identification methods, and open-source tools for risk mitigation in developer-friendly environments. Learn to integrate security into workflows.
Fine-Grained Policies: RBAC with Next-Generation Access Control (NGAC)
Explore Next-Generation Access Control (NGAC) for fine-grained, policy-consistent authorization in cloud-native deployments, offering advantages over traditional RBAC and ABAC in Zero Trust contexts.