Cloud Native Security Landscape - Key Areas and Strategies
Explore key areas of Cloud Native security: platform protection, user management, and software supply chain. Gain insights into securing control planes, managing access, and mitigating threats in the cloud landscape.
Vulnerabilities and Misconfigurations in Cloud-Native Security - Two Sides of the Same Risk Coin
Explore cloud-native security risks, focusing on vulnerabilities and misconfigurations in modern applications. Learn proactive defense strategies for comprehensive protection across entire application stacks.
Practical Perimeter-less Authentication Solutions for Startups Using AWS Native Tools
Explore Zero Trust implementation for startups using AWS, focusing on ephemeral access management and cost-effective tools like SSM and Verified Access for robust cloud-native security.
Cloud Threats Through the Eyes of an Adversary - Evolving Tactics in Cloud Security
Explore how cybercriminals adapt tactics for cloud environments, leveraging unique vulnerabilities. Gain insights into advanced attack strategies and learn to develop proactive cloud-native security defenses.
Cloud Native Supply Chain Security: Beyond SBOMs - Perspectives and Practices
Insights on cloud native supply chain security beyond SBOMs. Experts discuss straightforward approaches, simple security practices, and future perspectives using open-source tools and frameworks.
Cloud Native Security - Cell-Based Architecture and Kubernetes
Explore Cell-Based Architecture for scalable, secure multi-tenant Kubernetes environments. Learn practical applications, real-world case studies, and how to enhance security, isolation, and performance using open-source technologies.
Fortifying AI Security in Kubernetes with Confidential Containers - CoCo
Explore confidential computing for AI model protection in Kubernetes using Confidential Containers (CoCo). Learn how CoCo enhances security for AI/ML workloads and provides memory protection for foundational platforms.
4 CI Security Best Practices to Prevent Cloud-Native Supply Chain Attacks
Explore security challenges in CI pipelines and learn best practices to prevent cloud-native supply chain attacks. Discover tips for securing GitHub Actions, GitLab Runner, and CircleCI workflows.

Securing Kubernetes Applications by Crafting Custom Seccomp Profiles
Learn to create custom seccomp profiles for Kubernetes workloads, enhancing container security. Explore manual and automated techniques, multi-architecture profiles, and in-cluster enhancements for application-specific security.
Towards the Hardened Cloud-Native Cornerstone: Container Runtime Protection
Explore advanced container runtime protection techniques, from kernel-aided to hardware-assisted solutions, addressing security risks and privacy concerns in cloud-native environments.
KubeClarity - Bringing Clarity to Kubernetes Artifacts Security
Discover how KubeClarity enhances security for Kubernetes artifacts, providing comprehensive visibility and protection for your cloud-native applications.
Bypassing Falco - How to Compromise a Cluster without Tripping the SOC
Explore techniques to bypass Falco's default ruleset, enabling stealthy cluster compromise. Learn 9 bypass classes for target enumeration, privilege escalation, and lateral movement without alerting security teams.
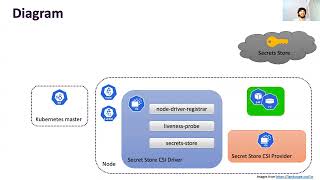
Secrets Store CSI Driver - Bringing External Secrets In-House
Explore how the Secrets Store CSI Driver enhances Kubernetes security by seamlessly integrating external secrets management systems with applications.
Cloud Native Live - Locking Down Your Cluster
Explore strategies for enhancing Kubernetes cluster security, including best practices, tools, and techniques to protect against vulnerabilities and unauthorized access.
Desktop to Deployment: Kubernetes Security with Checkov
Explore K8s security from desktop to deployment using Checkov. Learn about OS Top 10, CI monitoring, customization, and admission controllers for robust cloud-native security practices.
PolicyReport CRD - Managing Admission Control, Runtime, and Scan Reports
Explore PolicyReport CRD for standardized Kubernetes policy management. Learn about adapters for various engines and discover Policy Reporter's integration capabilities.
Komrade: An Open-Source Security Chaos Engineering Tool for Kubernetes
Explore Security Chaos Engineering (SCE) and its application in Kubernetes with Komrade, an open-source tool for proactively identifying system vulnerabilities through controlled experiments.
Tweezering Kubernetes Resources - Operating on Operators
Explore Kubernetes Operators' security risks, threat modeling, and best practices for secure implementation. Learn to assess third-party Operators and conduct effective code reviews for enhanced cluster safety.
Too Much to Choose - Making Sense of Kubernetes Security Standards
Explore Kubernetes security standards, their comparisons, and open-source tools for compliance assessment. Gain insights on choosing and implementing the right standards for your cluster.
Three Surprising Kubernetes Networking Features and How to Defend Against Them
Explore surprising Kubernetes networking vulnerabilities and learn effective defense strategies to protect your clusters from potential attacks and compromises.
Full Mesh Encryption in Kubernetes with WireGuard and Calico
Explore full mesh encryption in Kubernetes using WireGuard and Calico. Learn implementation details, benefits, and how to achieve data-in-transit security for compliance and zero-trust models.