Serverless Security and Functions-as-a-Service (FaaS)
Explore serverless security and Functions-as-a-Service (FaaS) with expert insights on potential risks, best practices, and implementation strategies for robust cloud-native applications.
Authorization in Microservices World - Kubernetes, ISTIO and Open Policy Agent
Explore fine-grained authorization in microservices using Open Policy Agent, integrated with Kubernetes and ISTIO. Learn challenges and solutions for enforcing programmatic authorization in cloud-native environments.
Automated Serverless Security Testing: Delivering Secure Apps Continuously
Explore serverless security risks, traditional testing limitations, and a new automated approach for secure serverless development without scripts or delays.
Open Policy Agent (OPA) Introduction and Deep Dive
Explore Open Policy Agent (OPA) for cloud-native policy enforcement. Learn about its applications, latest features, and integration with Kubernetes through OPA Gatekeeper.
Back to the Future - Next-Generation Cloud Native Security
Explore the future of cloud native security, examining emerging technologies, architectural patterns, and potential challenges. Gain insights into next-gen security pipelines and industry advancements.
Staring Into the Abyss with the Security Technical Advisory Group
Explore CNCF's Security TAG efforts, including security reviews, supply chain security, and community initiatives. Learn about cloud native security mechanisms and how to get involved.
Getting Familiar with Security Observability Using eBPF and Cilium Tetragon
Explore security observability using eBPF and Cilium Tetragon. Learn to extract data, monitor activities, and detect container escapes for enhanced incident prevention and response.
Red Light, Green Light: Traffic Security in the Service Mesh with Istio
Explore Istio's ingress and egress gateways for secure traffic management in service meshes, with real-world examples from Bloomberg's implementation for critical applications and ML workloads.
Cloud Native Application Security Governance Based on SBOM
Explore cloud-native app security governance using Software Bill of Materials (SBOM) for enhanced protection and compliance in modern software development.
Detecting Cloud and Container Threats - Kubernetes Security
Prepare, detect, and respond to security threats in containers and Kubernetes while maintaining agility. Learn to create perimeters, assess container content, and catch anomalies in fast-paced cloud environments.
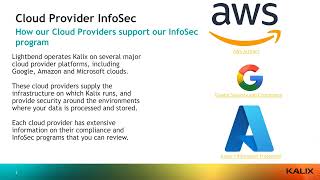
How to Secure Your Services with Kalix Security
Explore Kalix Security features to enhance service protection. Learn implementation strategies for robust security measures in cloud-native environments.
Cloud Native Live - What's New in Kyverno
Explore the latest features and updates in Kyverno, the policy engine for Kubernetes, enhancing security and compliance in cloud-native environments.
Modernizing Authorization in Cloud Native Environments
Explore modern authorization techniques for cloud-native applications, focusing on scalable and flexible solutions to enhance security and access control in distributed systems.
Introduction to Tetragon - CNCF Security Tool
Explore Tetragon, a powerful eBPF-based security observability and runtime enforcement tool for cloud-native environments.
Reshape Enterprise Cloud Native Security with Harbor and Narrows
Explore cutting-edge solutions for enhancing cloud native security in enterprise environments using Harbor and Narrows technologies.
Securing Requests with Keycloak and Istio through Request-Level Authentication
Explore request-level authentication using Keycloak and Istio to enhance security in cloud-native environments. Learn implementation techniques for robust access control.
What's New with Open Policy Agent Gatekeeper
Explore recent updates and advancements in Open Policy Agent Gatekeeper, enhancing Kubernetes security and policy enforcement capabilities.
Cloud Native Security Landscape - Myths, Dragons, and Real Talk
Explore cloud-native security across the software lifecycle, from open-source creation to runtime threat detection. Learn about key projects, developer-security team collaboration, and separating real risks from myths.
Cloud Native Security 101 - Building Blocks, Patterns and Best Practices
Explore cloud native security fundamentals, attack vectors, and best practices for implementing continuous security in cloud applications without compromising innovation.
Security Does Not Need to Be Fun - Ignoring OWASP to Have a Terrible Time
Explore OWASP's free tools for web application security testing and implementation. Learn to identify issues early and integrate security best practices throughout the software development lifecycle.
12 Essential Requirements for Policy Enforcement and Governance with OSCAL
Explore policy enforcement and governance in Kubernetes using OSCAL. Learn 12 key requirements for multi-cluster environments, focusing on security, compliance, and policy-as-code practices.