Lessons From Two Years of Crypto Audits
Explore fascinating security issues and risks in memory-safe languages like Rust, based on insights from two years of cryptocurrency audits.
MITRE ATT&CK - The Play at Home Edition
Learn how various cybersecurity teams can leverage MITRE ATT&CK framework to enhance threat tracking and protection strategies, with practical insights for immediate implementation.
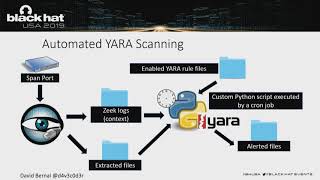
Detecting Malicious Files with YARA Rules as They Traverse the Network
Learn to detect malicious files using YARA rules and Zeek IDS for early-stage attack identification, enhancing network security with improved performance and targeted scanning techniques.
The Most Secure Browser? Pwning Chrome from 2016 to 2019
Explore Chrome browser security vulnerabilities and exploitation techniques from 2016 to 2019, presented by researchers who successfully pwned Nexus 6P in Mobile Pwn2Own 2016.
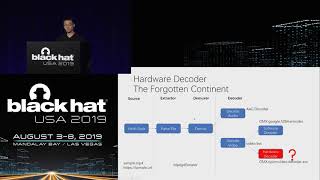
Bypassing the Maginot Line - Remotely Exploit the Hardware Decoder on Smartphone
Explore vulnerabilities in Qualcomm's Venus hardware decoder, learn its architecture, and discover remote exploitation techniques for smartphone security research.

How to Build Synthetic Persons in Cyberspace
Explore the development of AI agents simulating attackers and defenders in cybersecurity, enhancing training for both defensive and offensive roles in network security.
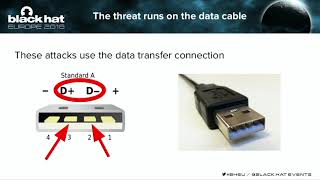
No Free Charge Theorem 2.0 - How to Steal Private Information from a Mobile Device Using a Powerbank
Exploiting hidden communication channels in smartphone charging to steal private data, despite Android's "Charging only" mode safeguards. Demonstrates vulnerability in public charging stations and powerbanks.
Zombie POODLE, GOLDENDOODLE, and How TLSv1.3 Can Save Us All
Explore advanced CBC padding oracle attacks, including a resurrected POODLE vulnerability and the faster GOLDENDOODLE attack. Learn how TLSv1.3 addresses these security issues.
Writing Trusted Applications in Rust
Explore using Rust for Trusted Applications, leveraging its security features like memory safety and error handling for system-level code development in secure environments.

Secure Boot Under Attack - Simulation to Enhance Fault Attacks & Defenses
Explore fault injection attacks on Secure Boot, their impact on embedded systems, and strategies for enhancing defenses through simulation techniques.
So I Became a Domain Controller
Explore Active Directory replication vulnerabilities, focusing on SAMBA implementation and mimikatz's DCSync feature. Learn techniques for extracting secrets and impersonating domain controllers.
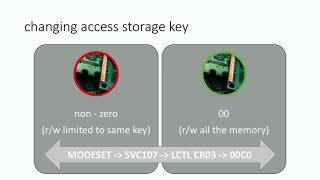
Mainframe Z-OS Reverse Engineering and Exploit Development
Explore mainframe security vulnerabilities, reverse engineering techniques, and exploit development for z/OS systems, challenging common assumptions about mainframe invulnerability.

SirenJack - Cracking a Secure Emergency Warning Siren System
Explore the SirenJack vulnerability affecting emergency warning sirens, its potential impact, and the surprisingly simple methods used to exploit this critical infrastructure weakness.
The Finest Penetration Testing Framework for Software-Defined Networks
Introducing DELTA: A powerful ONF-supported penetration testing tool for Software-Defined Networks. Learn about its capabilities and applications in enhancing SDN security.
Malware Buried Deep Down the SPI Flash - Sednit's First UEFI Rootkit Found in the Wild
Uncover Sednit's groundbreaking UEFI rootkit campaign, exploring its sophisticated techniques for deep system compromise and implications for cybersecurity in high-profile attacks.

Return of Bleichenbacher's Oracle Threat - ROBOT
Explore the resurgence of a critical TLS vulnerability affecting major vendors and websites, and learn why RSA PKCS #1 v1.5 encryption should be phased out.
New Norms and Policies in Cyber-Diplomacy
Explore evolving cyber-diplomacy landscape, discussing UN consultations, private sector initiatives, and potential new norms in international cybersecurity following 2016 negotiations collapse.
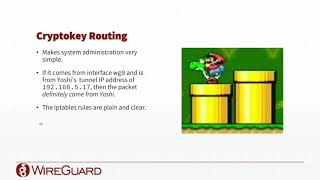
WireGuard - Next Generation Secure Network Tunnel
Explore WireGuard, a modern VPN protocol offering improved security, performance, and simplicity compared to traditional options like IPsec and OpenVPN. Learn about its innovative design and benefits.
A Deep Dive into macOS MDM - and How it Can Be Compromised
Explore macOS MDM vulnerabilities, including bootstrapping stages, IPC flows, and network security. Includes live demo of potential nation-state actor exploit on new Mac devices.
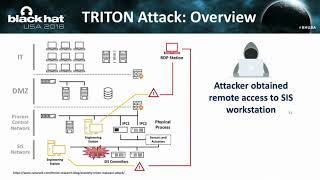
How TRITON Disrupted Safety Systems & Changed the Threat Landscape of Industrial Control Systems
Insights into TRITON attack framework targeting industrial safety systems, exploring its unprecedented impact on cyber-warfare and critical infrastructure protection. Analyzes implications for future threats.
Mental Health Hacks - Fighting Burnout, Depression and Suicide in the Hacker Community
Strategies for addressing mental health challenges in the hacker community, focusing on burnout, depression, and suicide prevention. Emphasizes the importance of recognizing and treating psychological issues.