Tales from the NOC - Going Public in Asia
Insider look at designing and securing Black Hat Asia's network infrastructure. Explore behind-the-scenes challenges, experiences, and evolving designs from the Network Operations Center team.
XOM-Switch - Hiding Your Code from Advanced Code Reuse Attacks in One Shot
XOM-switch: A security tool enabling XOM on Linux apps using PKU, protecting against code reuse attacks without source code or heavy binary rewriting. Enhances application security effortlessly.
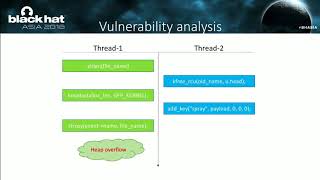
Breaking Android Kernel Isolation and Rooting with ARM MMU Features
Explore a new Android rooting solution, ReVent, exploiting a Use-After-Free vulnerability in 3.18 Linux kernels. Learn about breaking kernel isolation and ARM MMU features for device security.
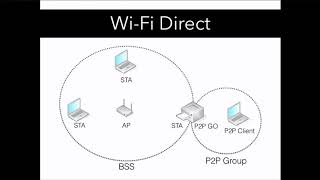
Wi-Fi Direct to Hell - Attacking Wi-Fi Direct Protocol Implementations
Explore Wi-Fi Direct vulnerabilities in Android, HP printers, and Samsung Smart TVs. Learn about protocol architecture, discovery, connection processes, and frame formats. Includes PoC and fingerprinting tool release.
Lost in Transaction - Process Doppelgänging
Explore Process Doppelgänging, a stealthy attack technique that evades security solutions. Learn its advantages over Process Hollowing and understand its detection challenges.
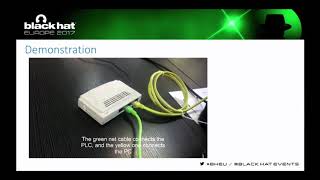
The Spear to Break the Security Wall of S7CommPlus
Unveiling vulnerabilities in S7CommPlus protocol, demonstrating potential security breaches in industrial control systems and proposing countermeasures for enhanced protection.
How to Hack a Turned-Off Computer, or Running Unsigned Code in Intel Management Engine
Explore vulnerability detection and exploitation in Intel Management Engine, bypassing protection mechanisms to run unsigned code on powered-off computers.
GDPR and Third Party JS - Can It Be Done?
Explore GDPR compliance challenges for third-party JavaScript, examining privacy implications and potential solutions for data protection in web development.
Remote Timing Attacks on TPMs - AKA TPM-Fail
Uncovers vulnerabilities in Trusted Platform Modules through timing analysis, revealing potential security risks in hardware-based cryptographic systems used across various computing platforms.
Operation Chimera - APT Operation Targets Semiconductor Vendors
Analysis of APT attacks on semiconductor industry, focusing on Taiwan. Explores threat actors, campaigns, and security status, highlighting potential global supply chain impacts.
Routopsy - Modern Routing Protocol Vulnerability Analysis and Exploitation
Explore vulnerabilities in dynamic routing and redundancy protocols, learn about common misconfigurations, and discover techniques for network attacks and discovery in this comprehensive analysis.
Industrial Protocol Gateways Under Analysis
Explore security vulnerabilities in industrial protocol gateways, examining cross-vendor issues and potential impacts on industrial facilities in the context of Industry 4.0 interconnectivity.
About Directed Fuzzing and Use-After-Free - How to Find Complex & Silent Bugs
Explore directed fuzzing techniques for targeted vulnerability detection, focusing on bug reproduction and patch-oriented testing to uncover complex and silent software flaws.
Virtually Private Networks
Explore the security implications of remote access solutions and VPNs for enterprise mobile workforces, examining potential vulnerabilities and challenges.
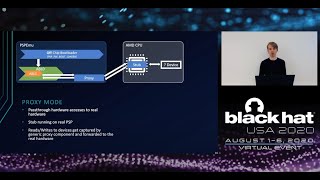
All You Ever Wanted to Know about the AMD Platform Security Processor and Were Afraid to Emulate - Inside a Deeply Embedded Security Processor
Explore AMD's Platform Security Processor: its role in system bootstrapping, security features, and proprietary nature. Gain insights into this embedded ARM core within x86 CPUs.
Black-Box Laser Fault Injection on a Secure Memory
Explore vulnerability research on the Microchip ATECC508A secure memory, examining laser fault injection techniques to bypass cryptographic authentication in IoT devices.
Escaping Virtualized Containers
Explore container escape techniques and new sandboxing tools using unikernels, lightweight VMs, and userspace-kernels to enhance isolation between host and container OS.
Portable Document Flaws 101
Dive deep into PDF's insecure features and vulnerabilities, exploring malicious capabilities affecting major viewers through systematic analysis and in-depth examination.
Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities
Explore a Safari exploit chaining six vulnerabilities to compromise the macOS kernel. Learn about offensive security research and browser-based kernel exploitation techniques.
Breaking Samsung's Root of Trust - Exploiting Samsung S10 Secure Boot
Exploración de vulnerabilidades en el arranque seguro de Samsung S10, analizando el manejo de solicitudes USB en S-Boot y sus implicaciones para la seguridad del dispositivo.
Lamphone - Real-Time Passive Reconstruction of Speech Using Light Emitted from Lamps
Explore a novel eavesdropping technique using light bulb vibrations to reconstruct speech in real-time, overcoming limitations of previous side-channel attacks for audio surveillance.