Story of Jailbreaking iOS 13
Explore the process and techniques of jailbreaking iOS 13, including kernel vulnerabilities and unauthorized code execution, presented by an expert at Black Hat conference.
EFIxplorer - Hunting for UEFI Firmware Vulnerabilities at Scale with Automated Static Analysis
Discover automated static analysis techniques for identifying UEFI firmware vulnerabilities at scale, addressing the lack of systemic approaches in x86-based systems research.
Precursor - Towards Evidence-Based Trust in Hardware
Explore evidence-based trust in hardware through the Precursor platform, challenging faith-based approaches and proposing new methods for verifiable hardware security.
The Evil of Spy Camera
Explore the structure, principles, and detection methods of spy cameras in this informative talk on combating hidden surveillance devices.
Walking Your Dog in Multiple Forests - Breaking AD Trust Boundaries through Kerberos Vulnerabilities
Explore Kerberos vulnerabilities in Active Directory forest trusts, revealing how attackers can breach trust boundaries in enterprise environments with multiple AD forests.
The Evil Alt-Ego - Abusing HTTP Alternative Services
Explore HTTP Alternative Services header vulnerabilities and potential exploits, including load balancing manipulation and client segmentation attacks.
Moving from Hacking IoT Gadgets to Breaking into One of Europe's Highest Hotel Suites
Explore tools and methods for hacking BTLE-based mobile phone key systems in hotels, from proof of concept to real-world application. Learn about vulnerabilities in IoT security and their practical implications.

Inside the Apple T2
Explore the inner workings of Apple's T2 chip, including methodology and tools for complex security research, going beyond publicly available technical details.
Women in Security - Building a Female InfoSec Community in Korea, Japan, and Taiwan
Explore how female InfoSec communities in Korea, Japan, and Taiwan are built, maintained, and overcome challenges to foster sustainable growth and attract new members.
Hacking Ten Million Useful Idiots - Online Propaganda as a Socio-Technical Security Project
Explore how online propaganda exploits socio-technical systems through data science, psychology, and security principles to influence millions of users.
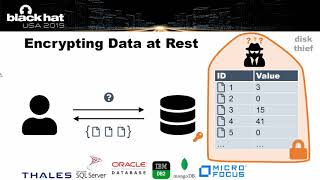
Breaking Encrypted Databases - Generic Attacks on Range Queries
Explore techniques for securely storing and querying outsourced data, focusing on range queries. Learn about common building blocks, commercial solutions, and potential vulnerabilities in encrypted databases.
Securing the System - A Deep Dive into Reversing Android Pre-Installed Apps
Explore techniques for analyzing pre-installed Android apps, including emulator challenges, component collusion detection, and privileged context behavior changes.
Paging All Windows Geeks – Finding Evil in Windows 10 Compressed Memory
Explore Windows 10 memory compression implementation, undocumented structures, and algorithms to enhance forensic tools for detecting malicious activities in compressed memory.

Process Injection Techniques - Gotta Catch Them All
Comprehensive overview of Windows process injection techniques for x64 systems, focusing on medium integrity processes without privilege elevation. Explores various methods and their implications.
DevSecOps - What, Why and How
Explore the transformation of DevOps into DevSecOps, covering open-source tools and cultural shifts needed for implementation, along with associated benefits and practical insights.
Controlled Chaos - The Inevitable Marriage of DevOps and Security
Explore DevOps basics, resilience, and chaos engineering. Discover factors behind elite organizations and how DevOps aligns with modern infosec goals in today's software-driven landscape.

Reverse Engineering WhatsApp Encryption for Chat Manipulation and More
Decrypting WhatsApp traffic and creating tools for vulnerability research, including a Burp Suite extension for investigating encrypted communications.
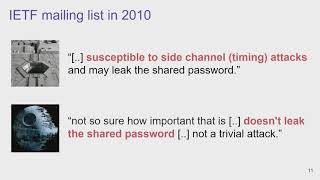
Dragonblood - Attacking the Dragonfly Handshake of WPA3
Uncover vulnerabilities in WPA3's Dragonfly handshake, including side-channel attacks and password partitioning techniques. Learn about design flaws and implementation issues affecting Wi-Fi security protocols.
Internet-Scale Analysis of AWS Cognito Security
Reveals findings from large-scale AWS Cognito security analysis, exposing vulnerabilities in identity pools granting access to thousands of S3 buckets, DynamoDB tables, and Lambda functions.
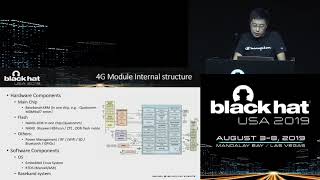
All the 4G Modules Could Be Hacked
Explores vulnerabilities in 4G modules, demonstrating methods to probe and exploit weaknesses in car entertainment systems for remote control of vehicles.
Responding to a Cyber Attack with Missiles
Explore the blurred lines between cyber and physical warfare, examining government responses to cyber attacks and the evolving rules of engagement in modern conflicts.