Evading Microsoft ATA for Active Directory Domination
Explore techniques to bypass Microsoft ATA's threat detection in Active Directory, covering reconnaissance, credential attacks, lateral movement, and persistence methods.
Exploit Kit Cornucopia
Explore creative techniques for detecting Exploit Kit infrastructure, including compromised websites, gates, and dedicated hosts, while understanding their underlying architecture.
Fad or Future - Getting Past the Bug Bounty Hype
Panel discussion on bug bounty programs: insights, challenges, and best practices from experienced program managers. Covers ROI, hunter interactions, and lessons learned for effective implementation and management.
Redesigning PKI to Solve Revocation, Expiration, and Rotation Problems
Explore PKI redesign for IoT security, addressing key revocation, expiration, and rotation challenges. Learn from real-world experiences and discover innovative solutions for robust device management.
Incident Response
Explore incident response and threat intelligence with Palo Alto Networks' SVP Wendi Whitmore, discussing cybersecurity consulting, ransomware trends, and prevention strategies.
The State of State Machines
Explore mobile security threats, the evolving landscape, and Zero Trust principles in this insightful discussion on protecting mobile devices and data.
Unleashing the Power of My 20+ Years Old Car
Explore automotive engine hacking, reverse engineering, and bypassing speed limiters in older vehicles. Gain insights into ECU communication, disassembly, and security vulnerabilities.
BluePill - Neutralizing Anti-Analysis Behavior in Malware Dissection
Explore BluePill, a customizable tool for neutralizing anti-analysis techniques in malware. Learn how it defeats evasive samples and executable protectors, enhancing malware dissection capabilities.
Real Eyes, Realize, Real Lies - Beating Deception Technologies
Explore weaknesses in deception technologies, learn tactics to overcome advanced techniques, and discover a new open-source tool for red teams to avoid traps during engagements.
Mac-A-Mal - An Automated Platform for Mac Malware Hunting
Automated platform for macOS malware analysis, featuring kernel-level behavioral monitoring and extending Cuckoo sandbox capabilities. Supports various sample types and detects evasion techniques.
Death by a Thousand Abstracts - How -Not- to Get Your Research into Black Hat
Discover key insights on crafting compelling research submissions for Black Hat and other industry events. Learn from common mistakes and best practices to increase your chances of being selected as a speaker.
The Risk From Power Lines - How to Sniff the G3 and Prime Data and Detect the Interfere Attack
Explore power line communication security, focusing on G3 and Prime standards. Learn to identify protocols, sniff data streams, and detect interference attacks in AMR systems.
New Tool for Discovering Flash Player 0-Day Attacks in the Wild from Various Channels
Discover techniques for identifying Flash player zero-day attacks in the wild, including sample collection methods and a tool for efficient detection with low false positives.
My Bro The ELK - Obtaining Context From Security Events
Automate security event analysis using ELK, Bro IDS, and threat intelligence feeds. Learn to integrate frameworks for faster incident response and enhanced threat detection.
Static Detection and Automatic Exploitation of Intent Message Vulnerabilities in Android
Explore Android app vulnerabilities, static analysis techniques, and automated exploitation methods for intent message flaws. Learn to identify and mitigate security risks in mobile app development.
Fingerprinting Web Application Platforms by Variations in PNG Implementations
Explore PNG implementation variations across web platforms for enhanced fingerprinting techniques in security audits, overcoming traditional methods and identifying platforms even with anti-fingerprinting measures.
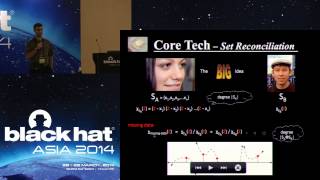
Say It Ain’t So - An Implementation of Deniable Encryption
Explore deniable encryption techniques, their applications, and implementation, focusing on set and string reconciliation methods for secure communication.
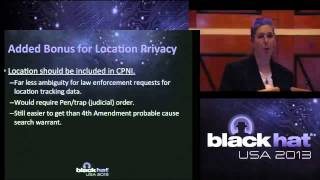
Beyond the Application - Cellular Privacy Regulation Space
Explore cellular privacy regulations, data collection practices, and potential changes in consumer protection, examining tensions between stakeholders and regulatory agencies.
Denial of Service as a Service - Asymmetrical Warfare at Its Finest
Explore DDoS attacks, investigative techniques, and asymmetrical warfare in cybersecurity. Learn about real-world incidents, tracking suspects, and the implications of "DDoS as a Service."
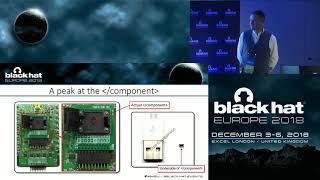
Attacking Hardware Systems Using Resonance and the Laws of Physics
Explore resonant frequencies to subvert electronic systems, challenging assumptions about hardware security and demonstrating vulnerabilities in supposedly secure components.
Return of the Insecure Brazilian Voting Machines
Análise detalhada da segurança do software de votação brasileiro, baseada em resultados de um desafio de hacking restrito organizado pela autoridade eleitoral nacional.