Alexa, Hack My Serverless Please
Explore serverless security risks, focusing on event injection attacks across various platforms. Learn to identify and mitigate vulnerabilities in cloud-based applications.
Tackling Privilege Escalation with Offense and Defense
Explore privilege escalation in JavaScript engines, focusing on offensive techniques and defensive strategies. Learn about vulnerabilities, attack surfaces, and security model improvements.
How to Break PDF Encryption
Learn techniques to break PDF encryption, analyze vulnerabilities, and understand the structure of encrypted documents for enhanced security awareness.
Implementing the Lessons Learned From a Major Cyber Attack
Explore lessons from Maersk's 2017 NotPetya cyber-attack, focusing on recovery strategies, resilient infrastructure, and evolving security principles for modern threats.
What the Fuzz
Explore cutting-edge fuzzing technologies, their potential, and future developments through demos, CVEs, and research insights from experts in the field.
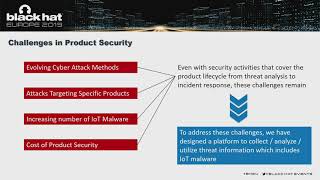
Understanding the IoT Threat Landscape
Explore IoT threat landscape, malware analysis, and Panasonic's approach to developing resilient products and an IoT SOC. Learn about security testing and the IoT Intelligence Platform.
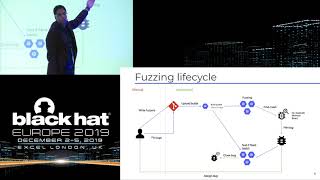
ClusterFuzz - Fuzzing at Google Scale
Explore Google's massive fuzzing infrastructure, ClusterFuzz, and learn how it finds thousands of security vulnerabilities across Google products and open-source projects.
Is Your Mental Health for Sale?
Explore the hidden world of data tracking on mental health websites, uncovering privacy risks and ethical concerns in online depression tests and advertising practices.

Reverse Engineering and Exploiting Builds in the Cloud
Explore security vulnerabilities in cloud-based CI/CD and container build environments. Learn about potential attack scenarios, remediation strategies, and best practices for securing the software supply chain.
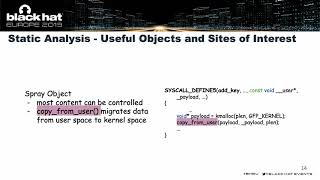
Hands Off and Putting SLAB - SLUB Feng Shui in a Blackbox
Automated memory layout manipulation technique for precise system call identification and assembly, enabling desired memory layouts for exploitation in SLAB/SLUB caches.
Doors of Durin - The Veiled Gate to Siemens S7 Silicon
Exploración detallada de la seguridad del PLC Siemens S7-1200, analizando su hardware, firmware y procesos de arranque para identificar vulnerabilidades y posibles vectores de ataque en sistemas de automatización industrial.
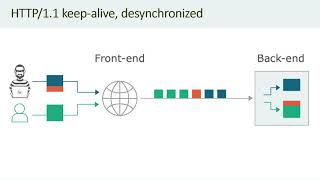
HTTP Desync Attacks - Request Smuggling Reborn
Explore HTTP request smuggling techniques to bypass security, manipulate web infrastructure, and exploit vulnerabilities. Learn detection, confirmation, and exploitation methods for various attack scenarios.
Far Sides of Java Remote Protocols
Explore critical flaws in Java RMI and CORBA protocols, uncovering vulnerabilities in vendor implementations and learning attack techniques for cross-process communications.
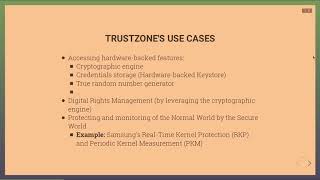
Breaking Samsung's ARM TrustZone
Explore Samsung's TrustZone vulnerabilities and learn techniques to exploit trusted components, execute high-privilege code, and bypass security measures in ARM-based systems.

Conducting a Successful False Flag Cyber Operation - Blame it on China
Explore techniques for conducting false flag cyber operations, including persona creation, toolchain analysis, and exploitation methods. Learn to understand and counter attribution attempts in cybersecurity.

Exploiting Qualcomm WLAN and Modem Over The Air
Explore Qualcomm WLAN and Modem vulnerabilities, focusing on firmware exploitation, isolation breaches, and over-the-air control techniques. Gain insights into real-time debugging and mitigation strategies.
Death to the IOC - What's Next in Threat Intelligence
Explore ML-driven automation for cyber threat intelligence, including custom entity extraction and attack pattern identification, moving beyond traditional IOC approaches.

WebAuthn 101 - Demystifying WebAuthn
Demystifying WebAuthn: Learn about its use cases, implementation, and future developments in web authentication, essential for any service implementing user login.
Fantastic Red-Team Attacks and How to Find Them
Explore prevalent gaps in organizational defenses through Atomic Red Team testing. Learn to identify and analyze complex attack patterns using Event Query Language and data analysis techniques.
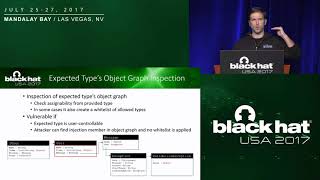
Friday the 13th - JSON Attacks
Explore JSON vulnerabilities, focusing on data libraries and serializers. Learn about attack vectors, classifications, and mitigation strategies for securing applications against JSON-based threats.
WiFuzz - Detecting and Exploiting Logical Flaws in the Wi-Fi Cryptographic Handshake
Explore techniques for detecting and exploiting logical vulnerabilities in Wi-Fi cryptographic handshake implementations, focusing on model-based testing and real-world examples.