Monitoring Surveillance Vendors - A Deep Dive into In-the-Wild Android Full Chains in 2021
Explore in-the-wild Android exploits discovered by Google's TAG and Android Security teams, including deep dives into CVE-2021-0920 and novel kernel exploitation techniques for bypassing hardware mitigations.
New Memory Forensics Techniques to Defeat Device Monitoring Malware
Discover new Volatility plugins for detecting device monitoring malware across major OS. Learn about advanced memory forensics techniques to combat sophisticated threats.
Unlimited Results - Breaking Firmware Encryption of ESP32-V3
Unveiling vulnerabilities in ESP32-V3 microcontrollers through hardware security evaluation, focusing on extracting firmware encryption keys to decrypt flash content containing potential secret data.
Backdooring and Hijacking Azure AD Accounts by Abusing External Identities
Explore Azure AD external identities, their vulnerabilities, and potential exploitation methods for backdooring and hijacking accounts in this informative cybersecurity presentation.
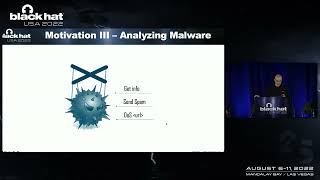
Automatic Protocol Reverse Engineering
Discover techniques for automatically extracting network protocol specifications from binary code, useful for security analysis, bug finding, and understanding botnet communications.
Pwning Cloud Vendors with Untraditional PostgreSQL Vulnerabilities
Explore PostgreSQL vulnerabilities in cloud services, including isolation issues and potential cross-account access attacks. Learn about real-world impacts and recent demonstrations of database security flaws.
Reverse Engineering the Tesla Battery Management System to Increase Power Available
Explore Tesla's Battery Management System reverse engineering, focusing on power upgrades in performance models. Learn about architecture, data structures, and hardware modifications for enhanced vehicle performance.
Ruling StarCraft Game Spitefully - Exploiting the Blind Spot of AI-Powered Game Bots
Explore techniques to exploit vulnerabilities in AI-powered game bots, focusing on StarCraft. Learn about deep reinforcement learning, adversarial attacks, and potential defenses in gaming AI.
Breaking VSM by Attacking SecureKernel
Explore vulnerabilities in Windows 10's SecureKernel, potentially compromising Virtualization-Based Security. Learn exploitation techniques and the process of finding and fixing critical security flaws.
Practical Defenses Against Adversarial Machine Learning
Explore real-world attacks on ML systems, from recommendation engines to email filters, and learn practical defense strategies against adversarial machine learning threats.
Detecting Access Token Manipulation
Demystifying Windows access token manipulation attacks and providing effective detection strategies for defensive practitioners in enterprise environments.
Mind Games - Using Data to Solve for the Human Element
Discover data-driven techniques to effectively reduce human risk in cybersecurity, challenging traditional training approaches and focusing on behavioral change strategies.
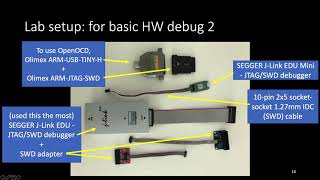
Finding New Bluetooth Low Energy Exploits via Reverse Engineering Multiple Vendors' Firmwares
Explore Bluetooth Low Energy vulnerabilities through firmware reverse engineering, uncovering remote code execution exploits at the protocol's lowest levels without authentication or pairing.
Election Security - Securing America's Future
Explore the US government's efforts to secure elections, including intelligence sharing, cybersecurity services, and collaboration with state and local officials to protect against malicious activities.
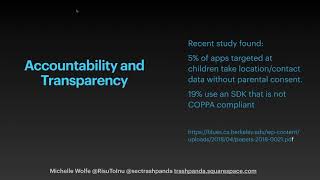
EdTech - The Ultimate APT
Explore the privacy and security risks of educational technology implementation in schools, highlighting concerns and potential actions for improvement.
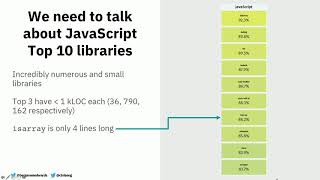
The Devils in the Dependency - Data Driven Software Composition Analysis
Análisis de datos sobre el uso de bibliotecas de código abierto en aplicaciones, examinando vulnerabilidades, dependencias y patrones de actualización para mejorar la seguridad del software.
Decisions and Revisions - The Ever Evolving Face of the Black Hat NOC
Explore the evolution of Black Hat's network operations, including equipment choices, regional adaptations, and cybersecurity insights from global events. Gain insider knowledge on network deployment and attendee behavior trends.
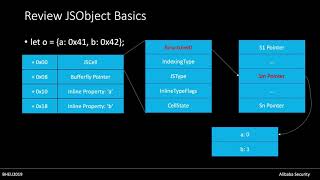
Thinking Outside the JIT Compiler - Understanding and Bypassing StructureID Randomization with Generic and Old-School Methods
Explore generic methods to bypass StructureID Randomization, gaining arbitrary Read/Write ability without relying on JIT compiler-related techniques. Learn innovative approaches to inspire better security mitigations.
Bypassing KPTI Using the Speculative Behavior of the SWAPGS Instruction
Unveiling a new speculative execution attack exploiting SWAPGS instruction, bypassing existing CPU and kernel protections. Explores side-channel vulnerabilities and their implications for system security.
Practical Side-Channel Attacks Against WPA-TKIP
Explore practical side-channel attacks against WPA-TKIP in Wi-Fi networks, analyzing vulnerabilities and countermeasures in this widely-used legacy protocol.
Fatal Fury on ESP32 - Time to Release Hardware Exploits
Methodical exploration of defeating ESP32 security features using low-cost hardware techniques, including voltage glitching and analog side-channels, with implications for IoT device security.