Sailing the Security Seas with Tetragon Tutorial
Explore Tetragon for runtime security: learn to filter and examine events, strengthen defenses against intrusions, and gain hands-on experience using the tetra CLI in this interactive tutorial.
From Observability to Enforcement: Lessons Learned Implementing eBPF Runtime Security
Dive into eBPF runtime security implementation, exploring the transition from observability to enforcement. Learn kernel-level security event collection, attack prevention strategies, and practical insights from the Tetragon team.

Comparing Kubernetes Security Agents: Falco, Tetragon and KubeArmor
Explore a detailed comparison of three leading eBPF-based Kubernetes security solutions, examining performance impacts, required privileges, and key features to make an informed choice for cluster protection.
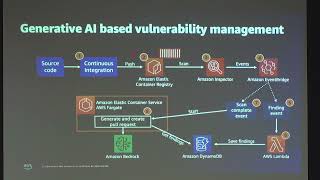
Applying Generative AI to Container CVE Remediation in CI Pipelines
Discover how to leverage generative AI for automating container vulnerability remediation in CI pipelines, with practical demonstrations and implementable solutions for efficient security management.
Protect Your Application with Zero Trust Superpowers Using OpenZiti
Discover how to embed zero trust security directly into applications using OpenZiti's SDK, moving beyond traditional network protection to create more secure, powerful software solutions.
Zero Trust and Runtime Security for Edge - Implementing Multi-Dimensional Protection
Discover how to implement Zero Trust security across application, network, and data dimensions for edge computing, addressing runtime challenges and automation requirements for effective protection.
Reinventing Seccomp with eBPF and KRSI for Enhanced Kernel Security
Explore how eBPF and KRSI can enhance Linux kernel security beyond traditional Seccomp capabilities, with practical demonstrations for implementing advanced syscall filtering in containerized environments.
Security Monitoring in Java Applications Using JDK Tools and JFR Events
Discover how to monitor Java application security using JDK Flight Recorder, Mission Control, and jcmd to track TLS protocols, security configurations, and X.509 certificates.
A Security Champion's Journey - Making Things A Bit More Secure Than Yesterday Every Day
Discover practical strategies for incrementally improving security in your organization through the lens of a security champion's daily experiences and lessons learned.
Securing with Love: A Philly Style Approach to Cloud Safety
Discover how security and development teams can collaborate effectively on cloud applications, focusing on practical steps like threat modeling, risk assessment, and maintaining robust security practices.
OWASP MASVS and Mobile App Security Threats - Understanding Resilience and Reverse Engineering in 2023
Explore mobile app security threats and defense strategies through OWASP MASVS framework, focusing on reverse engineering protection and resilience guidelines for modern application security.
Application Security in the Age of AI - Understanding Modern SSDLC and AI-Enhanced Security
Explore modern application security practices enhanced by AI, covering SSDLC implementation, threat modeling, secure coding, and runtime security for comprehensive software protection.
How Application Security Will Change with the Rise of AI
Explore how AI transforms application security practices, from enhancing threat detection to streamlining secure design, while understanding its limitations and the continued importance of human oversight.
Application Security and AI: Tools, Frameworks, and Implementation Techniques
Explore the intersection of AppSec and AI through practical tools, frameworks, and prompt engineering techniques for enhanced security implementation.
Maturing Your Application Security Program - A Practical Guide to Next Steps
Discover practical steps to advance your AppSec program through three maturity levels, with actionable strategies for immediate security posture improvements based on experience with 300+ companies.
Application Security Posture Management (ASPM) - Navigating Beyond the Hype Cycle
Discover practical insights into Application Security Posture Management (ASPM), learning to separate hype from reality and implement effective strategies that work for your organization's needs.

OWASP MASVS and Mobile App Security Threats - Understanding Resilience and Reverse Engineering in 2023
Explore mobile app security threats and defense strategies through OWASP MASVS framework, focusing on reverse engineering protection and resilience guidelines for modern applications.
How AI-Powered Tools Affect Application Security Practices and Benefits
Explore how AI-powered tools are transforming application security practices, maximizing development efficiency, and accelerating product delivery timelines.
API Security - Top 10 Essential Actions in 30 Minutes per Week
Discover essential API security priorities and high-impact actions to implement in time-constrained environments, focusing on preventing data breaches with maximum efficiency.
Modern AppSec vs. GenAI Applications - Is Your Security Program Ready?
Explore how traditional AppSec programs measure up against emerging GenAI security challenges, evaluating threat mitigation strategies and necessary program adaptations for AI-assisted development.
Generative AI Security: Top Considerations and Risk Mitigation Strategies
Explore essential security considerations for generative AI applications, covering risk mitigation strategies, data protection, prompt injection defense, and responsible implementation practices.