Trojan Source - Bad Characters Are Coming for Your Code
Explore invisible vulnerabilities in source code through encoding attacks, their impact on various systems, and practical defenses against this emerging threat vector.
Mother Nature vs Java - The Security Face Off
Explore biological analogies for application security, drawing inspiration from nature's defense mechanisms to enhance Java software protection and development processes.
Docker Security for Developers
Practical guide for developers on Docker security best practices, covering strong defaults, official images, least privilege, and microservices to enhance application security.
How to Get Properly Hacked
Live-coding session exploring common software development mistakes that lead to security vulnerabilities. Discover how to identify and prevent these issues to enhance application security.
Excellent Ways to Secure Your Spring Boot Application
Learn essential techniques to secure Spring Boot applications, including HTTPS, dependency scanning, CSRF protection, CSP implementation, OIDC authentication, and password hashing.
Finding Security Vulnerabilities Before They Find You
Explore live hacking techniques to identify and exploit vulnerabilities in open-source dependencies, with practical demonstrations and solutions for securing your applications.
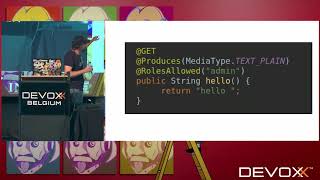
Secure Your Quarkus Applications
Explore options for securing Quarkus applications through live coding. Learn to implement crucial security and identity management features with ease and efficiency.
Stranger Danger - Finding Security Vulnerabilities Before They Find You
Discover techniques to identify and mitigate security vulnerabilities in open-source NPM modules, using real-world examples and practical demonstrations to enhance your application's safety.
AppSec is Too Hard
Explore common AppSec pitfalls, robust security approaches, and practical examples to improve application security and make it more manageable at scale.
Stranger Danger - Your Java Attack Surface Just Got Bigger
Explore cloud-native Java security risks, vulnerabilities, and best practices through live-hacking demonstrations, focusing on open-source dependencies and Docker images.
Why Building Your Ship with Raw Materials is a Bad Idea
Explore software bill of materials (SBOMs), open source compliance, and best practices for secure, robust application development in the face of new regulations and vulnerabilities.
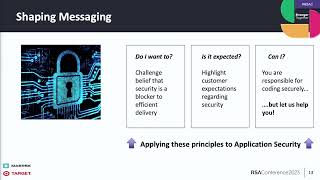
The Psychology of DevSecOps
Explore how DevSecOps teams apply psychological concepts to foster security-minded development cultures, increase collaboration, and cultivate buy-in from development partners.

Forget about OAuth 2.0. Here comes OAuth 2.1
Explore OAuth 2.1's simplified ecosystem, key differences from 2.0, and best practices for secure application architecture in this comprehensive overview.
Defeating EDR Evading Malware with Memory Forensics
Discover advanced memory forensics techniques to detect and analyze EDR-evading malware, including system call manipulation, module overwriting, and debug register abuse.
Applications and Cloud Hackers, Oh My!
Explore cloud security challenges, application vulnerabilities, and hacking techniques with experts Andrew Hay and Matt Johansen in this insightful BSidesLV presentation.
Techniques for Escaping the AppSec Labyrinth
Explore effective strategies for navigating complex application security challenges and overcoming obstacles in the ever-evolving AppSec landscape.
Securing the Future
Explore the evolution of application security and learn strategies to build secure, future-proof technology. Gain insights from Laura Bell's journey in AI and software development.
Sandboxing .NET Assemblies for Fun, Profit and of Course Security
Explore techniques for sandboxing .NET assemblies to enhance application security, limit third-party library risks, and create restricted environments for external modules using AssemblyLoadContext.
Developing and Deploying Containers and Microservices with Azure Container Apps
Simplify container deployment on Azure without Kubernetes complexity. Learn to set up, deploy, update, monitor, and secure containerized workloads using Azure Container Apps' serverless platform.
A Data Driven Approach to Application Security
Explore strategies for managing security alerts from multiple sources, aggregating data, and transforming information overload into actionable insights for both team and company-wide application security.
What the Log4j Incident Taught Us About Secure by Design
Exploring the Log4Shell vulnerability's impact on system design, this talk presents Secure by Design principles to mitigate similar threats and create more resilient applications.