Developers to the Rescue - How to Design Secure and Eco-Friendly Solutions
Explore strategies for designing secure and environmentally friendly software solutions, balancing cybersecurity with sustainability in modern development practices.
Everything New in Spring Security 6 Baked with a Spring Boot 3 Recipe
Explore the latest features and enhancements in Spring Security 6, integrated seamlessly with Spring Boot 3, to improve application security and streamline development processes.
How to Build a Secure Supply Chain for Your Spring Apps
Learn techniques to secure your Spring application's supply chain, enhancing overall software security and mitigating potential vulnerabilities in dependencies.
Securing RESTful Services with Spring HATEOAS and HDIV
Innovative approach to automate protection of Spring HATEOAS services against OWASP Top 10 security risks, integrating Spring HATEOAS with Hdiv security framework for RESTful service security.
Protection and Verification of Security Design Flaws
Explore protection against software design flaws using Spring applications and pentesting tools. Learn to identify, verify, and secure vulnerabilities beyond traditional automated detection methods.
Securing Spring Applications with Hashicorp Vault
Learn to secure Spring applications using Hashicorp Vault. Explore authentication, dynamic database credentials, TLS certificates, and secret management for enhanced application security.
From OWASP Top 10 to Secure Applications
Comprehensive overview of OWASP standards and practical security implementations for Spring applications, covering injection, access control, and various protection tools.
Leaving No Stone Unturned
Explore memory forensics techniques for digital investigations, covering attack methodologies and analysis steps. Learn to uncover hidden evidence in volatile memory samples for more comprehensive case insights.
Common Webapp Vulnerabilities and What to Do About Them
Explore common web app vulnerabilities and practical mitigations based on the OWASP Top 10 List, focusing on injection attacks, authentication issues, and data exposure risks.
Dynamic Polymorphism With Code Injection and Metaclasses
Explore advanced C++ techniques for dynamic polymorphism using code injection and metaclasses, offering alternatives to traditional virtual functions and inheritance for improved performance and flexibility.

Writing Viruses for Fun, Not Profit
Explore virus creation techniques, including self-replication and obfuscation, to understand system vulnerabilities and improve application security. Live PHP virus demos included.
The Art of Keeping Your Application Safe
Explore essential security practices for web applications, focusing on frontend vulnerabilities and protection strategies to safeguard your users and data.
Building Zero-Knowledge Backends
Explore Zero Knowledge Architecture for end-to-end encrypted applications. Learn to build secure backends with client-side encryption, ensuring data privacy and protection in modern app design.
The Security Toolbox for Node
Explore top Node.js security threats and learn practical tools to protect against vulnerabilities in dependencies, data, and servers. Gain a comprehensive security toolkit for robust application defense.
Threat Modeling Node
Learn threat modeling techniques for Node.js applications, enhancing security and identifying potential vulnerabilities in your code and infrastructure.
State of Node.js Security
Explore the current landscape of Node.js security, including vulnerabilities, best practices, and emerging threats in this informative talk by Vladimir de Turckheim.
Securing Your Application
Learn strategies for protecting applications in an open-source world, focusing on container security challenges and solutions from Docker's Security Lead.
Challenges in Developing a Large Django Site
Explore challenges and solutions for large-scale Django development, including signing, caching, API interactions, and best practices for improved performance and maintainability.
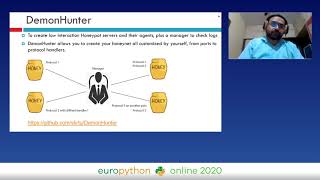
Deceptive Security Using Python
Explore deceptive security techniques using Python, including WebTrap and DemonHunter tools. Learn how to implement machine learning for XPath injection attack mitigation in web services.
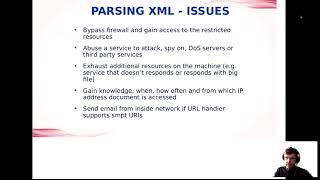
Python Security Best Practices
Discover essential Python security practices, covering input validation, XML parsing, assert statements, temporary files, and data serialization. Learn to identify vulnerabilities and implement robust defenses.
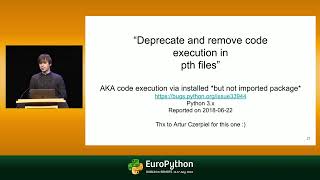
CPython Bugs and Risky Features
Explore security risks in CPython, including directory vulnerabilities, code injection possibilities, and socket issues. Learn about potential threats and mitigation strategies for Python developers and administrators.