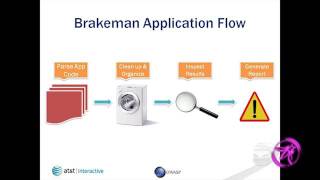
Brakeman & Jenkins - The Duo Detects Defects in Ruby on Rails Code
Explore static analysis tools for Ruby on Rails, focusing on Brakeman and Jenkins integration. Learn about security warnings, code updates, and best practices for detecting defects.
A DevOps View of AppSec
Explore DevOps history and its impact on AppSec, charting a path for DevSecOps success through standardization, automation, and Agile principles.
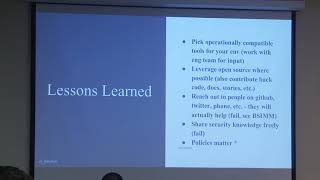
Building an AppSec Program from the Ground Up - An Honest Retrospective
Learn from a 2-year journey building an AppSec program, covering successes, failures, goal-setting, and execution. Gain insights on static analysis, threat modeling, metrics, and more for effective security implementation.
Adapting Your AppSec
Explore strategies for integrating application security into modern development processes without hindering progress. Learn about tooling, assessments, and agile methodologies for effective security implementation.
DevSecOps Without DevOps Is Just Security
Explore effective DevSecOps practices, emphasizing collaboration between security and DevOps teams. Learn prerequisites, case studies, and strategies for leveraging existing resources to enhance security integration.
AppSec Pipelines and Event-based Security - Moving Beyond a Traditional Security Test
Strategies for scaling AppSec programs using automation, continuous health checks, and event-based security to keep pace with rapid software development and delivery in large organizations.
Your Security Tools Are Just a Stop-Gap to Secure DevOps
Secure DevOps: Beyond tools, focus on risk assessment, threat modeling, and custom security controls. Learn to integrate security effectively in CI/CD pipelines for robust application protection.
Be Mean to Your Code - Rugged Development & You
Pragmatic approaches and tools for ruggedizing your development lifecycle, from code commit to running system. Learn solutions for secure, resilient applications in fast-paced environments.
Rugged Software Engineering
Practical strategies for rapid and secure software development, addressing challenges in modern engineering organizations and emphasizing rugged software practices.
Getting Security Up to Speed with CI - CD
Automating security in CI/CD: Learn about Threadfix-Centric Application Security Architecture, challenges in AppSec testing, and leveraging QA regression for enhanced coverage.
OWASP Flagship Projects - OWASP Dependency-Check
Learn to identify and mitigate vulnerabilities in software dependencies using OWASP Dependency-Check, enhancing application security through effective composition analysis.
OWASP Flagship Projects - OWASP DefectDojo
Learn about OWASP DefectDojo, an open-source application security management tool. Explore its features, automation capabilities, deployment options, and community-driven development.
Lessons Learned from the DevSecOps Trenches
Panel discussion on scaling AppSec programs, featuring insights from security leaders at major tech companies. Covers high-ROI efforts, effective tools, and lessons learned to help organizations improve their security practices.
Working with Developers for Fun and Progress
Practical strategies for building strong relationships with developers to create an impactful AppSec program, featuring competition-based training, tooling implementation partnerships, and codebase contributions.
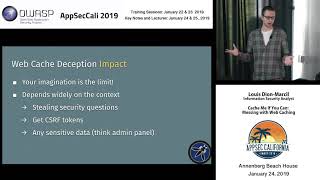
Cache Me If You Can - Messing with Web Caching
Explore web caching vulnerabilities including Web Cache Deception, Edge Side Include Injections, and Web Cache Poisoning. Learn detection techniques and mitigation strategies for these emerging threats in application security.
Remediate The Flag - Practical AppSec Training Platform
Hands-on platform for developers to find and fix security vulnerabilities in code. Offers real-time feedback, scoring, and customizable exercises to improve application security skills.
How to Get the Best AppSec Test of Your Life
Learn strategies to maximize the value of AppSec testing, from tailoring tests to your needs to ensuring actionable reports, for both defenders and breakers in application security.
Human Factors That Influence Secure Software Development
Explores human factors influencing secure software development, including environmental conditions, developer characteristics, and team dynamics. Discusses strategies to identify and mitigate vulnerability-prone code before issues arise.
Battle Tested Application Security
Insights on building effective Application Security programs, focusing on security culture, defensive capabilities, and organizational empowerment across different environments.
Serverless Infections - Malware Just Found a New Home
Explore serverless security risks through a live demo of RCE attacks, data infiltration, and self-duplicating malware in cloud environments. Learn best practices for securing serverless architectures.
Deserialization - What, How and Why Not
Explore insecure deserialization risks, vulnerabilities, and prevention techniques through code examples and live demos, focusing on Java but applicable to other languages.