Verifying and Synthesizing Constant-Resource Implementations with Types
Explores a type system for verifying constant-resource implementations, enhancing security against side-channel attacks while allowing natural programming models. Introduces resource-aware noninterference and automated repair techniques.
Introduction to Falco - Cloud-Native Runtime Security
Explore Falco, the open-source cloud-native runtime security project for Kubernetes threat detection. Learn installation, rules, Kubernetes integration, and advanced features like userspace implementation.
Cryptography: How Its Usage Affects Protection - 2018
Practical advice on proper cryptography usage in software and systems, covering design techniques, implementation best practices, and common pitfalls to avoid for secure application development.
The Eye of Falco: Detecting Container Escape Techniques with Linux Capabilities
Explore container security vulnerabilities and learn how Falco can detect and respond to container escape techniques based on Linux capabilities, with real-world CVE examples.
From Security Testing to Deployment in a Single Pull Request
Automating cloud native app development with integrated security testing, from building and scanning to packaging and deployment, all within a single pull request for consistency and efficiency.
Verifiable GitHub Actions with eBPF
Explore eBPF-based solution for securing GitHub Actions pipelines against supply chain attacks, featuring runtime security profiling and build verification techniques.
Kubernetes Defensive Monitoring with Prometheus
Explore innovative uses of Prometheus for defensive monitoring in Kubernetes, complementing traditional security tools. Learn practical examples and ready-to-use strategies for enhancing your cluster's security posture.
Interactive Playground to Learn Kubernetes and Cloud Native Security
Explore Kubernetes security through hands-on scenarios in a vulnerable cluster environment. Learn about real-world vulnerabilities, CVEs, and security tools across infrastructure, supply chain, and runtime layers.
Using OpenTelemetry for Application Security - A Real-Life Example
Explore OpenTelemetry's role in securing cloud-native applications. Learn how to detect vulnerabilities in microservices architectures through a practical Kubernetes example and Jaeger visualization.
Falco: Cloud-Native Runtime Security for Kubernetes - Recent Developments and Roadmap
Discover Falco: Cloud-Native Runtime Security for Kubernetes. Learn about recent developments, improved eBPF support, security enhancements, ecosystem integrations, and the project's roadmap from experienced contributors.
Cryptographic Agility: Preparing Modern Apps for Quantum Safety and Beyond
Explore cryptographic agility for modern apps, focusing on quantum safety. Learn strategies for seamless transitions between cryptography standards and preparing for future cryptographic migrations.
Verifiable GitHub Actions with eBPF
Explore eBPF-based solution for securing GitHub Actions pipelines against supply chain attacks. Learn about runtime security, build profiling, and verification techniques to protect your software development process.
Prometheus and Falco: The Swiss Army Knife for SREs - Cloud Native Live
Explore how Prometheus and Falco empower Site Reliability Engineers with robust monitoring, alerting, and security capabilities for cloud-native environments.
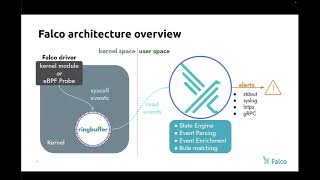
Detecting Five Famous Exploits with Falco
Explore real-world cybersecurity threats and learn to detect them using Falco, enhancing your ability to protect cloud-native environments from sophisticated attacks.
DevOps, CI, APIs, and Security Gone Agile
Explore agile security practices for modern IT environments, covering infrastructure, apps, APIs, and source code. Learn to adapt security processes to rapid deployment cycles and DevOps methodologies.
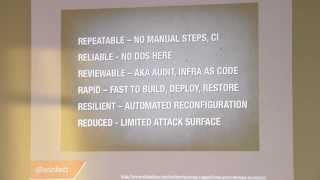
DevOps for the Discouraged - Integrating Security into Continuous Delivery
Equipping security teams with tools and strategies to integrate into DevOps practices, focusing on continuous delivery pipelines and open-source security tools for web application stacks.
Ground Truths of a Rugged DevOps Practitioner
Explore DevOps from a practitioner's perspective, uncovering lessons learned, surprises, and future plans in application security. Interactive discussion on real-world experiences and best practices.
Where the Security Rubber Meets the DevOps Road
Explore DevOps evolution, its integration with security practices, and implementation strategies for organizations. Learn from real-world experiences in adopting DevOps patterns and toolchains.
Why Infosec Needs Rugged DevOps Now - A Study of High Performing IT Organizations
Explore how Rugged DevOps integrates security into high-velocity IT environments, enabling scalable, secure applications while maintaining agility and competitive advantage.
Skip the Anxiety Attack - Build Secure Apps with Docker and Kubernetes
Learn to build secure applications using Docker and Kubernetes, reducing anxiety and enhancing your development process with industry-leading containerization and orchestration technologies.

Using Docker to Secure Traditional Applications Without Code Changes
Modernize legacy applications with Docker for enhanced security, portability, and cost-efficiency without code changes. Learn isolation, encryption, scanning, and signing techniques to reduce attack surfaces and manage threats.